ISPs 'likely' helped infect targets of state surveillance
Full article615 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
A spying tool known as FinFisher is involved in a seven-country campaign that most likely involves "complicit" internet providers helping to infect targets of surveillance, according to researchers with the cybersecurity firm ESET.
A spying tool known as FinFisher is involved in a seven-country campaign that most likely involves “complicit” internet providers helping to infect targets of surveillance, according to researchers with the cybersecurity firm ESET.
“In two of the campaigns, the spyware has been spread via a man-in-the-middle attack and we believe that major internet providers have played the role of the man in the middle,” Filip Kafka, the ESET malware analyst who conducted the research, explained.
This falls directly in line with FinFisher’s own marketing material which boasts it collaborates with internet service providers to distribute malicious files.
ESET declined to name the countries or internet providers involved in the unprecedented scheme. The reason is “so as not to put anyone in danger,” the company said.
Downloading a popular targeted application led users to be redirected to a malicious server hosting spyware enabling keylogging, file exfiltration and real-time surveillance.
“The most important innovation is the way in which the surveillance tool is delivered to targeted computers,” ESET’s researchers said. “When a user is about to download Skype, Whatsapp or VLC Player, they are redirected to the attackers’ server; there, they are served a Trojanized installation package infected with FinFisher. Other applications ESET have seen being misused to spread FinFisher include Avast and WinRAR.”
Two apps called Threema and TrueCrypt, a popular secure messenger and disk encryption software, were switched out for a version infected by FinFisher, suggesting targeting of privacy-minded users as well.
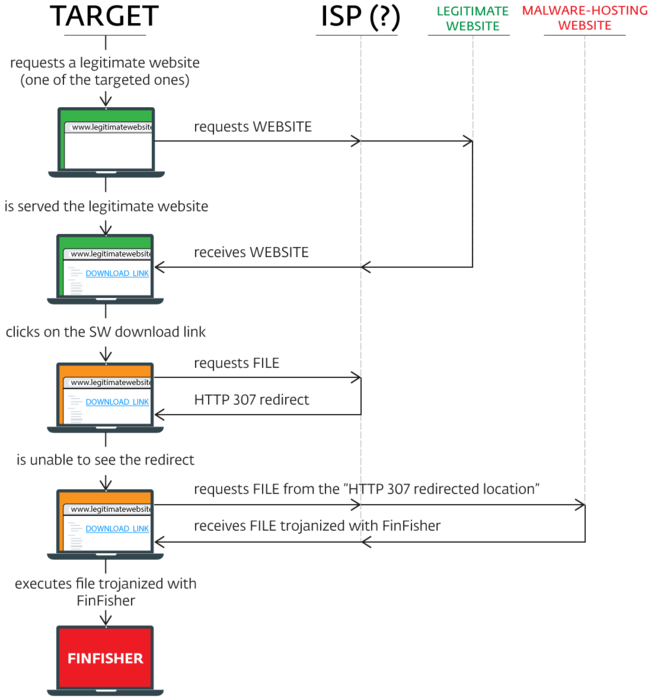
“It would be technically possible for the ‘man’ in these man-in-the-middle attacks to be situated at various positions along the route from the target’s computer to the legitimate server (e.g. compromised Wi-Fi hotspots),” the researchers explained. “However, the geographical dispersion of ESET’s detections of latest FinFisher variants suggests the MitM attack is happening at a higher level – an ISP arises as the most probable option.”
FinFisher is spyware sold to governments around the world. The German company behind the software has embarked on a permanent sales campaign including a stop at the upcoming surveillance tradeshow ISS World in Kuala Lumpur in December.
Speaking exclusively to government officials, FinFisher’s researchers will speak for three hours on topics including the company’s newest hacking technology — and no doubt hope to sign a few lucrative contracts as well.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/finfisher-isp-hijack-eset/