Kido, you ain’t kidding
Full article226 words · extracted from securelist.com · click to collapse



On January 13th we raised the alert level for the Kido family to orange: moderate risk. It’s been quite a while since an ‘old school’ network worm has caused such a stir – Kido’s managed it by not only relying on critical Windows SMB vulnerabilities to spread but it also bruteforces weak passwords in order to gain access to other machines in a local network.
Because of this (along with a few other things) Kido can be very painful to get rid of. That’s why we’ve decided to release a free tool which can be used to clean infected machines.
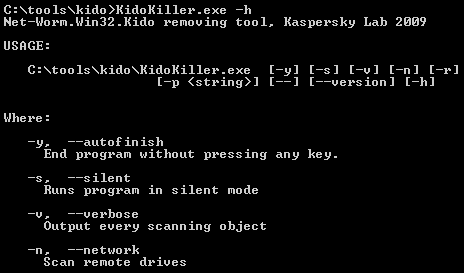
You can grab our KidoKiller tool here.
Feel free to give it a try.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/kido-you-aint-kidding/30479/