DoppelCart fraud network uses 119,000 fake shops to steal credit cards
DoppelCart, the largest documented fake-shop network, runs 119,000 domains impersonating 44,182 brands to steal payment card details via WebSocket-connected checkout pages.
German cybersecurity startup Nebty discovered DoppelCart, a network of more than 119,000 fake e-commerce domains, mostly in the .SHOP TLD, that harvest payment card details through fraudulent checkout pages. Over 105,000 shops remain active, impersonating 44,182 brands with discounts of up to 65%, and 96% of confirmed shops share identical build files resolving to 27 commerce backends. Checkout code exfiltrates card numbers, expiration dates, CVVs, cardholder names, contact details, and even bank one-time codes to attacker C2 over WebSockets in real time, potentially bypassing bank security controls. The network surpasses BogusBazaar, the previously largest documented fake-shop cluster with 75,000 sites and an estimated 850,000 fraudulent transactions.
- 105,000+ shops are still active; 96% share identical build files and resolve to 27 commerce backends.
- Impersonates brands like SodaStream, Daniel Wellington, and CurrentBody with over 30 clone shops each.
- Checkout code relays bank one-time confirmation codes, potentially bypassing transaction security checks.
- Some stores display the real brand's support address, sending victims to the impersonated company.
- Nebty launched a searchable database to help brands detect DoppelCart impersonation and abuse.
Full article411 words · extracted from bleepingcomputer.com · click to collapse
A massive operation dubbed “DoppelCart” uses more than 119,000 domains to run a network of fake e-shops that steal payment card details.
Most of the domains are in the .SHOP top-level domain, accounting for 2.72% of all sites on the TLD.
German cybersecurity startup Nebty discovered DoppelCart and describes it as the largest publicly documented fake-shop cluster by domain count, far surpassing the second-largest, “BogusBazaar,” which operated a network of 75,000 sites that recorded an estimated 850,000 fraudulent transactions.
The company's latest scans show that more than 105,000 DoppelCart shops are still active.
Nebty CEO Benedikt Scheungraber told BleepingComputer that 96% of the shops confirmed to be part of DoppelCart share identical build files and resolve to 27 commerce backends.
The sites impersonate legitimate businesses by copying product catalogs, descriptions, branding, and images, sometimes loading assets directly from the real company’s servers.
Scheungraber says that the shops mimic 44,182 different brands, with a median of two clones for each.
However, some brands like SodaStream, Velasca, CurrentBody, Daniel Wellington, Dreame, Horze, MOVA, and SPARK PAWS received more attention, with over 30 shops each.
The fake sites advertise big discounts of up to 65% in many cases to lure bargain-hunting shoppers.
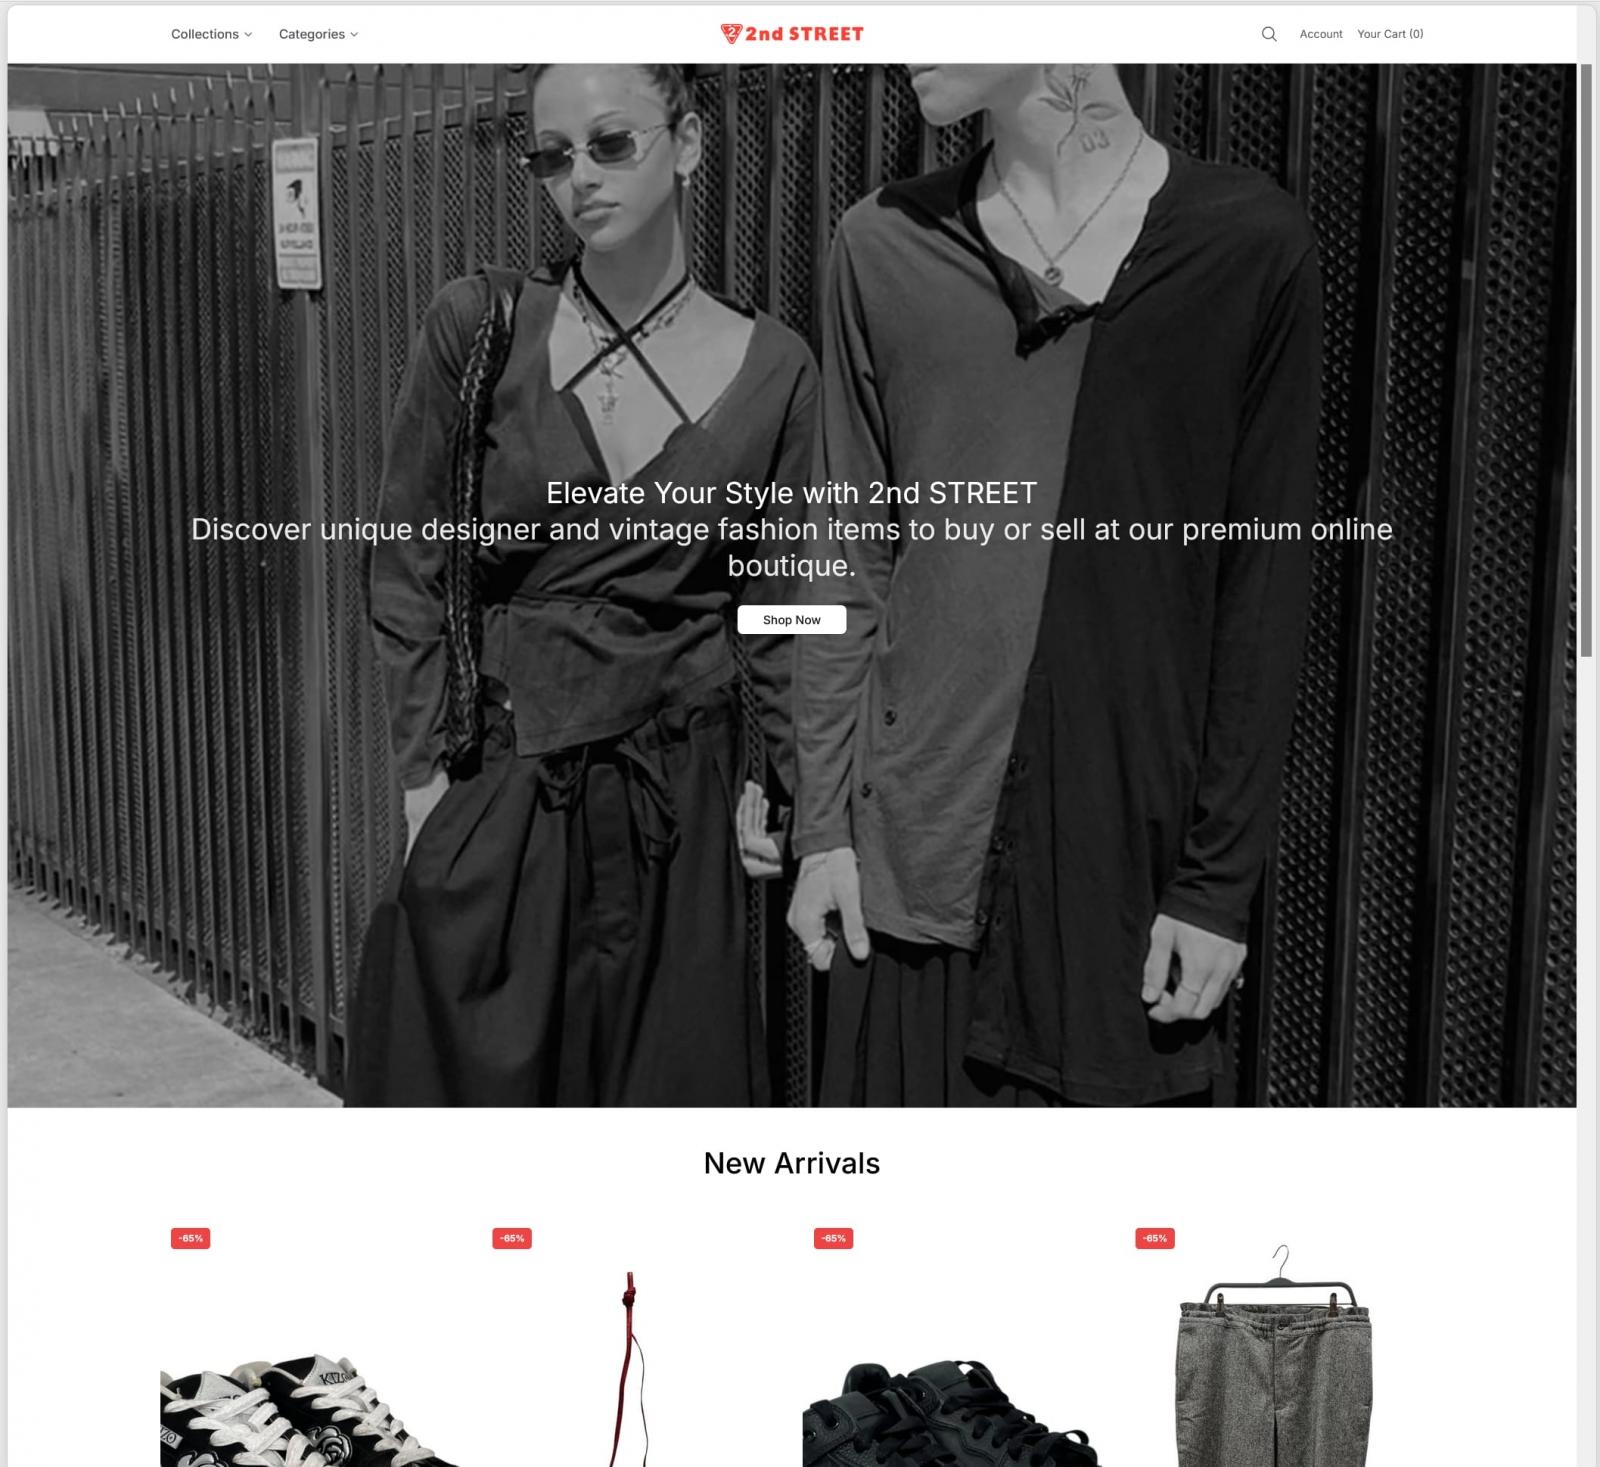
Source: BleepingComputer
When testing several checkout pages in the DoppelCart cluster, Nebty found code that collected sensitive information related to payment cards and their holders:
- Card numbers
- Expiration dates
- Security codes
- Cardholder names
- Email addresses
- Phone numbers
- Physical addresses
Each data field is transmitted over WebSockets to the command-and-control (C2) in real time, Netby says in a report shared with BleepingComputer.
The checkout code can also relay the one-time confirmation code issued by a victim’s bank, which the attackers may use to bypass security protections.
Nebty says some of the fake stores show the impersonated brand’s legitimate support address, leading victims who didn’t receive their purchases to contact the real company.
Scheungraber says that the company tried to contact the main hosting provider for DoppelCart sites but received no response.
Separately, Nebty created a searchable database to help companies identify DoppelCart impersonation and brand abuse and take appropriate action to protect themselves.
Once attackers have valid credentials, only 37% of their actions are blocked
Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.bleepingcomputer.com/news/security/doppelcart-fraud-network-uses-119-000-fake-shops-to-steal-credit-cards/