Koobface on the tweet
Full article258 words · extracted from securelist.com · click to collapse



We are currently witnessing a new wave of Koobface messages flooding twitter. The message that is mostly used right now is: “My home video 🙂 <URL>”
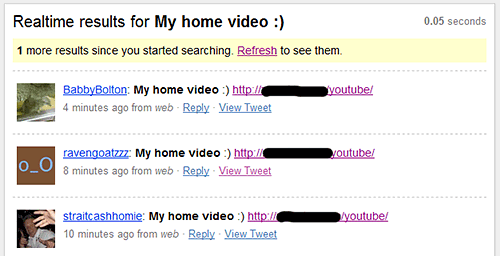
The link in infected tweets points to a site with a little javascript.
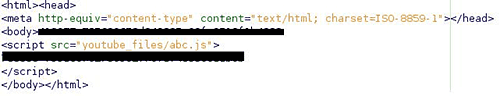

The script calls a php-script on a server which uses an ID to return an IP address leading to the video site. This means the IP address is different for every request.
Interestingly, the guys behind this attack are clearly out to maximize their ROI: if you’re using Mac or Linux, you end up getting redirected to an adult site.
Twitter is saying it may block infected accounts. We’re doing our part as well – our users are already protected from the malicious file:
And we’ve also added protection against the malicious tweet itself, which will be detected as Net-Worm.Win32.Koobface.aqy as updates are rolled out to our users.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/koobface-on-the-tweet/30531/