Paris Hilton spam
Full article356 words · extracted from securelist.com · click to collapse



Last week there was a lot of speculation going round that Paris Hilton has changed her sexual orientation. A couple of years ago when she was making the news, IM-Worm authors played on this. With these latest rumours – I am an AV researcher after all – I immediately thought that the bad guys would find some way to use these rumours. Unsurprisingly, this prediction turned out to be true. Over the last couple of days we’ve seen spam being sent out which contains a link in it claiming to be a Paris Hilton video.
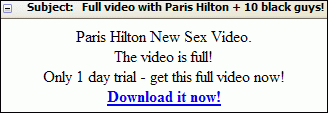
The social engineering is obvious – although it’s amusing that the video title mentions men rather than women. Putting this aside, it’s rather an odd case from a technical point of view.
The URL leads to a simple Trojan-Downloader which is packed using FSG. It doesn’t have any anti-AV functionality. In turn the Downloader downloads two files, one for harvesting email addresses from the victim machine and one for sending out spam. One of those is stuffed with anti-AV techniques.
Of course, using Trojan-Downloaders is extremely common these days. What’s strange is the combination of such a simple Trojan-Downloader which downloads highly sophisticated malware.
And given that the Trojan-Downloader will be heuristically detected by quite a number of virus scanners, including ours, the chances of actually getting infected are slim. This leaves me wondering if this unusual combination was created by the authors by accident, or by some strange design.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/paris-hilton-spam/30398/