Wyden demands answers from telecom giants, NSA over SS7 vulnerabilities
Full article730 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Oregon Senator Ron Wyden is demanding to know how America's largest telecommunications companies plan to stop hackers from exploiting vulnerabilities in an outdated mobile-data transfer framework that remains fundamental to how cellphones function.
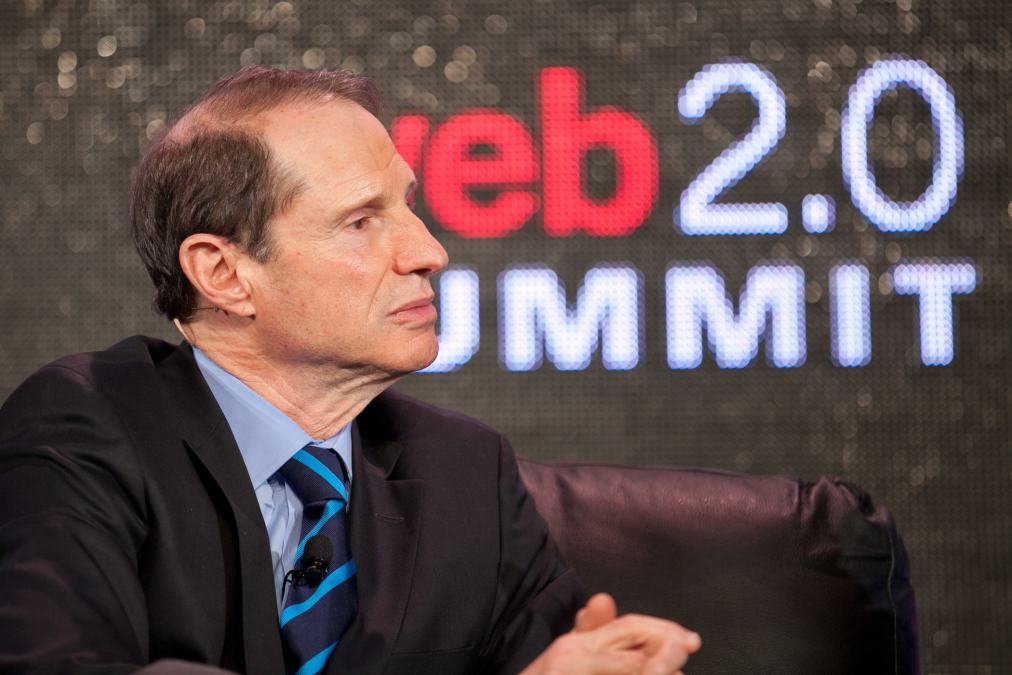
Sen. Ron Wyden, D-Ore., is demanding to know how America’s largest telecommunications companies plan to stop hackers from exploiting vulnerabilities in an outdated mobile-data transfer framework that remains fundamental to how cellphones function.
Wyden sent a series of letters Thursday to the chief executives of AT&T, Sprint, Verizon and T-Mobile to learn about their efforts to mitigate risks associated with weak points in Signaling System No 7, or SS7, a set of protocols that allow for different mobile phone networks to connect to one another. In addition, he also sent a letter to the NSA director, Adm. Michael Rogers, requesting information about past attempts by adversaries to hack into SS7 for the purpose of spying on Americans, including military personnel, civilians and companies.
The Daily Beast was the first to report on Wyden’s multiple letters.
There are well-known security issues with SS7, including reported cases of intelligence agencies exploiting vulnerabilities in the framework to remotely eavesdrop on targets through their cellphones. Governments, cybercriminals and defense contractors continue to be interested in attacking the framework because of the access it provides to a continuous flow of communications, data, records and the locations of specific devices. By breaching SS7, a hacker would be able to access GPS data to track down an individual.
“I understand that some wireless carriers are further along in the process of implementing protections against SS7 attacks than others. However, information about the progress that each carrier has made, and the extent to which their customers remain vulnerable to SS7 spying is not currently available to the general public, nor even to DHS,” the letters read. “The continued existence of these vulnerabilities and the ease with which they can be exploited by hackers and foreign governments poses a serious threat to U.S. national and economic security.”
The letters are the latest in a broader effort, largely pioneered by Wyden and Rep. Ted Lieu, D-Calif., to inform the public on the existing security issues behind SS7, which was developed in 1975.
Wyden’s letters specifically ask for information about whether AT&T, Sprint, Verizon and T-Mobile have hired outside help to review threats to SS7; how they’ve worked with the Homeland Security Department to date on the issue; and details about how certain vulnerabilities in SS7 could negatively impact customers if a breach were to occur.
Multiple federal agencies, including most recently DHS and the FCC, have published reports focused on the security issues underpinning SS7. DHS, for example, earlier this year noted that there is a realizable threat to SS7 from hackers because “there are tens of thousands of entry points worldwide, many of which are controlled by countries or organizations that support terrorism or espionage.”
Wyden’s request calls for companies to respond before Oct. 13 to his questions.
You can read the letters here:
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/wyden-demands-answers-telecom-giants-nsa-ss7-vulnerabilities/