Hackers target WordPress sites via third-party WooCommerce plugin
Attackers exploit unauthenticated file-upload flaw CVE-2026-27540 in WooCommerce Wholesale Lead Capture plugin to install PHP webshells; Wordfence blocked 100,000+ attacks.
CVE-2026-27540 is an unauthenticated arbitrary file-upload vulnerability in the WooCommerce Wholesale Lead Capture premium plugin (versions 2.0.3.1 and older), caused by the exposed wwlc_file_upload_handler AJAX action trusting a user-controlled file_settings allowlist. Discovered by researcher Teemu Saarentaus, it was fixed in version 2.0.3.2 released February 20. Defiant reports Wordfence blocked over 100,000 attacks, with exploitation spikes between June 4-17, July 1, and August 30, delivering shell.php webshells for reconnaissance and additional payload uploads.
- Unauthenticated AJAX handler accepts PHP uploads via forged file_settings allowlist
- Wordfence blocked 100,000+ exploitation attempts across multiple spikes
- Uploaded shell.php reports host details and enables further malicious file writes
- Patched in plugin version 2.0.3.2; admins urged to upgrade and audit uploads
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2026-27540 | Unrestricted Upload of File with Dangerous Type vulnerability in Rymera Web Co Pty Ltd. Unrestricted Upload of File with Dangerous Type vulnerability in Rymera Web Co Pty Ltd. Woocommerce Wholesale Lead Capture woocommerce-wholesale-lead-capture allows Using Malicious Files.This issue affects Woocommerce Wholesale Lead Capture: from n/a through <= 2.0.3.1. NVD description · AI analysis pending | 9.0 | 2% |
| — |
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| ipv4 | 2.0.3.1 | aw is tracked as CVE-2026-27540 and impacts plugin versions 2.0.3.1 and older. It is an unauthenticated arbitrary file-upload v |
Full article383 words · extracted from bleepingcomputer.com · click to collapse
Hackers are actively exploiting a critical vulnerability in the WooCommerce Wholesale Lead Capture premium plugin for WordPress to upload a PHP backdoor.
The flaw is tracked as CVE-2026-27540 and impacts plugin versions 2.0.3.1 and older. It is an unauthenticated arbitrary file-upload vulnerability discovered by security researcher Teemu Saarentaus.
An attacker can exploit it to upload PHP webshells and execute code, potentially leading to a complete site compromise.
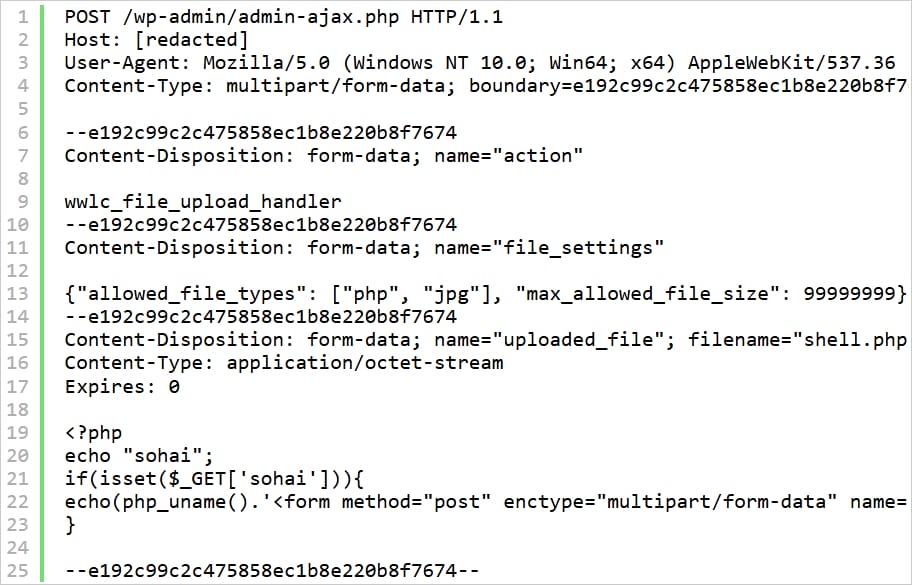
From a technical standpoint, the flaw is caused by exposing an unauthenticated AJAX action named wwlc_file_upload_handler, which checks file extensions against an allowlist supplied through the user-controlled file_settings request parameter.
This allows adding ‘php’ to the permitted file types, making the plugin accept PHP executable file uploads.
The vulnerability was addressed in version 2.0.3.2 of the WooCommerce Wholesale Lead Capture plugin, released on February 20.
However, WordPress security company Defiant is warning that its Wordfence web application firewall blocked over 100,000 attacks linked to CVE-2026-27540.
Wordfence reports that exploitation activity spiked between June 4 and June 17, and on July 1 and August 30.
During the attacks, the hackers upload a webshell that conducts reconnaissance but can also introduce additional payloads.
“The attacker submits a request to the wwlc_file_upload_handler AJAX action containing a forged file_settings parameter and a malicious file with a .php extension,” Wordfence explains.
“The uploaded shell.php is a PHP webshell that reports host details and provides a browser-based upload form for writing additional malicious files to the site.”
Source: Wordfence
Wordfence provides a set of high-offender IP addresses that deployed tens of thousands of exploitation attempts. Administrators are recommended to add them to a blocklist and upgrade to plugin version 2.0.3.2 or later that addresses the security problem.
The researchers advise checking upload directories for unexpected or recently created PHP files, examining logs for requests to /wp-admin/admin-ajax.php invoking wwlc_file_upload_handler, and removing unknown administrator accounts.
If compromise is confirmed, the recommended action is to restore the website from a safe backup, as removing all persistence mechanisms, users, and backdoors may be complicated.
Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.bleepingcomputer.com/news/security/hackers-target-wordpress-sites-via-third-party-woocommerce-plugin/