And farewell from Vegas
Full article499 words · extracted from securelist.com · click to collapse
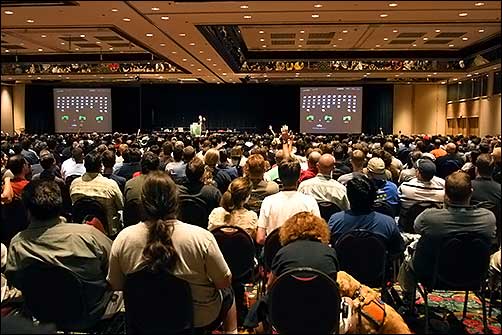

Yesterday Defcon was winding down, the lights were being turned off, and the feeling of electricity among the participants was palpably less than at the beginning of the event. After this grand bash — now as much a part of Las Vegas as any Comdex ever was — people are sobering up, and the reason isn’t just that the alcohol is starting to wear off. It’s also due to a greater realization of just how far-reaching the threat against modern computer systems is.
I attended several sessions on malware and computer-based exploits, and it was clear to me that the bad guys are going to continue to come at our computers with full force. It was equally clear that organized cyber crime exists, with criminal groupings investing the large sums they’ve already made back in to further ‘product development’.
I’m not talking just about developing new exploit code. According to a panel of several U.S. Federal agents, organized cyber crime rings spend heavily on recruiting and retaining people, who may be geographically remote from each other.
Each person within the group will have a specific skill set which complements the skills of other members. Because in many cases cyber crimes transcends geographical borders, the ringleaders have to invest not only in people, but just as heavily in other key areas: computers and peripherals, telecommunications and other fees, and, in some cases, money-laundering and legal fronting organizations.
If this sounds like a expensive business, it is. And yet the bad guys do it because they know think that they’ll see a good return on their investment. And if it sounds like a risky business, well yes, it is. The good guys claim to remain vigilant in curbing cyber crime. As to who will win – that’s a question that only the future can answer.
As the reported 5000+ attendees can attest to, the conference was about much more than just malware and exploits against computers. There were also lighter – though still on-topic – presentations. From upgrading an airline ticket using old ‘skewl’ techniques (which drew raucous applause from a delighted audience) to the ever popular Spot the Fed contest (you G-men need to be more watchful – or perhaps less! – of the young female hacker contingent), this 14th Defcon was both a fun and highly informative event.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/and-farewell-from-vegas/30204/