Greetings from my first visit to Virus Bulletin
Full article451 words · extracted from securelist.com · click to collapse
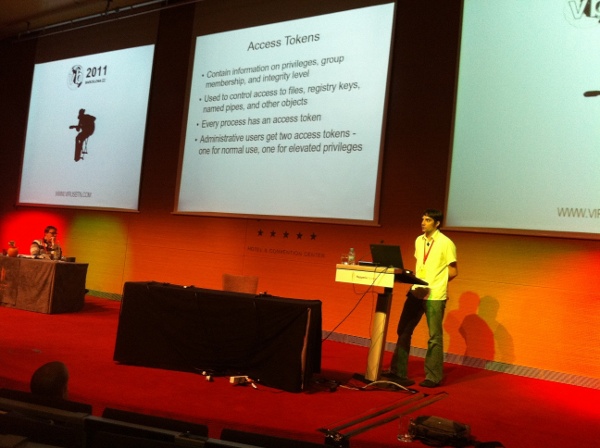

Hello, David Jacoby here checking in from sunny Barcelona where I’m attending the annual Virus Bulletin conference.
I’m sitting here reviewing all the presentations from yesterday, and it just hit me, this is actually my first time at this conference. Previously I have only attended security conferences in the style of Black Hat, Defcon, HITB and others. The content is very different, and also the presentation styles. To be honest, I had no idea what to expect, but so far it’s been really refreshing and educational.
It’s been a blast to meet meet fellow researchers from the same industry and just to get a face to the people behind the e-mail addresses. If you are at Virus Bulletin and reading this, do not hesitate to find me!
So, it’s currently day two, and so far so good. Yesterday I saw about eight presentations, mostly in the technical track, but today I’m mostly visiting the corporate tracks. I think its a good mixture to get information from both tracks. The only problem with two tracks is choosing which one you want to attend.
I’m going through my notes and the presentations I’ve seen so far (in no particular order) are:
- Predicting the future of stealth attacks by Rachit Mathur (McAfee)
- Same botnet, same guys, new code by Pierre-Marc Bureau (ESET)
- A study of malicious attacks on Facebook by a replacement for (Commtouch)
- The dangers of per-user COM objects in Windows by Jon Larimer from (Google)
- Strategies for monitoring FakeAV distribution networks by Onur Komili from (Sophos)
- Malware mining from Igor Muttik from (McAfee)
I cannot really write about all of them, so I decided to pick one that was very interesting, and so far I must say that the one from Jon Larimer about the per-user COM objectives was really interesting. Nice presentation style and pretty interesting content. I mean the vulnerabilities has been disclosed but the concept was interesting. It kind of reminds me of the old LD_PRELOAD vulnerabilities for Unix/Linux. You can read more about the presentation here: http://www.virusbtn.com/conference/vb2011/abstracts/Larimer.xml
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/greetings-from-my-first-visit-to-virus-bulletin-10/30927/