DHS’s cyber wing responds to ransomware attack on pipeline operator
Full article577 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The incident serves as a warning for industrial companies of the ways that ransomware can impact operations.
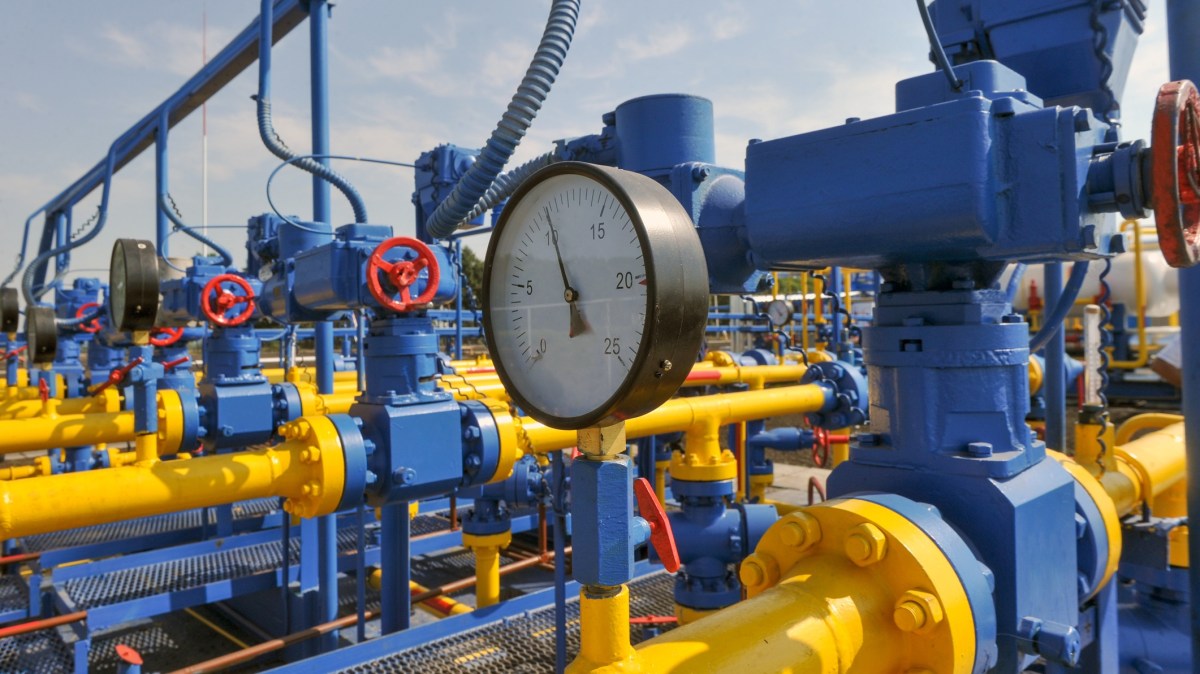
The Department of Homeland Security’s cybersecurity agency recently responded to a ransomware attack on a natural gas compression facility that led the organization to shut down its operations for two days, the agency said Tuesday.
The hackers were able to encrypt data on the organization’s IT and “operational technology” network, a broad term for a network that oversees industrial processes. No longer able to read data coming from across its enterprise, the facility shut down its various assets, including its pipelines, for two days.
The incident serves as a warning for industrial companies of the ways that ransomware can impact operations.
“Although the victim’s emergency response plan did not specifically consider cyberattacks, the decision was made to implement a deliberate and controlled shutdown to operations,” says the advisory from DHS’s Cybersecurity and Infrastructure Security Agency.
The unnamed gas facility is back up and running, but CISA said it was releasing a report to help other organizations protect themselves against similar attacks. U.S. lawmakers have previously called on DHS, and its Transportation and Security Agency specifically, to do more to help protect pipeline operators from cyberthreats. In April 2018, a cyberattack struck accounting software used by a Texas-based owner of more than 71,000 miles of pipelines, disrupting a customer transaction service used by the company.
In the incident flagged Tuesday by CISA, the attackers knocked offline human machine interfaces (HMIs), the dashboards that connect operators to industrial equipment. They did not, however, affect the more sensitive programmable logic controllers (PLC), the ruggedized computers that monitor and control industrial systems.
“At no time did the threat actor obtain the ability to control or manipulate operations,” CISA said. It did not say who was responsible for the attack or if the victim paid the ransom.
Beyond this one incident, CISA is sending a signal to critical infrastructure operators that a failure to plan for ransomware can be costly.
“The victim cited gaps in cybersecurity knowledge and the wide range of possible scenarios as reasons for failing to adequately incorporate cybersecurity into emergency response planning,” the advisory says.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/ransomware-dhs-natural-gas-pipeline/