Senate Democrats call on FTC to investigate Twitter's data security
Full article781 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Lawmakers worry that Elon Musk's hasty changes on the Twitter platform such as altering its verification service could harm consumers.
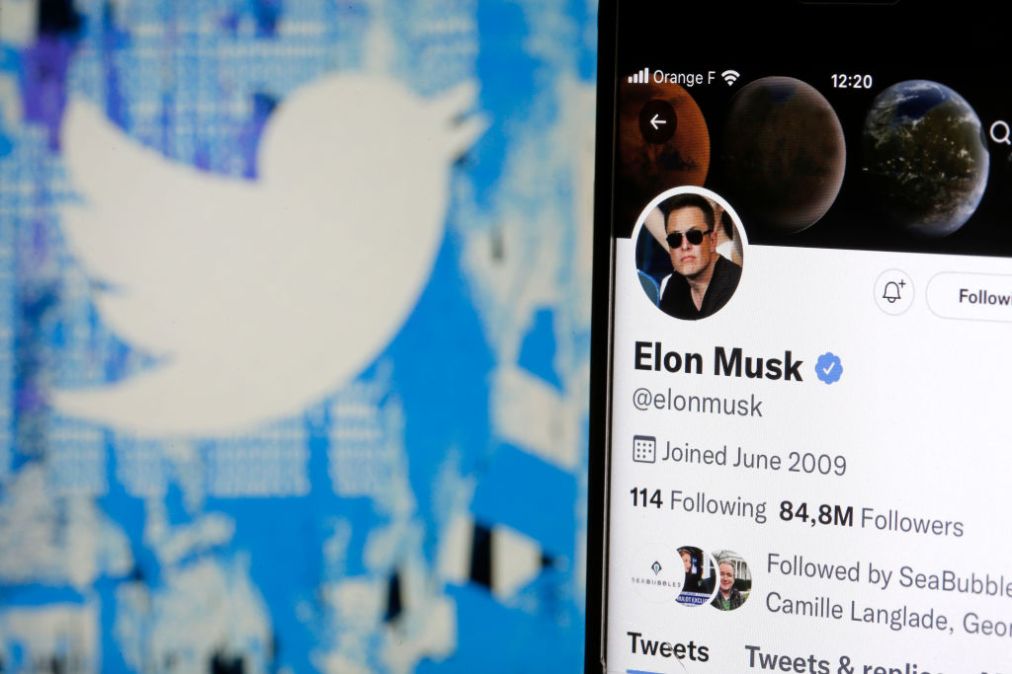
A group of Senate Democrats including Sens. Richard Blumenthal, D-Conn., and Elizabeth Warren, D-Mass., are calling on Federal Trade Commission to investigate potential security issues at Twitter since Elon Musk purchased and took over the company late last month.
In a letter to the FTC sent Thursday, lawmakers expressed concerns that the company may be in violation of consumer protection laws as well as in breach of a 2011 agreement the company reached with the agency over repeated security failures.
Lawmakers’ top concerns related to how Musk rolled out Twitter’s verification services to all paying users, a move that experts warned could further exacerbate the platform’s issues with disinformation and financial scams. Fraudsters immediately used the service, Twitter Blue, to create accounts to impersonate corporations and individuals and spread fake news. Washington Post reporters were even able to create a verified account impersonating Sen. Edward Markey, D-Mass., one of the letter’s signatories.
After Markey wrote a letter to Musk about the issue, Musk responded on Twitter “Perhaps it is because your real account sounds like a parody?”
Perhaps it is because your real account sounds like a parody?
— Elon Musk (@elonmusk) November 13, 2022
“Twitter knew in advance that there was high likelihood the Twitter Blue product could be used for fraud, and still it took no action to prevent consumers from being harmed until this rampant impersonation became a public relations crisis,” wrote the letter’s signatories, which also included Sens. Dianne Feinstein, D-Calif., Ben Ray Luján, D-N.M., Cory Booker, D-NJ, and Robert Menendez, D-NJ.
Lawmakers also expressed concerns that since Musk’s takeover key executives responsible for the privacy, cybersecurity and safety have resigned and many employees tasked with preserving the platform’s security have been cut.
“We are concerned that the actions taken by Mr. Musk and others in Twitter management could already represent a violation of the FTC’s consent decree, which prohibits misrepresentation and requires that Twitter maintain a comprehensive information security program,” the letter states.
Twitter was already under increased lawmaker scrutiny prior to the finalization of Musk’s purchase after its former chief information security officer, Peiter “Mudge” Zatko, filed a whistleblower complaint alleging that the company had misled regulators, consumers and its own board members about its security performance.
Earlier this year, Twitter agreed to pay $150 million to settle a separate case with the FTC and Department of Justice that found Twitter violated its 2011 consent decree by misleading users about how it was using phone numbers collected to verify their accounts.
An internal message from a lawyer at Twitter, obtained by The Verge, suggested that Musk wasn’t deterred by the threat of legal action and that “Elon has shown that his only priority with Twitter users is how to monetize them.”
The FTC has made clear in public statements that Twitter and Musk could be subject to enforcement actions if the agency finds violations of the 2011 order.
“No CEO or company is above the law, and companies must follow our consent decrees,” Douglas Farrar, the FTC’s director of public affairs, said in a written statement last week. “Our revised consent order gives us new tools to ensure compliance, and we are prepared to use them.”
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Election official says Tina Peters would be consultant, won’t have access to election systems
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/senate-democrats-ftc-investigate-twitter/