Threat Advisory: High Severity OpenSSL Vulnerabilities
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2022-3786 +1 in the same advisory: …3602 | A buffer overrun can be triggered in X.509 certificate verification, specifically in name constraint checking. A buffer overrun can be triggered in X.509 certificate verification, specifically in name constraint checking. Note that this occurs after certificate chain signature verification and requires either a CA to have signed a malicious certificate or for an application to continue certificate verification despite failure to construct a path to a trusted issuer. An attacker can craft a malicious email address in a certificate to overflow an arbitrary number of bytes containing the `.' character (decimal 46) on the stack. This buffer overflow could result in a crash (causing a denial of service). In a TLS client, this can be triggered by connecting to a malicious server. In a TLS server, this can be triggered if the server requests client authentication and a malicious client connects. NVD description · AI analysis pending | 7.5 | 92% |
| — |
Full article592 words · extracted from blog.talosintelligence.com · click to collapse
Tuesday, November 1, 2022 15:03
In late October two new buffer overflow vulnerabilities, CVE-2022-3602 and CVE-2022-3786, were announced in OpenSSL versions 3.0.0 to 3.0.6. These vulnerabilities can be exploited by sending an X.509 certificate with a specially crafted email address, potentially causing a buffer overflow resulting in a crash or remote code execution (RCE). X.509 is the standard defining the format of public key certificates, commonly used in protocols including TLS as well as digital signatures. Importantly, these vulnerabilities can affect both the client and server in contrast to most vulnerabilities that typically impact one or the other, broadening the potential attack surface.
These vulnerabilities could be very impactful as OpenSSL is widely used, and the affected version is included in some major Linux distributions. However, the affected version was released relatively recently in September of 2021 so adoption may not be as widespread as older versions, such as 1.1.1 and 1.0.2, which are currently unaffected by this vulnerability.
For more information about these vulnerabilities’ impact on Cisco products, please refer to Cisco’s Security Advisory here.
Cisco Talos is closely monitoring for potential exploitation attempts in the wild as new details of the vulnerabilities are released. We strongly recommend users mitigate affected systems as soon as possible by upgrading to version 3.0.7.
Vulnerability details
A buffer overflow can be triggered by sending an X.509 certificate with a specially crafted email address in the “id-on-SmtpUTF8Mailbox” field ( OID 1.3.6.1.5.5.7.8.9 ) resulting in a crash (Denial of Service - DoS) or potential remote code execution on a vulnerable client or server. Potential opportunities for exploitation can occur if a server requests authentication information after a malicious client connects, or if a client connects to a malicious server, which would then make the client vulnerable.
CVE-2022-3602 is assigned for a 4-byte buffer overflow (single unsigned int overwrite) resulting in a crash or remote code execution. However, CVE-2022-3786 refers to the variable length overflow variant in the X.509 email address field with the potential to result in crashes.
Coverage & Mitigations
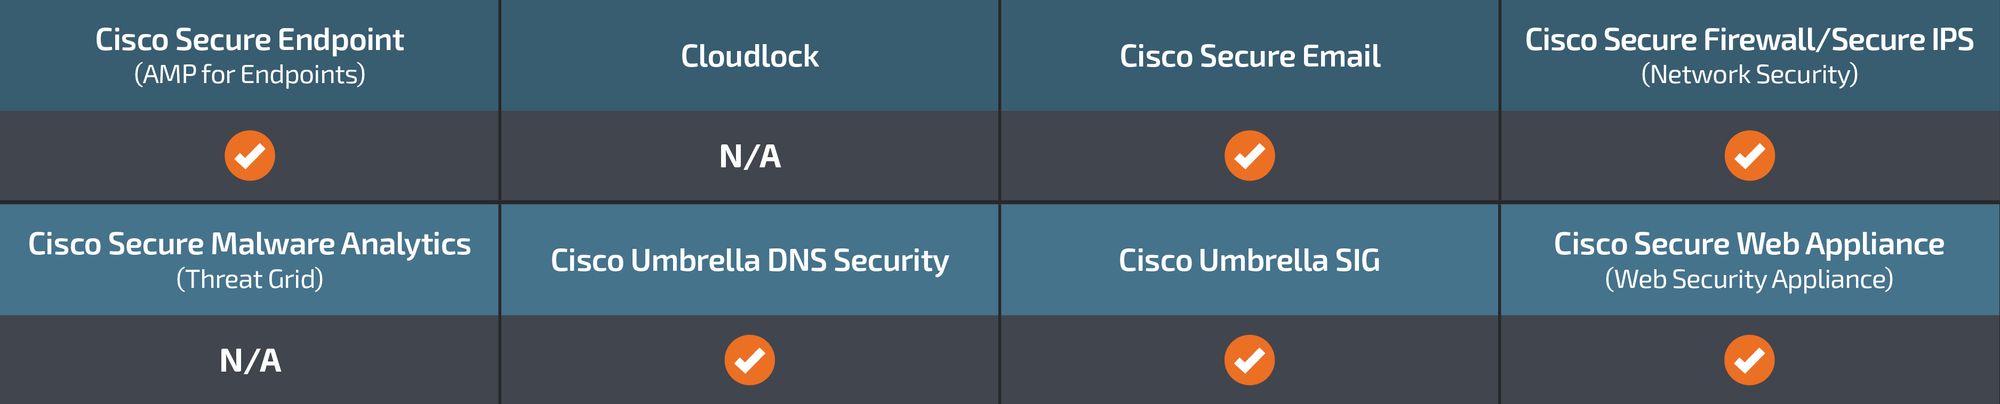
Cisco Secure Endpoint (formerly AMP for Endpoints) is ideally suited to prevent the execution of the malware detailed in this post. Try Secure Endpoint for free here.
Cisco Secure Web Appliance web scanning prevents access to malicious websites and detects malware used in these attacks.
Cisco Secure Email (formerly Cisco Email Security) can block malicious emails sent by threat actors as part of their campaign. You can try Secure Email for free here.
Cisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.
Umbrella, Cisco’s secure internet gateway (SIG), blocks users from connecting to malicious domains, IPs and URLs, whether users are on or off the corporate network. Sign up for a free trial of Umbrella here.
Cisco Secure Web Appliance (formerly Web Security Appliance) automatically blocks potentially dangerous sites and tests suspicious sites before users access them.
Additional protections with context to your specific environment and threat data are available from the Firewall Management Center.
Open-source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org.
For more information about this vulnerability’s impact on Cisco products, please refer to Cisco’s Security Advisory here.
Cisco Talos is releasing Snort Rules: 60790, 300306-300307 to protect against exploitation of CVE-2022-3602.
The following ClamAV signatures have been released to detect malware artifacts related to this threat:
- Multios.Exploit.CVE_2022_3602-9976476-0
Text extracted automatically; images, tables and formatting may be missing. Original: https://blog.talosintelligence.com/openssl-vulnerability/