FTC threatens fines for health apps that fail to report compromised data
Full article568 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The consumer protection agency clarified a 2009 rule meant to help Americans understand when their data is shared improperly.
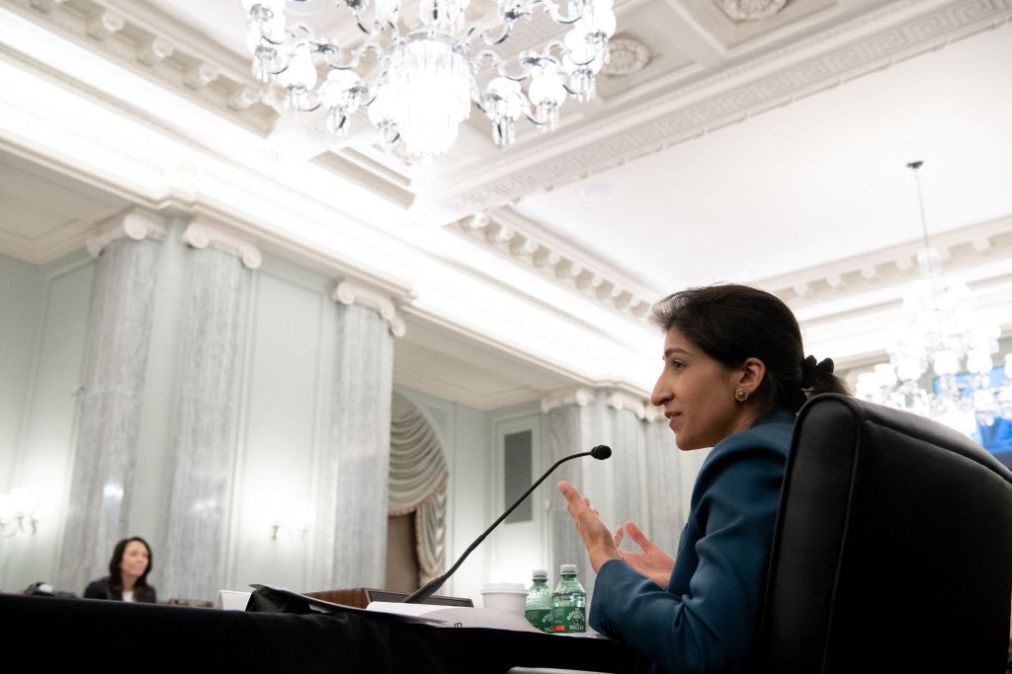
App developers and device operators that collect health data about Americans must alert consumers in the event their personal information is compromised or shared without permission, the Federal Trade Commission ruled Wednesday.
The U.S. consumer protection agency voted 3-2 on a new regulation that is meant to clarify the 2009 Health Notification Rule, which details how companies should tell consumers if their data is improperly shared or breached. The decision Wednesday extends the 2009 rule to cover health apps, fitness trackers and other connected devices that have risen in popularity over the past decade.
“The global pandemic has hastened the adoption of virtual health assistants, with Americans placing their trust in various technologies to track and manage their personal health,” FTC chair Lina Khan said in a statement. “As we have seen, however, digital apps are routinely caught playing fast and loose with user data, leaving users’ health information susceptible to hacks and breaches.”
Unauthorized access to personal data, such as an app developer sharing user information without their consent, as well as data breaches constitute grounds for notification. Failure to comply with the regulation will trigger fines of up to $43,792 per violation, per day.
The update comes after the FTC voted to ban SpyFone, a so-called stalkerware app that enabled snoops to monitor an individual’s phone usage, online activity and physical movements, and prohibited the company’s owner from participating in similar ventures. Along with marketing itself as a surveillance device, the FTC said, SpyFone also failed to enact basic security measures.
“This case is an important reminder that surveillance-based businesses pose a significant threat to our safety and security,” Samuel Levine, acting director of the FTC’s Bureau of Consumer Protection said at the time. “We will be aggressive about seeking surveillance bans when companies and their executives egregiously invade our privacy.”
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/ftc-health-data-fine-lina-khan/