Government website encryption needs help from DHS, Sen. Wyden says
Full article529 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Despite significant improvements to government website encryption, some metadata is still transmitted insecurely, the Oregon Democrat said.
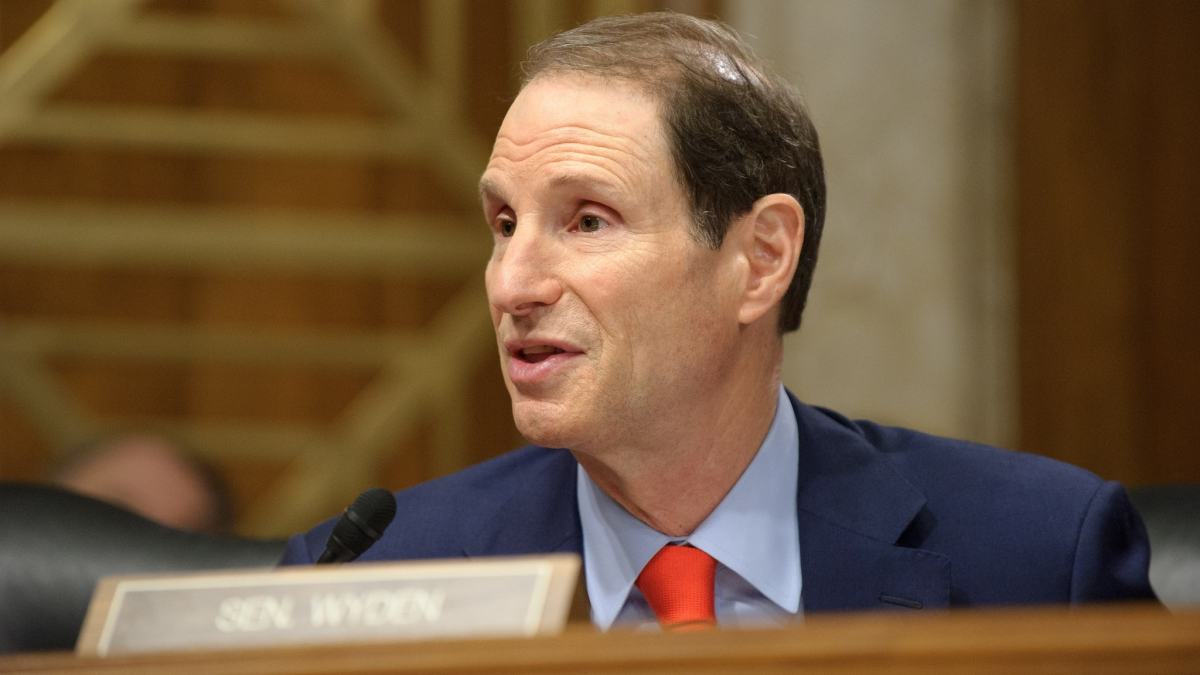
The Department of Homeland Security should push federal agencies to implement stronger encryption practices for government websites visited by federal workers and everyday citizens alike, Sen. Ron Wyden says.
Despite significant improvements to government website encryption, some metadata is still transmitted insecurely, revealing the domain names of sites visited by users, Wyden, D-Ore., wrote to DHS Undersecretary Chris Krebs.
“Hackers can intercept or hijack the unprotected metadata, tricking users into visiting a malicious site or spying on their activities,” the Oct. 24 letter states.
When possible, DHS should require federal agencies to encrypt the online queries employees make to domain name system (DNS) servers, Wyden suggested. He also asked DHS to work with General Services Administration to make using an encrypted protocol extension a condition of selling web content delivery services to the government. The government can usher in broad industry adoption of that encrypted extension, known as ESNI, according to Wyden.
When cybersecurity vendor Cloudflare rolled out ESNI last month, the Electronic Frontier Foundation, a digital privacy advocacy, said the tool “will give a huge boost to the goal of reducing what other people know about what you do online.”
As an example of DHS’s ability to prod agencies toward strong cybersecurity policies, Wyden cited a directive the department issued last year for agencies to encrypt website data. “Requiring agencies to protect metadata with encrypted DNS and ESNI is the next logical step,” he wrote.
The letter also highlights the possibility of agencies addressing encryption issues in-house or contracting a solution out. “Federal agencies should protect DNS data either by operating their own encrypted DNS servers, or using private encrypted DNS services, provided that they meet rigorous cybersecurity and privacy standards,” Wyden wrote.
Wyden asked for an “affirmative response” from Krebs within 60 days.
Gizmodo was first to report on the letter.
Latest Podcasts
Government
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/encryption-federal-government-websites-dhs-ron-wyden/