Apple patches macOS zero-day exploited by malware for months (CVE-2021-30657)
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2021-30657 | Actively Exploited Gatekeeper Bypass in Apple macOS CVE-2021-30657 is a logic flaw (CWE-862) in macOS whose faulty state management allows a malicious application to bypass Gatekeeper, Apple's mechanism that verifies and prompts users before first launch of downloaded software. It is triggered locally when a user opens a malicious, quarantined application; the flawed state handling lets the app launch without the expected Gatekeeper authorization checks. An attacker gains the ability to run unsigned or unnotarized code without the usual security warning, which in observed campaigns enabled adware families such as AdLoad to install on user-level accounts. Any Mac running a version of macOS Big Sur prior to 11.3, or macOS Catalina without Security Update 2021-002, is affected. Apple confirmed the issue was being actively exploited in the wild, and the flaw is listed in CISA's Known Exploited Vulnerabilities catalog. Do: Upgrade to macOS Big Sur 11.3 or later, or apply Security Update 2021-002 Catalina (or newer) per Apple's instructions, then verify the installed version under Apple menu > About This Mac. Because the flaw lets quarantined apps launch without a Gatekeeper prompt, scrutinize downloaded applications and monitor for AdLoad adware indicators on endpoints that have not yet been patched. This CVE is in CISA KEV, so federal and KEV-tracked environments must apply the vendor updates by the required action deadline. | 5.5 | 69% | KEV |
| mass≈100M+ Macs running affected Big Sur or Catalina builds at the time of disclosure |
Full article462 words · extracted from helpnetsecurity.com · click to collapse
Apple has patched a critical macOS zero-day (CVE-2021-30657) that has been exploited by Shlayer malware for months and has finally introduced/enabled the App Tracking Transparency feature and policy in iOS, iPadOS and tvOS.

A zero-day exploited by malware peddlers (CVE-2021-30657)
Discovered by security researcher Cedric Owens and privately reported to Apple in March 2021, CVE-2021-30657 is a logic issue that allowed attackers to craft a macOS payload that is not checked by Gatekeeper, the macOS’s security feature that verifies downloaded applications before allowing them to run, and bypasses File Quarantine and Application Notarization protections as well.
Security researcher Patrick Wardle explored and did a root cause analysis of the vulnerability, then contacted Jamf researchers and asked them if they have ever detected malware exploiting this flaw.
The Jamf Protect detections team observed this exploit being used in the wild by a variant of the Shlayer adware dropper, as early as January 9th, 2021.
“An attacker manually crafts an application bundle by using a script as the main executable. When this bundle is created they do not create an Info.plist file. The application can then be placed in a dmg for distribution. When the dmg is mounted and the application is double clicked, the combination of a script-based application with no Info.plist file executes without any quarantine, signature or notarization verification,” they explained the exploitation process.
Judging by previous tactics employed by the group that pushes Shlayer onto users, the adware was likely posing as an update for a legitimate app (e.g., Adobe Flash Player). Victims who downloaded and ran it would have had no warning from macOS that the application might be malicious.
Apple has fixed CVE-2021-30657 in macOS Big Sur 11.3, along with two other flaws that may allow a malicious application to bypass Gatekeeper checks and a bucketload of other vulnerabilities.
To review the other security updates released by Apple on Monday (April 26) go here.
iOS, iPadOS and tvOS start enforcing App Tracking Transparency
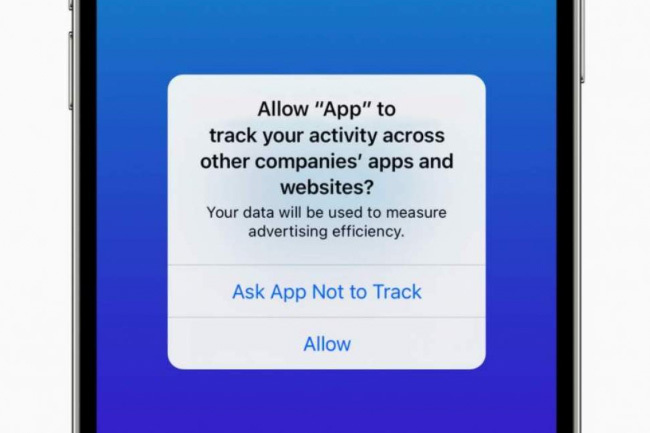
iOS 14.5, iPadOS 14.5 and tvOS 14.5, released on Monday, will start enforcing App Tracking Transparency, a hotly debated feature that will force apps to ask for users’ permission if they want to track their activity across other apps and websites via Apple ID for Advertisers (IDFA) and use their data for things like ad targeting.
Faced with this choice and given the option to say no and still continue using the apps, it is expected that many users will opt out of IDFA tracking, thus impacting some companies’ revenues.
iOS 14.5 and watchOS 7.4 also make it possible for users who own an Apple Watch to unlock their iPhones via Face ID even if they are wearing masks.
For more new iOS features, check out Apple’s iOS 14.5 release notes.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.helpnetsecurity.com/2021/04/27/cve-2021-30657/