After SolarWinds breach, White House preps executive order on software security
Full article634 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
"The level of trust we have in our systems has to be directly proportional to the visibility we have," said Deputy National Security Adviser Anne Neuberger.
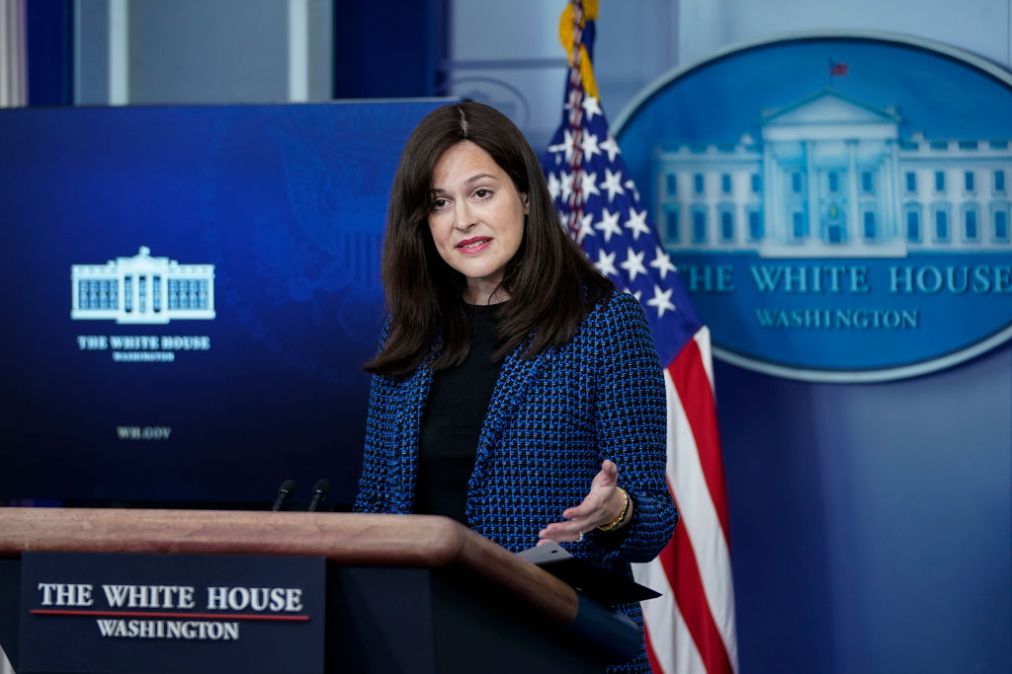
The White House is moving forward with an executive order to encourage software developers to build more security into their products as the investigation of a suspected Russian supply chain compromise continues, a top security official said Friday.
The upcoming directive “will focus on building in standards for software, particularly software that’s used in critical areas,” Anne Neuberger, the deputy national security adviser for cyber and emerging technology, said at the SANS Institute’s ICS Security Summit. “The level of trust we have in our systems has to be directly proportional to the visibility we have. And the level of visibility has to match the consequences of the failure of those systems.”
Neuberger said the directive would be one of the Biden administration’s multiple responses to the alleged Russian spying operation that has exploited software made by federal contractor SolarWinds, among other vendors, and breached nine federal agencies and 100 companies.
Neuberger did not provide details on the timing and scope of the order. A National Security Council spokesperson did not respond to a request for additional information by press time.
The pending action would follow another executive order that President Joe Biden issued Feb. 24 that directs federal agencies to conduct a review of supply chain security risks in industries including information technology.
The alleged Russian hacking activity will take many more months to investigate, Neuberger has said, and it will likely shape the way the U.S. government approaches cybersecurity matters for some time. U.S. officials have said the operation is “likely Russian in origin.” Moscow has denied involvement.
In addition to key software suppliers, the digital intrusions affected “numerous sites across the industrial community,” according to Neuberger. Organizations in the electricity, water and manufacturing sector downloaded the malicious SolarWinds software, she said, raising questions about those critical organizations’ ability to see malicious activity on their networks.
That lack of visibility “was one of the things that was eye-opening for us as we started combing through the lessons from SolarWinds,” she said at the SANS Institute conference.
In that vein, the North American electric grid regulator has asked utilities to report how exposed they are to the tampered SolarWinds software, and has advised utilities that the vulnerability “poses a potential threat” to parts of the power sector.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/white-house-executive-order-software-solarwinds-neuberger/