White House releases National Cybersecurity Strategy implementation plan
Full article1,049 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The plan is a roadmap for the U.S. government to accomplish the goals outlined in the National Cybersecurity Strategy.
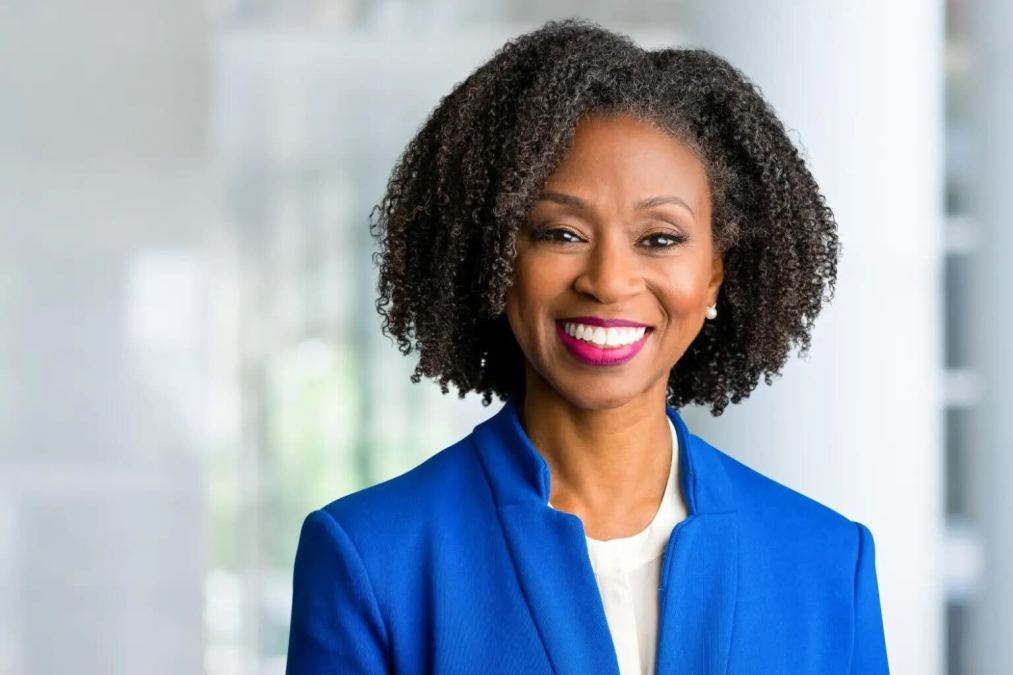
The White House released the first version of its multiyear implementation plan for the National Cybersecurity Strategy on Thursday, setting into motion a significant overhaul of how the federal government will regulate digital security issues.
The implementation plan has been eagerly anticipated by both policymakers and industry as it lays out how the Biden administration plans to make its strategy, which has been largely lauded by experts and officials, into a reality.
The document has more than 65 initiatives to carry out the “five pillars” of the cyber strategy and largely follows the same format. While the strategy is a one-time document, however, implementation plan to carry out that strategy is expected to evolve over time.
“The implementation plan is a living document. The National Cybersecurity strategy is meant to be enduring and is crafted to guide policy across the decisive decade in which we find ourselves,” said Acting National Cyber Director Kemba Walden at a press briefing on Wednesday. “Implementation Plan, on the other hand, will evolve whether in response to changing threat landscapes, or as initiatives are completed and we get follow on actions.”
The plan released Thursday will be updated next year to 2.0 and other aspects of the plan will be updated as they are completed or new cyberthreats require some alterations.
Walden noted there are several aspects of the plan that are either already completed or are underway such as working to codify the Cyber Safety Review Board, the Pentagon’s updated unclassified cyber implementation plan, and the nearing completion of the anticipated national cyber workforce and education strategy.
“While it does not intend to capture all cybersecurity activities being carried out by agencies, it describes more than 65 high-impact initiatives requiring executive visibility and interagency coordination that the Federal government will carry out to achieve the Strategy’s objectives,” the document states.
Some initiatives of the plan include the Cybersecurity and Infrastructure Security Agency updating the National Cyber Incident Response Plan, which the agency announced in January and is expected to be completed in the first quarter of fiscal year 2025.
“The update will also include clear guidance to external partners on the roles and capabilities of federal agencies in incident response and recovery,” Walden said.
Another initiative around cyber mandates for critical infrastructure will have the National Security Council, sector risk management agencies and regulators, and the ONCD analyze cyber risk in sectors and outline how to either use existing authorities to mandate better defenses or develop proposals to close any gaps in authorities.
Some of the plan’s initiatives are expected to be accomplished this year. For instance, the Office of Management and Budget will work with the Federal Acquisition Regulatory Council to propose Federal Acquisition Regulations changes for Internet of Things devices, the IoT labeling program, CISA’s work on building domestic and international support for a coordinated vulnerability disclosure, and a State Department effort to develop an international engagement plan to counter ransomware crime.
The plan comes just as the federal government is in the midst of another widespread hacking incident impacting federal agencies. The Chinese-linked operation gained access to the emails of roughly two dozen organization worldwide including multiple U.S. federal entities.
Asked how the plan will help in ongoing situations like the Chinese campaign, Walden said that “the strategy has two pivotal pieces to it: one is to make sure that we are more defensible and that we are more resilient.”
“So what does that mean? That we know cyberattacks are going to happen but that the downtime is going to be quick, and that the impact won’t be catastrophic,” Walden said. “So we need to figure out what investments we need to make.”
More Scoops
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
The six-month program will be overseen by the Office of the National Cyber Director and Texas Cyber Command to “find out what works.”
Irregular says ‘human oversight’ responsible for AI sandbox escape incidents
National cyber director lays out White House plans to secure AI without writing new rules
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Election official says Tina Peters would be consultant, won’t have access to election systems
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/national-cybersecurity-strategy-implementation-plan-2/