Industry group sounds alarm over 'Tardigrade' malware targeting biomanufacturing sector
Full article549 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The malware shows a "significant level of autonomous decision-making ability."
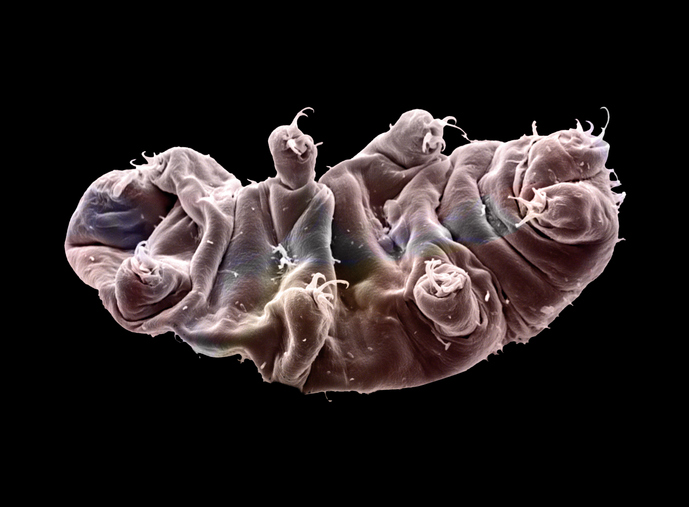
A group of likely foreign government-sponsored hackers is behind cyberattacks on two bio-manufacturing companies that occurred this year, using a kind of malware capable of operating with independence within a network, an industry group warned.
The Bioeconomy Information Sharing and Analysis Center (BIO-(ISAC) dubbed the malware “Tardigrade” after the resilient micro-animal, and said it looks like the work of an advanced persistent threat group, a term that most often refers to government-backed attackers.
Researchers first investigated the hacking tool this spring following a ransomware attack. The actor behind Tardigrade doesn’t just appear to want payment to decrypt systems, though. Rather, it could be primarily a tool for intellectual property theft, BIO-ISAC said on Monday.
The biomanufacturing sector encompasses makers of coronavirus vaccines and treatments, although BIO-ISAC has declined to say whether the firms hit in the spring and then in October were involved in battling COVID-19. “Bioeconomy” is a term with little consensus on its definition, according to the National Academies of Science, Engineering and Medicine, but most definitions include the use of biological resources to sustainably provide goods.
BIO-ISAC didn’t attribute the attacks to a specific nation, but noted some similarities with Russian hacking techniques. The U.S. government has accused China, Iran, North Korea and Russia of trying to steal U.S. coronavirus research.
Tardigrade is an offshoot of SmokeLoader, a malware that’s been sold on cybercriminal markets as far back as 2011, BIO-ISAC says. However, Tardigrade “is far more autonomous,” demonstrating a “significant level of autonomous decision-making ability” and more “able to decide on lateral movement based on internal logic.”
BIO-ISAC, which has pressed the Department of Homeland Security to deem biomanufacturing a critical infrastructure sector, advised companies to segment their networks, test offline backups of key systems and ask, “If this machine was inoperable overnight, what would be the impact?”
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/tardigrade-bio-isac-coronavirus-biomanufacturing-bioeconomy/