Biden administration nears completion of second cybersecurity executive order with plethora of agenda items
Full article1,271 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Federal agencies would have to address everything from AI to cloud security to access management, sources told CyberScoop.
Listen to this article
0:00
Learn more.
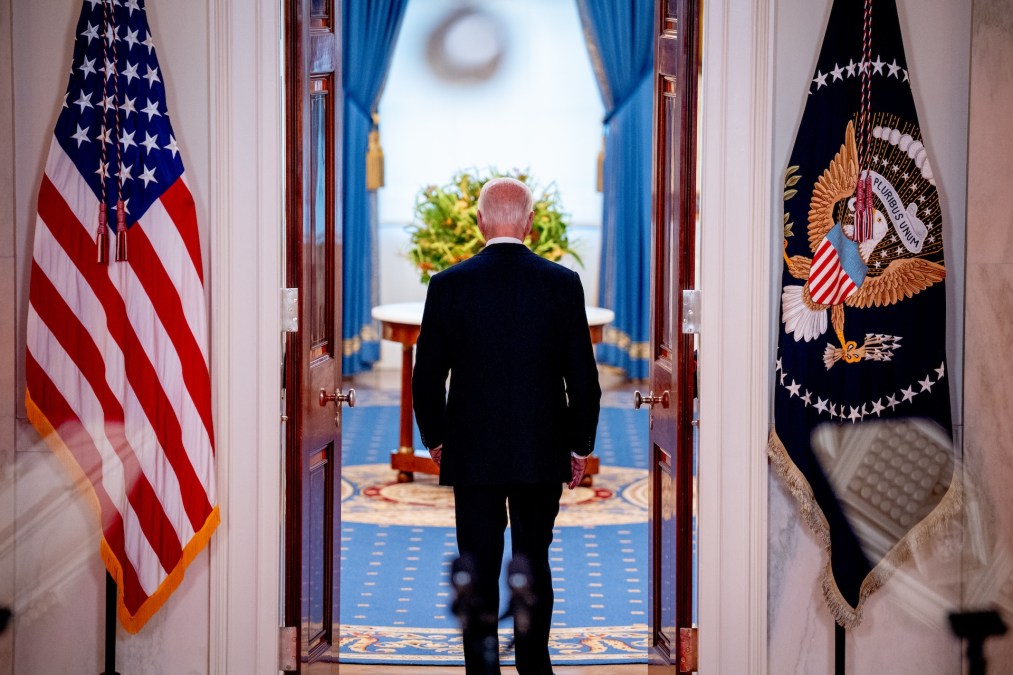
The White House is close to finalizing a second executive order on cybersecurity that covers a wide range of subjects for federal agencies to address, including artificial intelligence, secure software, cloud security, identity credentialing and post-quantum cryptography, according to sources familiar with work on the document.
The executive order, a follow-up to the sweeping cybersecurity executive order President Joe Biden signed in his first year in office, had been working its way through the interagency process, during which agencies give feedback on the draft, sources said.
According to one source familiar with the order, the interagency process has wrapped up and a draft is “95%” of the way toward its final incarnation. The target is to get something signed in early December, subject to the president’s review and approval. But another source recently told CyberScoop that the executive order is viewed as “pretty aspirational to get it done.” Biden will leave office in January, although the Trump administration finished up a cybersecurity-related executive order deep into January of the former president’s term.
Few details of the executive order have been made public. Anne Neuberger, the deputy national security adviser for cyber and emerging technology at the White House, has spoken sparingly about it at a pair of cybersecurity conferences in recent months.
“As we work on the Biden administration’s potentially second executive order on cybersecurity, we’re looking to incorporate some particular work in AI, so that we’re leaders in the federal government in breaking through” in areas like writing more secure code, finding vulnerabilities, generating patches and gleaning information from forensics and logs, she said at the Billington Cybersecurity Summit in September.
The White House declined to comment.
AI is in fact a focus of the draft, according to multiple sources. It contains pilot programs “for accelerating next-gen cyber defense AI models,” one source said. Biden signed an AI-centric executive order last year that had some cybersecurity elements.
Another section deals with transparency and deployment of secure software that meets standards set forth in the first Biden executive order. That order sought to leverage the immense purchasing power of the federal government, requiring contractors to comply with certain security rules before they can do business with agencies in hopes of promoting those standards throughout the private sector.
Under the first order, companies are required to attest that they adhere to secure software development practices, in language spurred by Russian hackers who infected an update of the widely used SolarWinds Orion software to penetrate the networks of federal agencies. The second order would address publicizing when companies have submitted their attestations “so that others can know, here’s the software that meets the secure standards” and allow for the “broader benefit to other users of the same software,” a source said.
Chinese hackers exploiting a gap in Microsoft’s cloud environment last year to access the emails of federal agency employees is one inspiration for components of the draft order about software supply chain security. The section would update cloud standards under the FedRAMP program for assessing the security of cloud products that the federal government uses, the source said.
The post-quantum cryptography section will build on the release of National Institute of Standards and Technology standards earlier this year, the source said.
The source said there’s also a section on modernizing federal identity credentialing and access management, which involves the security of how federal personnel sign into agency systems and controlling who can access which systems or data.
Other sections touch on software bills of materials, open-source cybersecurity as well as securing federal communication and internet routing, aligning policy practices and modernizing guidance for agencies on national security systems, the source said.
Cyber experts have differing views on what any follow-up to the first cyber executive order should include.
“It’s important for a subsequent executive order to really take inventory of what was in the first one to see which items should carry forward, because very few of those action steps are ever 100% obtained,” said Brandon Pugh, director of the R Street Institute’s cybersecurity and emerging threats team. “Regardless of how this election turns out, we’re going to have a new administration, and that’s one risk of putting something out.”
That doesn’t necessarily mean that the politics of cyber will change, so much as the likelihood that “a new president will have some degree of vision when it comes to cybersecurity regardless of who is elected,” Pugh said, meaning anything that’s prescriptive or has a lot of mandates might conflict with the incoming president’s vision.
Another cybersecurity expert, speaking on condition of anonymity, questioned how valuable a second executive order could be if it gives more tasks to agencies without any guarantees of funding to implement them all.
There is still room for a second executive order, said OpenPolicy CEO Amit Elazari — particularly on AI. “The original cyber executive order was very ambitious, and the AI executive order did include a lot of cyber components as well,” she said. “So just looking holistically, cybersecurity and AI is a really good follow-up.”
The threat picture also has changed dramatically since 2021, Elazari added.
AI is an area where a second executive order could make a big difference, said Lindsay Gorman, managing director of the German Marshall Fund’s technology program.
“In the cyber case, there are incredible opportunities for AI, both in cyber offense and defense,” she said. “We haven’t seen a broad-scale adoption of those technologies in the cybersecurity of government agencies.”
More Scoops
100-plus companies call for ‘global surge’ in AI-powered cyber defense
OpenAI, Anthropic, Google, Microsoft, and others say there’s a narrow “defenders’ window” to strengthen security before AI-powered attacks become more sophisticated.
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Federal judge issues second order blocking Trump mail-in voting directive
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Election official says Tina Peters would be consultant, won’t have access to election systems
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/biden-cybersecurity-executive-order-ai-cloud-security-identity-credential/