Lawmakers demand answers in wake of strange OPM identity fraud lawsuit
Full article829 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Virginia lawmakers are especially interested in learning how the defendants acquired the data.
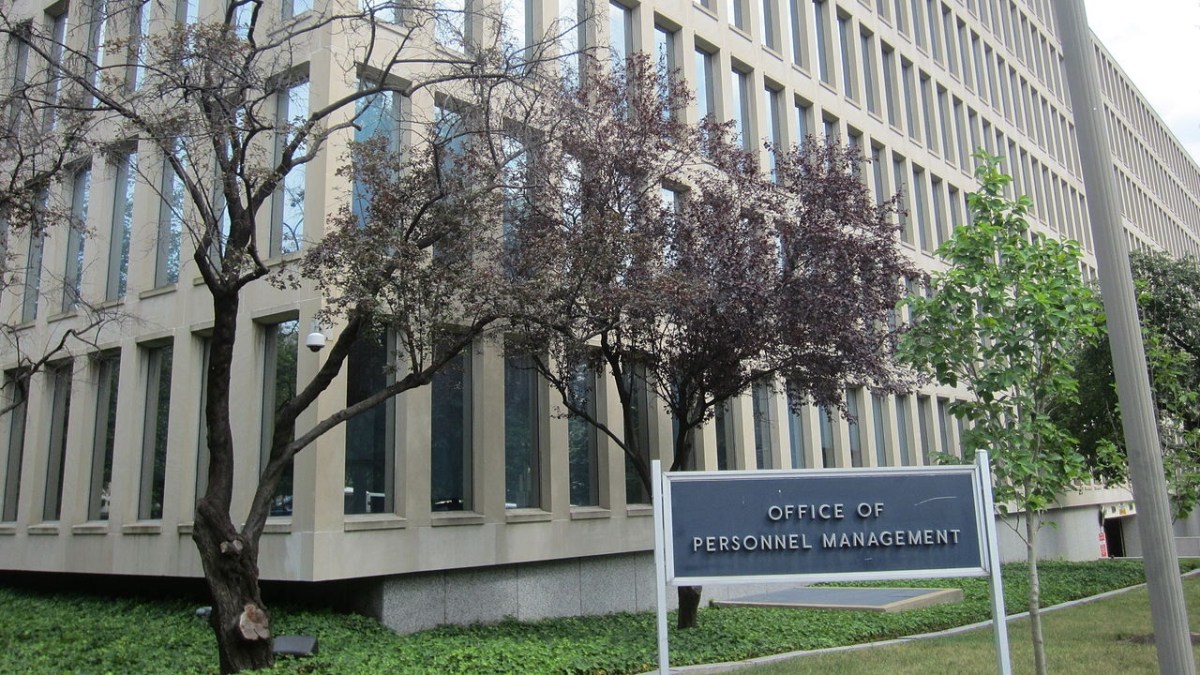
With mystery swirling around an identity theft case where prosecutors have claimed the perpetrators used personal information included in the Office of Personnel Management breach, two lawmakers are pushing the government for more information.
A pair of letters sent this week by Sen. Mark Warner, D-Va., and Rep. Gerry Connolly, D-Va., to the heads of the Department of Justice and OPM issues a number of questions about the alleged identity fraud charges. The Virginia lawmakers are especially interested in learning how the defendants acquired the data.
On June 18, the Eastern District of Virginia announced that a Maryland woman had pleaded guilty to identity theft charges. That press release initially said the data used in that crime was from the OPM breach. On June 21, the district issued a correction to their press release, stripping any mention of the breach.
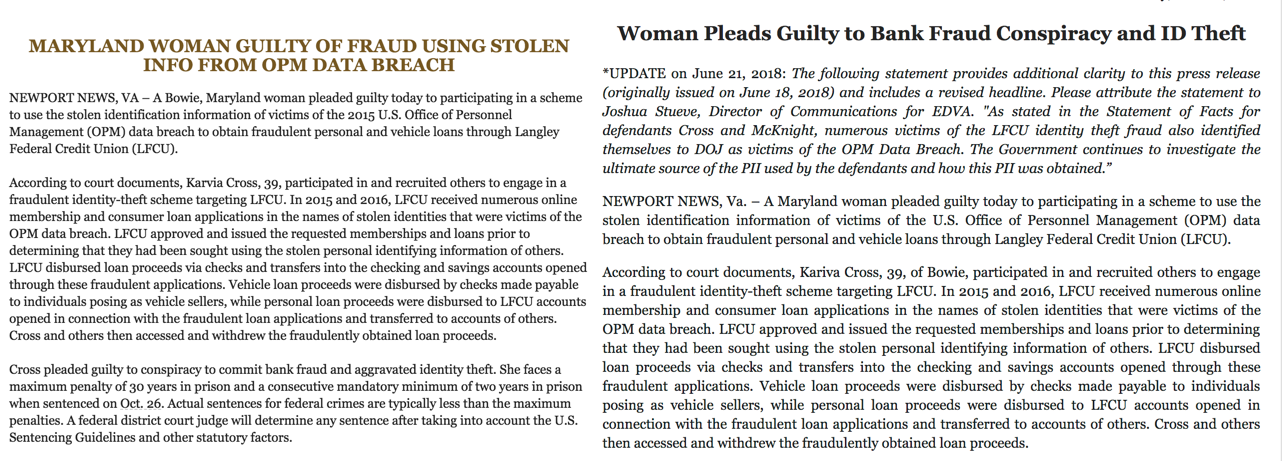
A comparison of the press releases issued by the U.S. Eastern District of Virginia. On the left, the press release from June 18. On the right, the amended version from June 21.
Virginia is home to the single largest population of federal workers and government contractors. Data stolen from OPM carried highly sensitive personal identifiable information, including social security numbers and medical records. Fears that the stolen data could be used by criminals has been looming for years.
The widely assumed notion is that OPM breach was carried out by a Chinese government-linked hacking group that was looking for counterintelligence material. While never publicly attributed to any group, the breach was not believed to be carried out by financially motivated actors.
The latest revelation challenges that narrative and simultaneously helps various civil lawsuits still pending against the government for the breach.
It remains possible that the defendant in this case used stolen data that also existed in OPM’s database, but was taken entirely different source, such as a breached financial institution.
Since the DOJ announcement, current and former government officials affected by the breach have questioned if they, too, are now at risk of having their identities stolen.
Multiple attempts to contact the defendant’s lawyer went unanswered.
Connolly told CyberScoop Wednesday that if the alleged fraudsters really did use data stolen by hackers during the 2015 OPM breach, it would be “hard to believe” that there weren’t more victims of fraud using that data.
But regardless of what emerges in the fraud case, Connolly said that there was a continued and urgent need to protect the OPM breach victims.
“I am very alarmed,” he said. “What additional measures are we taking to protect against that [fraud]?”
You can read the letters from Connolly and Warner below.
Sean Lyngaas contributed to this report.
[documentcloud url=”http://www.documentcloud.org/documents/4560208-Letter-to-DOJ-and-OPM.html” responsive=true]
[documentcloud url=”http://www.documentcloud.org/documents/4562291-2018-06-26-Gec-Letter-to-Doj-Opm-Data-Breach-Case.html” responsive=true]
More Scoops

Lawmakers spring to save ID theft services for OPM breach victims, with expiration looming
Sen. Mark Warner, D-Va., and Del. Eleanor Holmes Norton, D-D.C., hope to make the services permanent before they end next month.
Dem report concludes Department of Government Efficiency violates cybersecurity, privacy rules
Lawmakers fear Elon Musk, DOGE not adhering to privacy rules
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/opm-identity-fraud-mark-warner-gerry-connolly/