The human vulnerability
Full article393 words · extracted from securelist.com · click to collapse



Hello from the Middle East! I’m in Kuwait City where I’m speaking at the Kuwait ICT Security Forum. The topic of my presentation? Web 2.0 attacks, of course –that’s where it’s at these days.
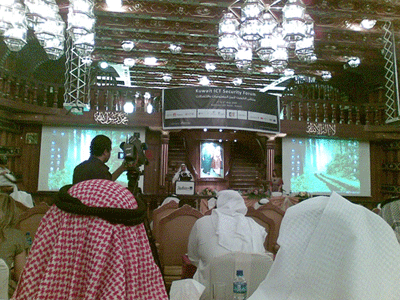
One of the biggest points when I talk about web 2.0 threats is the importance of social engineering, or the “human vulnerability”, as I like to call it, in getting innocent users’ computers infected. Social engineering has been around for just about ever, way before any social networking sites, but right now, with everyone and their dog using sites like Facebook, Twitter, etc., it seems to me the two go hand in hand. Social engineering, social networking – not so hard to spot what these two have in common, is it?
We’ve recently seen a massive increase in phishing attacks on the Facebook login page. Attackers have been using Facebook’s internal message system to send short messages that direct users to “fbaction.net”, a website purposely designed to clone Facebook’s log-in screen.
Why do the bad guys want Facebook passwords? Simple: malicious code distributed via social networking sites is 10 times more effective in terms of successful infection than malware spread via email. Users are far more likely to click on a link received from a trusted friend (or a trusted friend’s dog!) rather than a link in a random spam message.
Don’t be a victim: consider creating a bookmark for the login page, or typing www.facebook.com directly into the browser address bar. Even better, think about using HTTPS, especially if you are browsing from a public network: https://www.facebook.com.
This advice doesn’t only apply to Facebook, of course. Here’s to happy socializing! Or should I say… safe socializing?
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/the-human-vulnerability/30510/