Class action lawsuit filed against two Puerto Rican hospitals for alleged ransomware attacks
Full article892 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The suit claims the hospitals had a 'wanton disregard' for security.
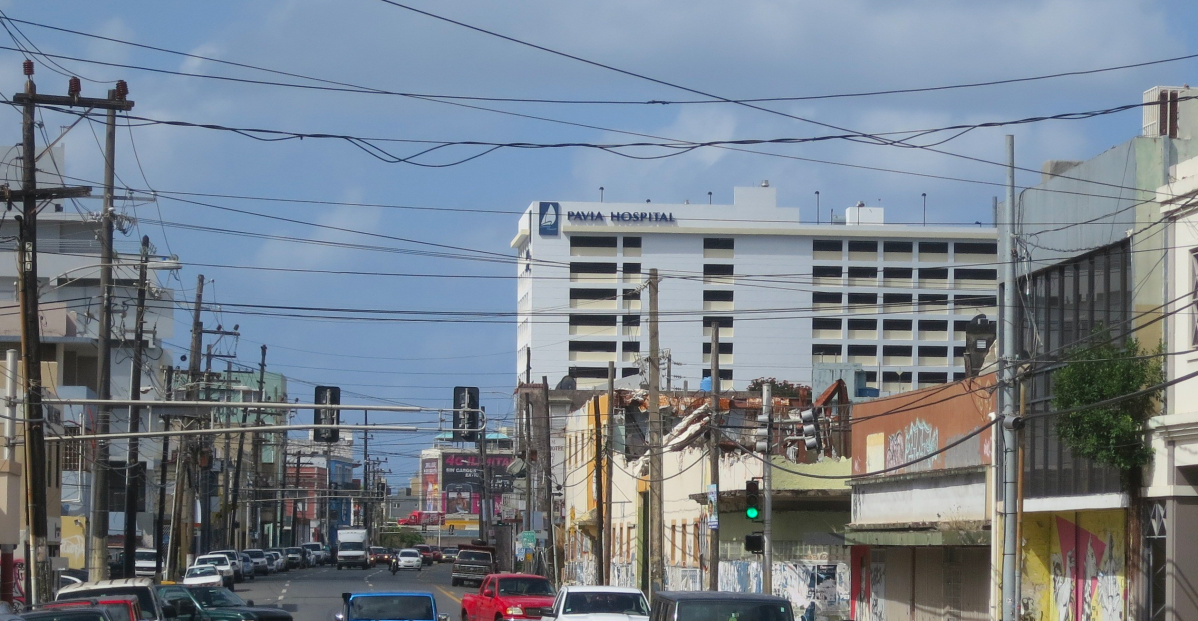
A class action lawsuit was filed earlier this week in the U.S. District Court for the District of Puerto Rico against two hospitals for what plaintiffs are calling “reckless and negligent violation of patient privacy rights” in light of alleged ransomware attacks that hit the hospitals last year.
The alleged ransomware attacks, which took place in February last year at the Pavía Hospital Santurce and Pavía Hospital Hato Rey hospitals, affected 305,737 people, according to Department of Health and Human Services records. The plaintiffs, both former patients of the hospitals, allege patients’ personal identifying information, including full names, addresses, dates of birth, gender, financial information, and social security numbers, were exposed as a result of the attacks. These records also constitute protected health information as designated by HIPAA.
“These patients reasonably expect the highest level of protection for their private identifiable information, when giving highly sensitive information such as their Social Security numbers and medical information to medical providers and insurers,” the complaint says. “What these patients do not expect, and did not expect, was that their personal and sensitive information would be harvested by unauthorized individuals.”
Although the plaintiffs allege that their “patient information was stolen,” it was not immediately clear if the patients’ information had been stolen, or whether the ransomware attacks had just encrypted computers and demanded ransom to decrypt them.
Hospital Pavía told a local news outlet last year that it found no patient information was impacted by the attack.
Increasingly, ransomware attacks are being used in concert with attempts to steal data, and not just as a way to steal money, according to Recorded Future.
“If a ransomware attacker is sitting in your network for weeks before encrypting the first machine, that gives them ample time to exfiltrate gigabytes’ worth of data, as we have repeatedly seen,” Allan Liska, a senior threat intelligence analyst at Recorded Future, said in a ransomware analysis report released today.
‘Compensable damages’
As a result of the alleged ransomware attacks, the plaintiffs argue they have suffered “compensable damages” because they have been forced to purchase identity monitoring services to guard against identity theft, or hackers dumping and selling their information online. The victims are at “imminent, immediate and continuing risk of further identity theft-related harm,” the complaint says.
They are seeking an amount they suggest be determined at trial; costs of the lawsuit, litigation and attorneys’ fees; and injunctive relief so that the hospitals maintain “reasonable security procedures” to protect PII from unauthorized access or disclosure.
‘Wanton disregard for security’
The hospitals failed to properly protect victims’ PII, the complaint claims.
“The exposure of Plaintiffs’ and Class Members’ PII to unauthorized third-party hackers was a direct and proximate result of Defendants’ failure to properly safeguard and protect Plaintiffs’ and Class Members’ PII from unauthorized access, use, and disclosure, as required by their contracts with Plaintiffs and the Class Members, and federal law,” the complaint alleges. “Defendants acted with wanton disregard for the security of Plaintiffs’ and the Class Members’ PII.”
The plaintiffs also take issue with how quickly the hospitals notified victims of the ransomware attack, according to the complaint. The hospitals reported the incident on April 13, 2019, according to HHS records. But the plaintiffs allege they were only notified in June.
According to HHS and HIPAA, individuals must be notified in case of a breach “without unreasonable delay and in no case later than 60 days following the discovery of a breach.”
Defendants Metro Santurce, Inc., which owns Pavía Hospital Santurce, and Metro Hato Rey, Inc., which owns Pavía Hospital Hato Rey, did not return requests for comment.
The incidents occurred prior to two other medical facilities in Puerto Rico — Bayamón Medical Center and Puerto Rico Women and Children’s Hospital — being hit with ransomware. Those attacks, which occurred in May 2019, impacted more than half a million patients.
You can read the lawsuit below or here.
[documentcloud url=”http://www.documentcloud.org/documents/6775566-Class-Action-Lawsuit-Puerto-Rico.html” responsive=true height=450]
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/hospital-pavia-class-action-lawsuit-ransomware/