Brazilian Trojans beyond borders
Full article313 words · extracted from securelist.com · click to collapse


Brazilian cybercriminals have always been very active in the creation and dissemination of banking Trojans among their compatriots. But now they are redirecting their attacks beyond the borders of Brazil to target banks in Europe. In recent months we have seen several Trojans developed in Brazil attempting to attack financial institutions in Europe, especially in Spain and Portugal.
As a rule, European banks were attacked by sophisticated Trojan bankers like SpyEye and by Zeus gangs, but now they face an onslaught from Brazilian Trojans. Our statistics show the dissemination of a specific variant affecting customers in Brazil and Portugal:
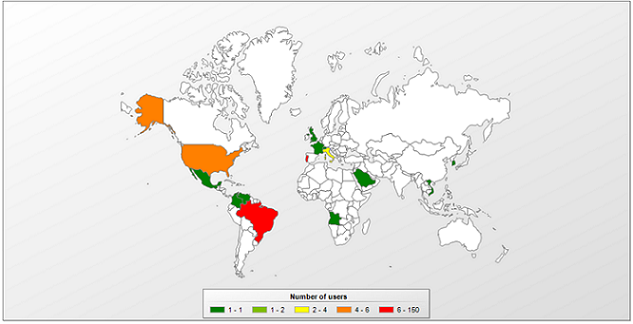
Trojan-Banker.Win32.Banbra.akzy
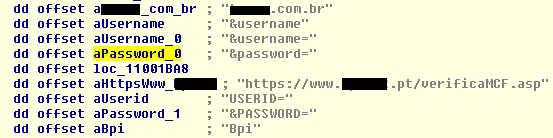
Inside the code of this Trojan we can see the name of some of the Brazilian and Portuguese banks targeted in the attack:
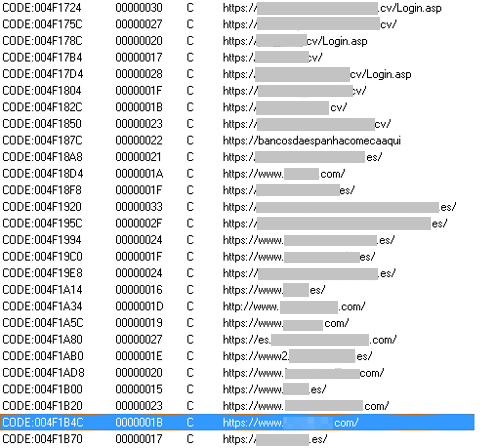
In other similar Trojans we found a function capable of stealing credentials from Brazilian customers:
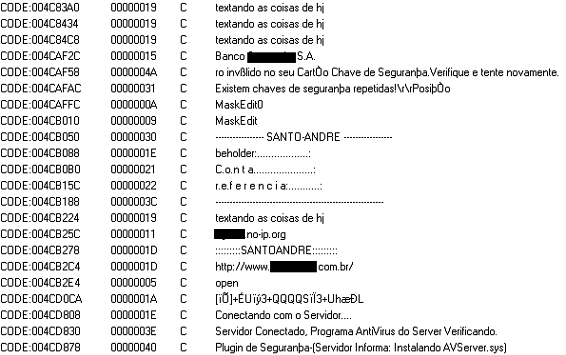
As well as customers of banks in Cape Verde and Spain:
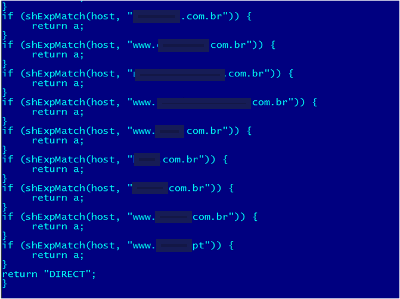
In a malicious proxy script commonly used in MitB attacks detected by our heuristic engine, we can see a list of Brazilian banks redirected to a malicious host – and surprisingly, a bank from Portugal is also targeted in the attack:
All these Brazilian Trojans demonstrate that cybercrime has no borders!
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/brazilian-trojans-beyond-borders/30879/