McAfee pushes government to craft improved cybersecurity game plans
Full article923 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
In the face of malware's growth in both category and character, government experts joined private sector leaders Thursday to formulate better ways to tackle cybersecurity challenges.
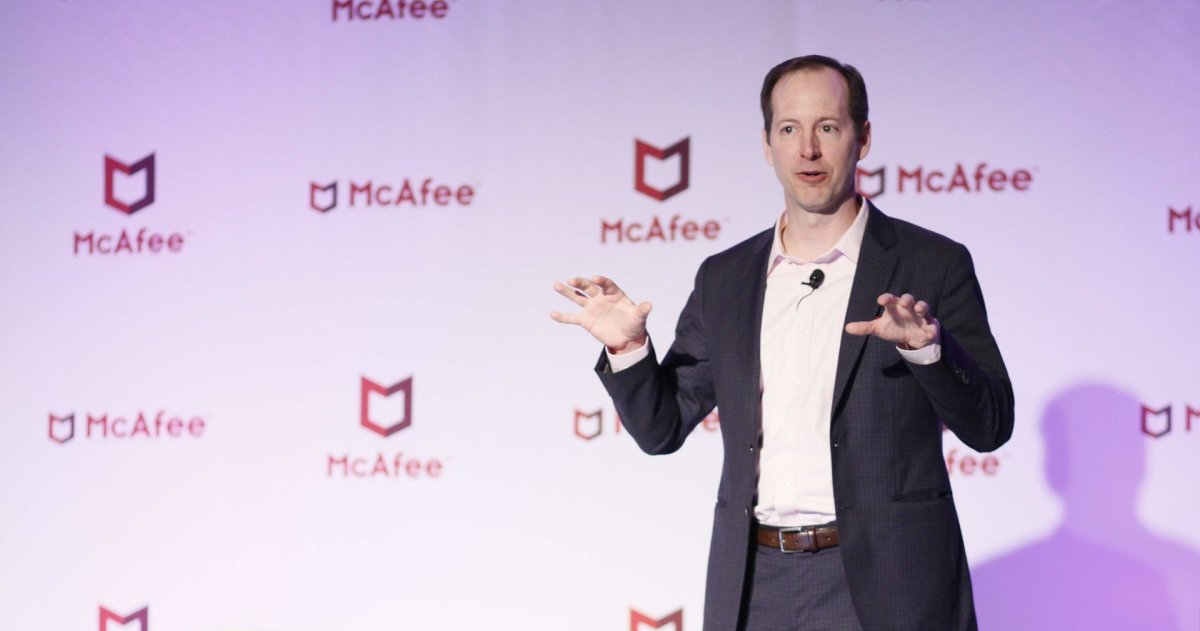
In the face of malware’s growth in both category and character, government experts joined private sector leaders Thursday to formulate better ways to tackle cybersecurity challenges.
During McAfee’s 2017 Security Through Innovation Summit, both sides of the public and private sector relationship talked about changes needed at every aspect of the security ecosystem, from better information sharing to more automation to a total revamp of the government acquisition process.
“We as an industry have been tackling this cybersecurity problem in the fundamentally wrong way,” said Brian Dye, McAfee’s executive vice president of products, at the event hosted by CyberScoop and FedScoop.
Automation was a continuing theme Thursday, promoted not only as a way to address cybersecurity workforce shortages but also improve the consistency and reliability of network defenses.
A panel of government speakers drew a distinction between tasks that could be made “automatic” — where no input was required — and those that might require some input or judgment that could be automated with software.
“Have your humans work on human tasks and your computers work on computer tasks,” said Andy Brody, who is a member of the U.S. Digital Service stationed at the Department of Homeland Security.
McAfee believes a reliance on automation, as well as enhanced information sharing, could help stem the growing tide of attacks. According to a threat report the company released Thursday, the volume of bad data, the lack of timeliness, and overall poor quality of threat intelligence is bad for both the public and private sector.
“Working together is power,” said Vincent Weafer, Vice President of McAfee Labs. “Addressing these challenges will determine the effectiveness of cybersecurity teams to automate detection and orchestrate responses, and ultimately tip the cybersecurity balance in favor of defenders.”
Government executives highlighted their own evolving practices when it comes to threat sharing over the course of the program.
Department of Commerce CISO Rod Turk said the cross-cutting functionality required by the deployment of DHS’ Continuous Diagnostics and Monitoring tools helped get many other conversations started about ways the various parts of the department could bring their IT provisioning together.
It was a “significant culture shift,” he said. “From a shared services point of view it’s kind of broken the ice to get us thinking about other things we could do collaboratively.”
Yet while sharing information within agencies is improving, there is a bigger challenge to share worthwhile information in the face of cybercrime investigations.
The Homeland Security Department and FBI follow distinctly different missions, and this extends into cyberspace, according to John Felker, director of the National Cybersecurity and Communications Integration Center.
“There’s always going to be some tension between our mission space at DHS, which is asset response, threat mitigation — stop the bleeding, if you will — and law enforcement’s threat response, which is to catch a bad guy and make a successful prosecution,” Felker said during McAfee’s Security through Innovation conference hosted by CyberScoop and FedScoop. “It’s not easy and it’s case-by-case. The challenge we have is to keep a relationship that is open and honest and transparent between us.”
Ongoing negotiations effectively determine when DHS will rapidly reach out to a victim of cybercrime or if the FBI will be afforded a grace period to collect evidence and gain new insight. This collaborative although sometimes challenging balance between DHS and FBI underscores a larger cyberthreat information sharing paradigm between the two agencies and broader federal government.
“The speed of trust is there,” said FBI Section Chief Trent Teyema. “By design we have that friction because we’re trying to get information to go after a case and they’re trying to ‘stop the bleeding.’ We want that friction, we want that dialogue going forward. It’s a good process.”
The process is something that McAfee execs pressed the audience to think about as they continue to keep up with the ever changing threat landscape.
“It’s important that we don’t over-simplify the field of cybersecurity,” said McAfee CTO Steve Grobman.
Chris Bing and Shaun Waterman contributed to this story.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/mcafee-security-through-innovation-2017/