Here's how to (legally) hack the Defense Department
Full article562 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The Department of Defense released a policy Monday that allows freelance security researchers a legal way to disclose vulnerabilities in any of the department’s public-facing systems.
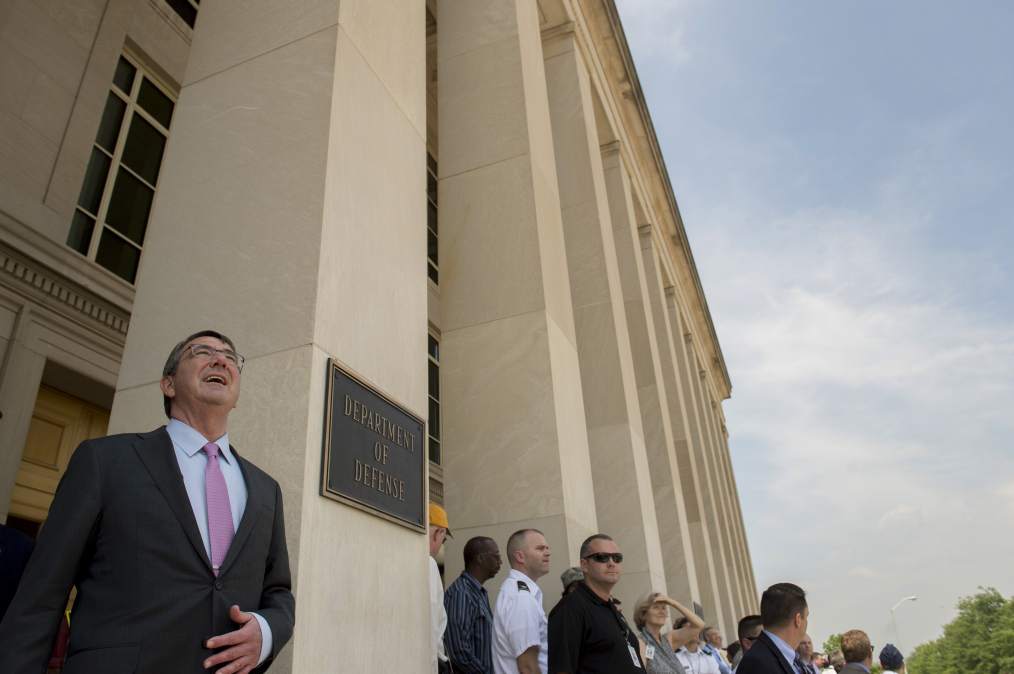
The Department of Defense released a policy Monday that allows freelance security researchers a legal way to disclose vulnerabilities in any of the department’s public-facing systems.
The DOD’s new Vulnerability Disclosure Policy is the latest in an effort to allow hackers to poke around in government systems without running afoul of the law.
“We hope that this policy will yield a steady stream of disclosures, allowing us to find and fix issues faster,” wrote Secretary of Defense Ash Carter in a blog post on Medium. “The net effect is that the Department of Defense, our service members, and the public will be safer and more secure.”
The program will be managed by HackerOne, which managed DOD’s ‘Hack the Pentagon’ pilot program run earlier this year. Last month, contracts were awarded to HackerOne and Redwood City, Calif.-based Synack, allowing crowdsourced security researchers to scour the DoD’s applications, websites and networks for vulnerabilities.
Monday also marked the first day of registration for Hack the Army, a HackerOne-led bounty program that focuses on public-facing Army websites.
“The Vulnerability Disclosure Policy and Hack the Army initiatives underscore the Department’s commitment to innovation and adopting commercial best practices,” Carter wrote. “DoD has focused on efforts to modernize our security and find ways to tap into sources of talent across the country.”
The military is not the only government sector that is employing bug bounties. Last week, the IRS announced an agreement with Synack that adds a level of vetting before hackers are allowed to poke and prod at government systems. Unlike conventional, open-crowd bug bounty programs, Synack says it rigorously vets and tracks its white-hat hackers “ensuring the customer has continuous visibility and management over all Synack Red Team activities.”
The program follows a trend in which organizations from outside the technology sector are allowing freelance hackers to find holes in their system for a monetary reward.
The full policy can be found on HackerOne’s website.
Latest Podcasts
Government
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/dod-bug-bounty-hackerone-vulnerability-disclosure-policy/