After 2016 election hacking, Illinois politicians pose cybersecurity questions to local officials
Full article1,068 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Two lawmakers are asking questions about what might have been hacked and how local election officials responded.
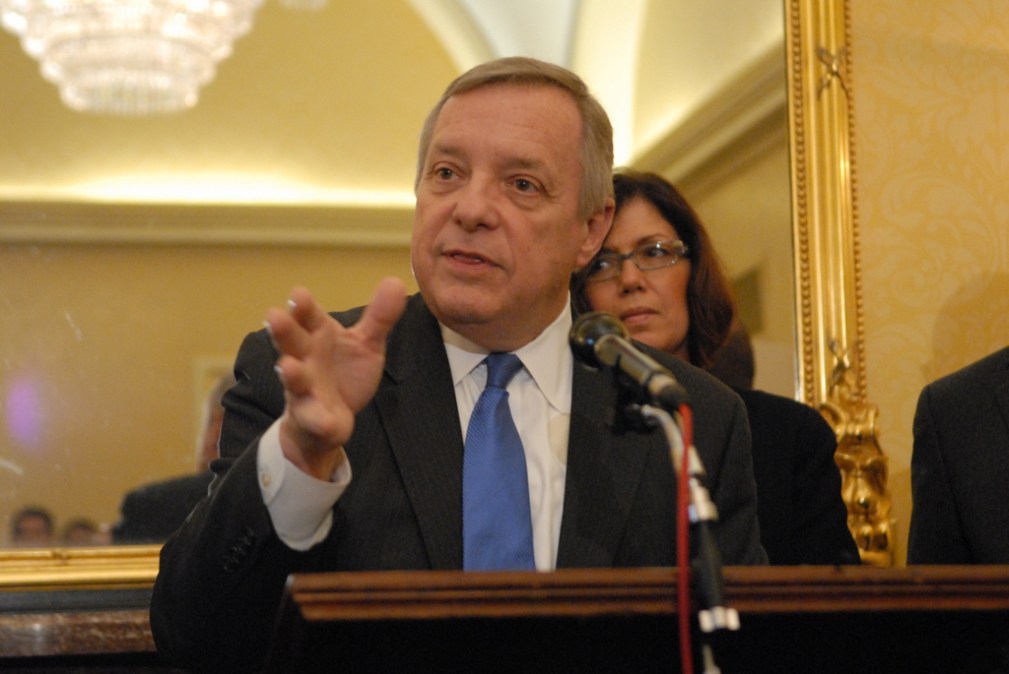
Nearly a year after Illinois election boards were targeted in a monthlong cyberattack, Sen. Dick Durbin, D-Ill., and state Sen. Michael E. Hastings, want the state’s local election authorities to assess the state’s election-system cybersecurity.
The two lawmakers are asking questions about what might have been hacked and how local election officials responded. The letter not only dives into the specifics of Illinois cybersecurity but also asks how federal and state agencies can assist in protecting the election system at all levels.
The inquiry comes as the the Senate Intelligence Committee will hold an open hearing June 21 to examine U.S. election security for the 2018 and 2020 elections and to assess Russian interference in the 2016 U.S. elections. Experts from the DHS, FBI, Illinois State Board of Elections, the National Association of State Election Directors and election cybersecurity expert J. Alex Halderman will testify.
Last year, the personal information of as many as 90,000 voters was hacked by a possible foreign attacker beginning in June 2016 and halted a full month later, according to Illinois State Board of Elections officials. The exact scope of the data breach remains unknown but personal information including drivers’ license numbers and the last four digits of Social Security numbers may have been accessed. Voting history and signatures were not captured, officials said at the time. Arizona was targeted as well.
A recent Bloomberg report citing three people with direct knowledge of the U.S. investigation into election hacking said Russian hackers hit systems in 39 total states.
The letter from Durbin and Hastings to county clerks across Illinois lauds the State and Local Cyber Protection Act of 2017, a Senate bill that aims to increase cybersecurity cooperation between the Department of Homeland Security and state and local governments — which vary widely in their ability, resources and expertise to deal with the rising tide of cybersecurity threats. The bill awaits action by the Homeland Security and Governmental Affairs Committee.
The measure would require DHS to build a website for local and state governments with information security resources and guidelines, help identify and address vulnerabilities, provide training and assistance, and ensure local and state awareness of all federal tools at their disposal.
Durbin and Hastings seek detailed answers to several broad questions on hacking, security audits, adherence to the critical cybersecurity controls outlined in the NIST framework as well as answers on how the federal and state governments should assist security efforts. Here are all the questions the local Illinois election authorities are being asked:
1. Have you been hacked or suffered from a cyber-intrusion in recent history?
2. If so, have you worked with local or national law enforcement on the matter?
3. Did you perform an audit of your systems after the BOE was hacked?
4. Have you taken any steps that would make such cyberattacks less likely to be successful in the future? What steps have you taken, if any, to better secure the identities of Illinois voters?
5. Are you implementing any of the Top 5 Critical Cyber Security Controls outlined in the National Institute of Standard and Technology Cyber Security Framework of 2014? These include:
- Inventory of Authorized and Unauthorized Devices
- Inventory of Authorized and Unauthorized Software
- Secure Configurations for Hardware and Software
- Continuous Vulnerability Assessment and Remediation
- Controlled Use of Administrative Privileges
6. How could the federal and state governments best assist your efforts to strengthen the cybersecurity of your election systems?
” It is our view that a secure election process, without the malicious interference of foreign or domestic entities, is of utmost importance and we are confident that you are dedicated to ensuring such intrusions are dealt with in a proper manner,” the two politicians write in the letter.
More Scoops
Election official says Tina Peters would be consultant, won’t have access to election systems
Shasta County registrar Clint Curtis told CyberScoop he needs Peters to help manage the county’s 2026 elections and he’s not concerned about her past conviction.
A California county wants to hire Tina Peters to help run its elections
Trump turns to private sector in offensive hacking operations memo
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/after-2016-election-hacking-illinois-will-assess-election-system-cybersecurity/