You can teach an old worm new tricks
Full article282 words · extracted from securelist.com · click to collapse

We’re seeing a lot of reports about a new version of Backdoor.Win32.IRCBot.acd. This backdoor is a fairly limited IRCBot with spy capabilities combined with MSN-Worm functionality.
Depending on the locality of the machine the backdoor sends out messages in different languages. This functionality is similar to that seen in the recent widespread AutoIT MSN-Worms, which is mostly downloaded by Backdoor.Win32.MSNMaker variants.
The interesting touch in this case is that the backdoor tries to transfer a ZIP file called “myalbum2007.zip” instead of sending out an URL to a malicious file.
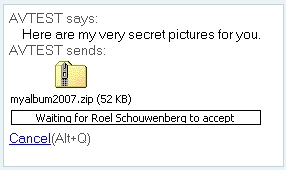
This is not entirely new, for instance the IM-Worm.Win32.Sumom family back from 2005 did the same. However it’s been quite a while since we last saw this type of propagation routine.
There are pros and cons to each type of propagation. Perhaps some cyber criminals think that websites containing malicious code get taken offline too fast for their liking. It’ll be interesting to see if sending files instead of URLs will become a proven method for MSN-Worms to spread.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/you-can-teach-an-old-worm-new-tricks/30347/