State cybersecurity authorities issue warning over Hurricane Florence scams
Full article617 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
As Hurricane Florence rips through the East Coast, scammers and hackers will very likely look to exploit the storm for financial gain.
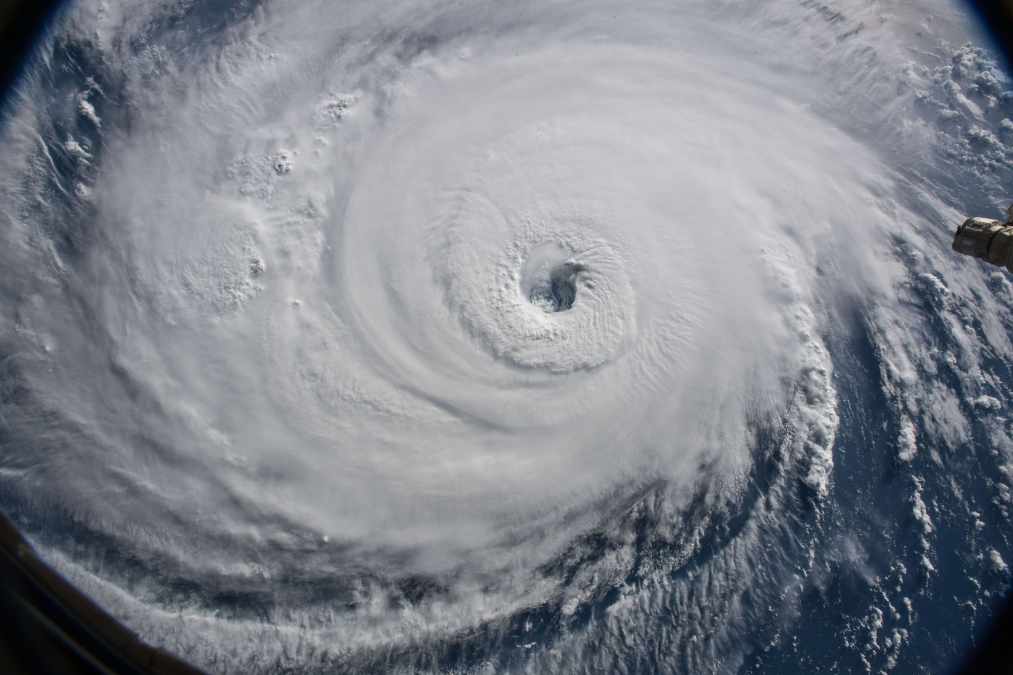
As Hurricane Florence rips through North and South Carolina, scammers and hackers will very likely look to exploit the storm for financial gain or other malicious purposes, an inter-state cybersecurity organization has warned.
Florence’s landfall — and the storms that follow — are expected to “propel the emergence of new and recycled scams involving financial fraud and malware,” the Multi-State Information Sharing and Analysis Center (MS-ISAC) said in an advisory Friday.
Hurricane Florence made landfall in North Carolina Friday morning. Though downgraded to a Category 1 storm, Florence has brought flash flood warnings and already caused more than 600,000 power outages in North Carolina, according to the state’s department of public safety.
In recent days there have been a marked increase in registered domains related to Hurricane Florence with words like “compensation” and “funds,” indicating possible fraud, MS-ISAC said. Thirteen domains associated with Florence were registered on Monday, and that number jumped to 51 on Tuesday and 65 on Wednesday, the threat-sharing center added.
The MS-ISAC, which includes representatives from all 50 states, also predicted that malicious computer users will send phishing emails related to Florence that contain embedded malware or attempt to redirect users to infected websites.
The phishing and scamming attempts are expected to continue as the Carolinas recover from the storm.
“It is highly likely that more scams and malware will follow over the course of the recovery period,” the advisory says, cautioning internet users to be careful where they click. New Jersey’s cyberthreat-sharing agency also circulated the notice.
North Carolina’s Department of Information Technology has also warned computer users of phishing expeditions tied to the disaster, as has the Department of Homeland Security’s threat-sharing center.
Scott Aaronson, vice president of security and preparedness at trade group Edison Electric Institute, urged electric customers to “be wary of criminals impersonating electric company employees.”
Opportunistic scammers will try to exploit natural disasters, Aaronson told CyberScoop, adding that electric customers should know that utilities “do not require payment to restore electricity after a natural disaster or other related outage.”
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/hurricane-florence-scams-hacking-phishing-ms-isac/