Windows Messenger spam
Full article308 words · extracted from securelist.com · click to collapse



We are seeing an increase in spam sent via the MS Windows Messenger service. Spammers are abusing a feature in the service to trigger fake error or warning messages from the messenger service.
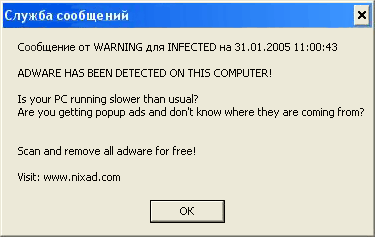
Very often, the message warns users that a significant number of spyware programs have been detected on their machine and recommends that users download an anti-spyware program.
Naturally, this is an attempt to trick users into downloading Trojans, in the worst case scenario, or in the best case scenario, useless utilities that imitate spyware detection. In any case, adware and spyware are neither detected nor removed.
What we are seeing is virus writers adapting the never-ending social engineering technique of picking up on a well-publicized security issue. This time the media attention and public awareness of the term spyware is being exploited.
We urge users to be aware that such messages are fake and to avoid downloading any programs advertised in this manner. This kind of spam can be prevented on PCs where you have admin rights by disabling the Messenger service C:WINDOWSSystem32svchost.exe -k netsvcs or Control Panel -> Administrative Tools -> Services -> Messenger.
Read more about MS Windows Messenger Service:
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/windows-messenger-spam/29985/