Malware in Lenovo
Full article249 words · extracted from securelist.com · click to collapse



Some of you might have seen the blogpost that our colleague Ryan Naraine has put at ZDNET about malware being distributed along with a pack of Lenovo Thinkpad drivers.
Here are some more details on that story. Working together with fellow researchers in Microsoft we discovered an URL that pointed to a file on IBM’s ftp site that looked like a false positive, so we sent them a ‘heads up’ message.
Careful analysis of the file, which was named ‘q3tsk04us13.exe’ (Lenovo Trust Key Software for WinXP) showed that the file in question did indeed contain a virus named Virus.Win32.Drowor.a. Luckily, the virus was broken and it didn’t work.
Naturally, we’ve notified IBM immediately – and IBM took the file offline.
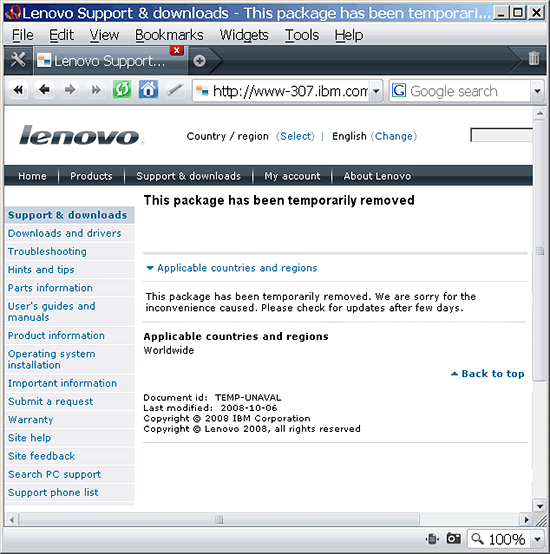
We’d like to salute IBM’s prompt response and to thank our friends at MS for their initial analysis!
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/malware-in-lenovo/30470/