Data breach notices become more opaque, leaving consumers in the dark
Full article876 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
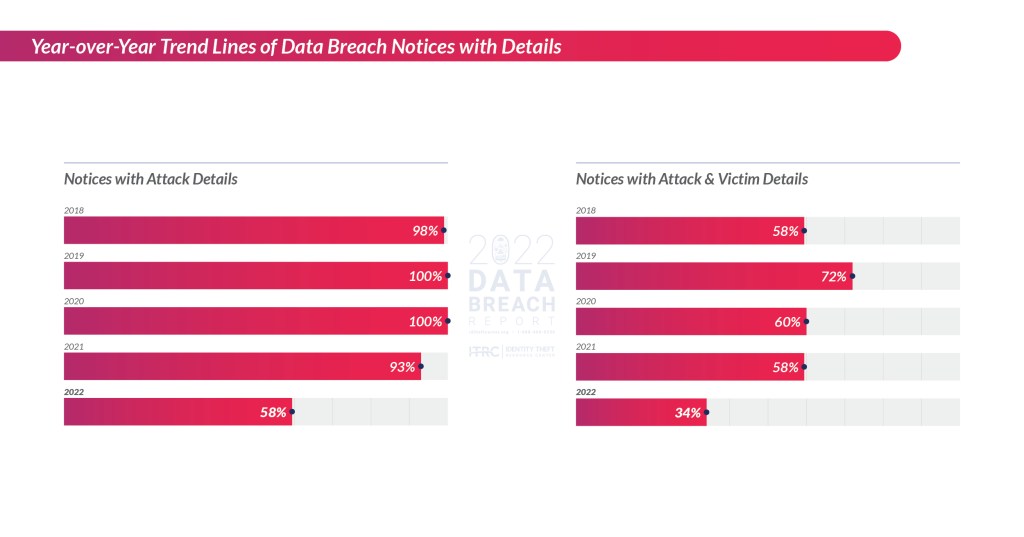
Of the 1,802 breaches the Identity Theft Resource Center tracked in 2022, 66% of notices lacked details about the attack and victims.
Data breach disclosures that included specific details for consumers dropped dramatically in 2022, according to the most recent data from the Identity Theft Resource Center.
Of the 1,802 breaches the group tracked in 2022, 66% did not include victim and attack details such as root cause. It’s a dramatic decline from two years ago when 100% of reported breaches tracked by the center included details about attack vectors.
Data breaches in 2022 affected roughly 400 million individuals, according to the ITRC report. The trend toward less descriptive disclosures makes it harder for consumers to protect themselves and for policymakers and cyber defenders to respond, experts say.
“That’s hundreds of millions of people who are left in the dark about what’s happened to them, and more importantly, what they can actually do about it,” Eva Velasquez, president and chief executive order of the Identity Theft Resource Center, said at an event Wednesday co-hosted with Better Identity Coalition.
“If your card numbers or your bank account numbers were stolen, there are different steps that you should take than if it was just your social,” said James Ruotolo, senior manager in fraud risk mitigation at Grant Thornton. “There are certain things that consumers can and should do to protect themselves. None of that information is being communicated in the vast majority of the breach notices that I’ve seen.”
Companies are currently subject to a patchwork of state data breach laws, many of which don’t require victim details. The Federal Trade Commission has gone after companies for covering up or failing to disclose breaches, such as when it ordered CafePress last year to take on new security protocols in light of covering up multiple breaches.
But current enforcement measures might not be incentive enough for reporting.
“I don’t think that there’s much fear of the consequences. The FTC can’t bring the same kind of fines it did before. State [attorneys general] are overworked. Courts aren’t granting standing when you go to court as a private litigant,” said John Breyault, vice president of public policy at the National Consumers League. “So, what’s the downside of not putting more information out there that’s going to potentially harm your business?”
The report puts the number of data compromises in 2022 at 1,802, just 60 short of an all-time high set in 2021. Twitter had both the first and sixth largest breaches on the list with approximately 220 million victims of a suspected breach revealed in December and roughly 5.5 million victims in November tied to a previously reported breach of Twitter’s API in 2021. Twitter maintains that there’s no evidence of the breach that involved 220 million victims.
ITRC attributed the slight slowdown in breaches last year to Russia-based cybercriminals being distracted by the war in Ukraine, a theory several cybersecurity experts have also posed.
The ITRC report also notes that cybercriminals are moving away from zero-day exploitations to going after weaknesses in APIs, a problem highlighted a recent breach of T-Mobile that effected up to 37 million consumers.
More Scoops

Lawmakers spring to save ID theft services for OPM breach victims, with expiration looming
Sen. Mark Warner, D-Va., and Del. Eleanor Holmes Norton, D-D.C., hope to make the services permanent before they end next month.
LastPass breach exposes how US breach notification laws can leave consumers in the lurch
FCC proposes stronger data breach rules, faster notifications for telecoms
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/data-breach-disclosures-opaque/