Popular technology that hospitals use to send lab samples is vulnerable, researchers found
Full article551 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
There's no evidence attackers have exploited the software issue for their own gain.
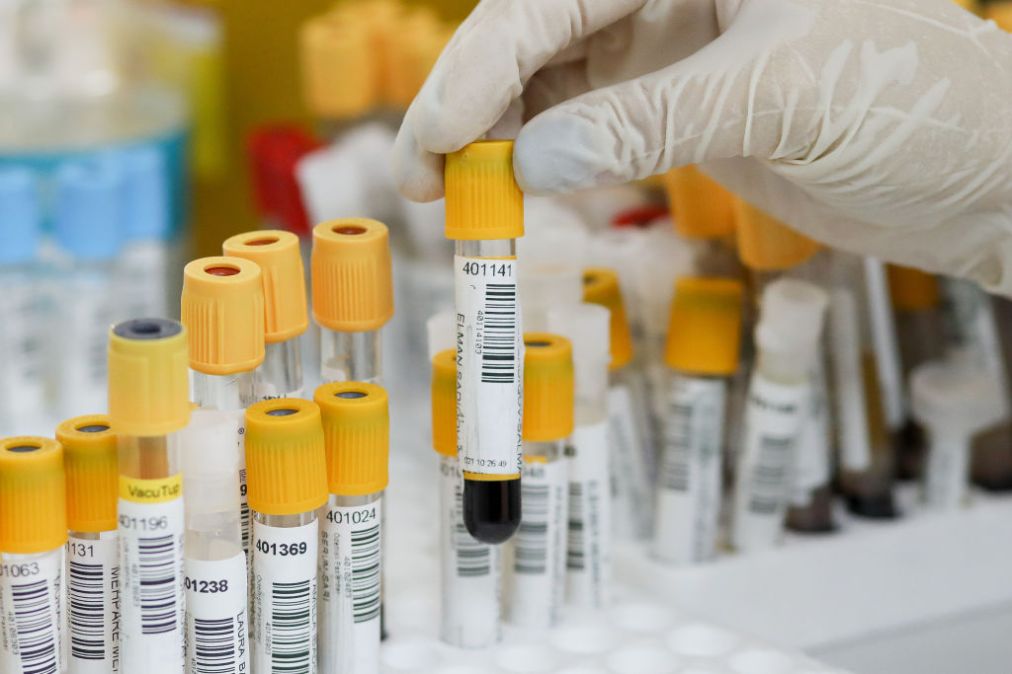
A key technology that hospitals use to deliver medications, blood and other vital lab samples is at significant risk of hacking, new findings suggest.
Researchers from the security vendor Armis found nine critical vulnerabilities in the control panel that powers the Translogic pneumatic tube systems from logistics automation company Swisslog Healthcare.
The Translogic pneumatic tube system is used by more than 3,000 hospitals worldwide and over 80% of hospitals in North America, according to a report published Monday. Researchers warn that the vulnerability could be used to launch a ransomware attack against the delivery system, crippling hospital functions. Hackers could also use such access to leak sensitive medical data.
There’s no evidence attackers have exploited the software issue for their own gain.
Ransomware attacks against hospitals have risen dramatically in recent years, costing organizations millions of dollars and sometimes crippling emergency care.
Five of the vulnerabilities, which researchers have collectively named “PwnedPiper,” can be used to gain access to a hospital’s network and take over a Nexus station without verification. From there, hackers could use the access to scan for data including employee credentials to get access to the wide pneumatic tube system.
“With so many hospitals reliant on this technology we’ve worked diligently to address these vulnerabilities to increase cyber resiliency in these healthcare environments, where lives are on the line,” said Ben Seri, Armis vice president of research.
Armis disclosed the vulnerabilities to Swisslog on May 1 and has been working with the manufacturer on a patch. Swisslog wrote in a security update to consumers that seven of the identified vulnerabilities were removed in a software release update and it has made mitigations for a remaining vulnerability. (Swisslog identified counts two of the vulnerabilities identified by Armis as one.)
Seri and fellow Armis researcher Barak Hadad will present the findings at Black Hat on Wednesday and Thursday.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/pneumatic-tubes-ransomware-hospitals-swisslogic-armis/