Google takes swift action to kill massive ad fraud campaign in Play store
Full article541 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Google killed a massive ad fraud operation evident in the Google Play Store just one day after a security firm publicly revealed the malicious campaign.
Google killed a massive ad fraud operation evident in the Google Play Store just one day after a security firm publicly revealed the malicious campaign.
A total of 41 individual smartphone applications, which were available for download on Android devices earlier this week, have been removed in the last 24 hours. Each of those applications were connected to a larger scheme uncovered Thursday by U.S. cybersecurity firm Check Point. Forbes magazine was first to notice the swift action on the part of Google.
Check Point discovered and published technical details of the scheme, perpetrated by South Korean software company Kiniwini, which involved bobby-trapped apps with rogue code causing devices to open webpages in the background and click on banners. The result was a spike in revenue for the company, which sold banner ads to clients valued in relation to engagement. Most of these maligned apps were free games.
A Google spokesperson did not respond to a request for comment.
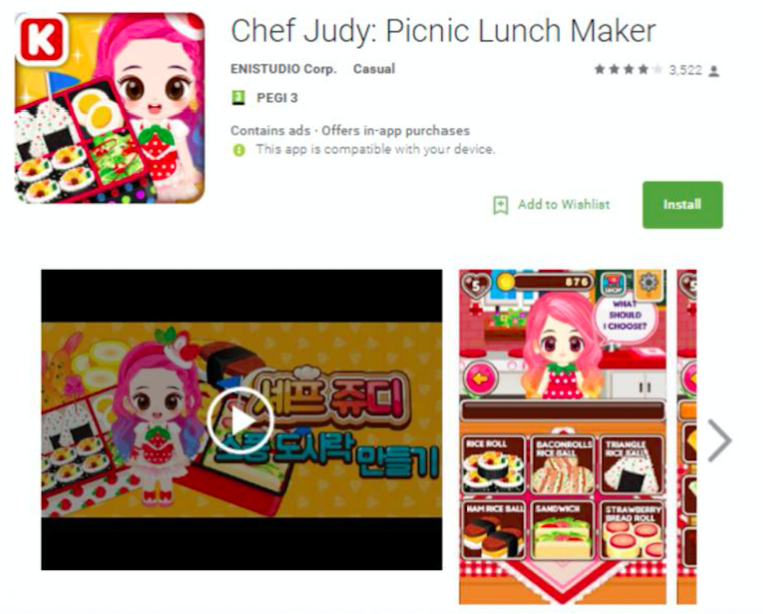
A popular app found in the Google Play Store named “Chef Judy” carried malicious computer code / Image by Check Point
Many of the apps developed by Kiniwini also displayed a variety of different, internal advertisements. At times, a flood of these advertisements within the apps would lock a user from doing anything aside from inadvertently clicking on a banner, according to Check Point.
The Kiniwini incident underscores a larger issue affecting the Google Play Store ecosystem.
Security researchers have published multiple examples of harmful Android apps existing within the Google Play Store in recent months. In some cases, these apps bypassed detection technology designed by Google before being posted for download.
Some have described the operation by Kiniwini as the largest malware campaign ever found on the Google Play Store. A blog post on the company’s website reportedly recognizes that Google took action to remove their applications.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/google-ad-fraud-chef-judy/