Forcepoint execs: CrowdStrike's warranty is nothing more than marketing
Full article724 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Forcepoint CEO Matt Moynahan: "It probably puts you on the defensive more so than not."
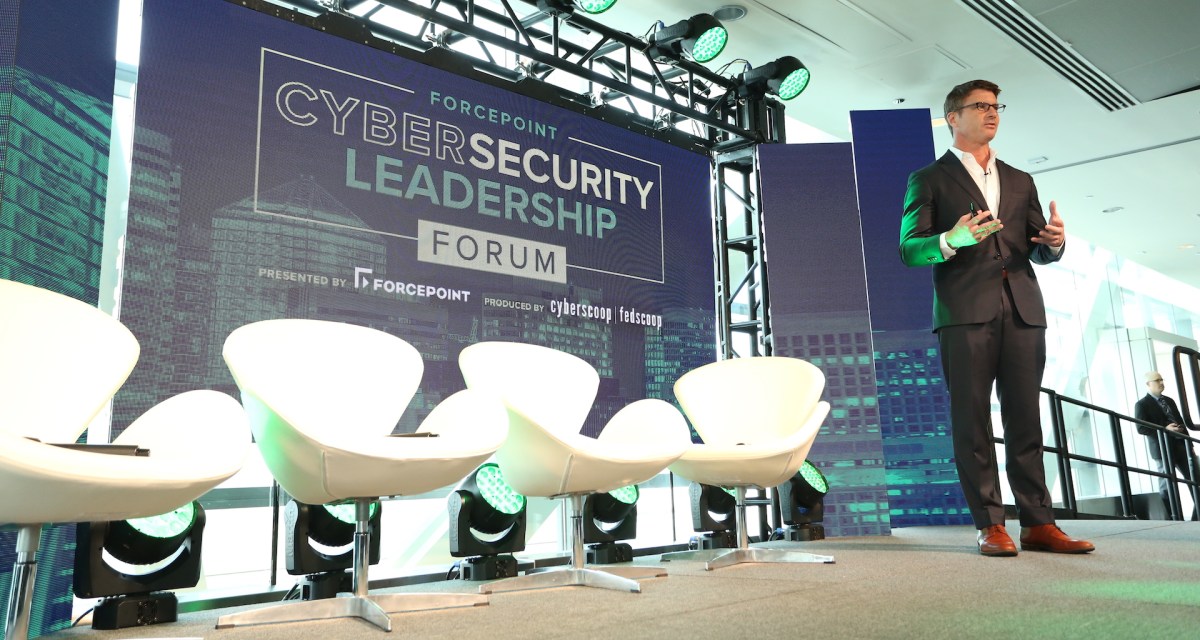
Two Forcepoint executives have criticized CrowdStrike’s recent announcement of a breach prevention warranty as nothing more than a marketing stunt.
Earlier this month, Silicon Valley-based CrowdStrike announced a warranty would cover the company’s Falcon Endpoint Protection Complete customers for up to $1 million if a breach happens in the environment it was hired to protect.
Matt Moynahan, CEO of Austin-based Forcepoint, told CyberScoop that it’s standard business practice to place liability terms in contracts with customers, yet to take those provisions and make them public doesn’t mean the product will better secure an enterprise.
“I think it’s a marketing gimmick,” Moynahan said Wednesday at the Cybersecurity Leadership Forum presented by his company and produced by CyberScoop and FedScoop. “I don’t think that changes anything fundamentally about the way the security industry operates or quite frankly the effectiveness of it. It probably puts you on the defensive more so than not. You won’t see us do it any time soon.”
Nico Fischbach, global CTO for Forcepoint, said that enterprises could be lulled into a “false sense of security” if they seek similar warranties from their cybersecurity providers.
“There is no quick fix to cybersecurity threats,” Fischbach said. “A warranty of $1 million isn’t actually a lot when it comes to the entire cost of a breach, although it will certainly help to start to fix the problem.”
Fischbach also says that instead of relying on warranties, CISOs may want to explore cyber insurance policies. That’s an option CISOs are increasingly relying upon: In 2017, package cyber premiums grew 54 percent to $2 billion for the year, according to Fitch Ratings.
However, Fischbach says insurance policies are a small piece of the puzzle when protecting an enterprise.
“Cyber insurance is part of a CISO’s overall risk management arsenal, but far more important is understanding the overall risk posture and exposure: knowing how your people interact with your data and how you can best prevent and mitigate against the threats,” he said.
“For those considering buying warranties or insurance, I would advise firstly gaining a deep understanding of where your data is located, and classify it. From this position, you can assign the dollar value to the data, and proceed accordingly. But if you’re insured, you should not relax: We all operate in a rapidly evolving threat environment and must adapt and change along with it.”
In response, CrowdStrike said in a statement to CyberScoop: “For far too long, the cybersecurity industry has made claims of protection without providing evidence or guarantees, as is commonplace in other industries.”
“CrowdStrike changed that by launching a breach prevention warranty of up to $1 million,” the statement continued. “We develop products and capabilities that as a company we fully stand behind. Customers put their trust in us because we deliver on our commitments. We encourage competitors to do the same.”
Update, 6/25/18: The story has been updated with comments from CrowdStrike.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/forcepoint-crowdstrike-warranty-marketing-gimmick/