Open-source security group pulls out of U.S. grant, citing DEI restrictions
Full article895 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Listen to this article
0:00
Learn more.
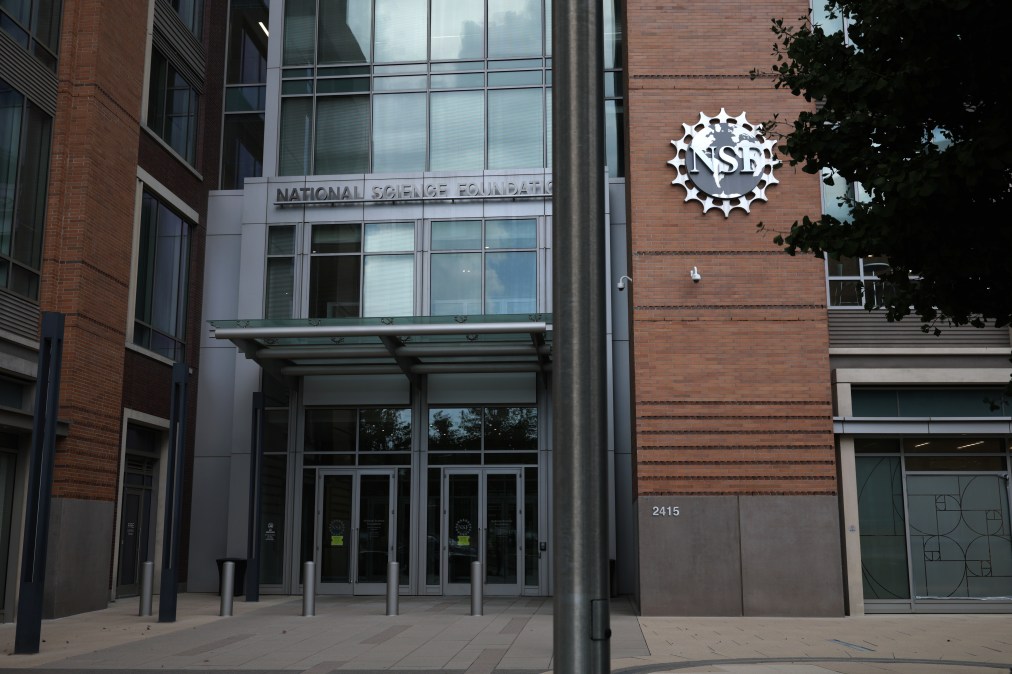
The Trump administration’s zeal to stamp out diversity, equity and inclusion programs is affecting national cybersecurity research, as a key open-source security foundation announced it would reject federal grant funding.
The Python Software Foundation (PSF), which promotes safe and secure Python coding practices and helps oversee PyPI, the world’s largest open-source code repository for Python, said Wednesday it would withdraw from a $1.5 million research grant from the National Science Foundation.
Loren Crary, deputy executive director at the PSF, said her organization was initially honored to have its project — which would have addressed structural vulnerabilities in Python and PyPI — selected. Both are heavily used by software developers today.
However, she said the organization could not agree to contract language on diversity, equity and inclusion, which went well beyond the specific work that would be performed for the government.
“These [contract] terms included affirming the statement that we ‘do not, and will not during the term of this financial assistance award, operate any programs that advance or promote DEI, or discriminatory equity ideology in violation of Federal anti-discrimination laws,’” Crary wrote Monday on the foundation’s website. “This restriction would apply not only to the security work directly funded by the grant, but to any and all activity of the PSF as a whole.”
Crary added that the contract also included a “claw back” provision that would allow the government to rescind previously approved and transferred funds.
“This would create a situation where money we’d already spent could be taken back, which would be an enormous, open-ended financial risk,” she wrote.
The primary purpose of the NSF grant in question (NSF-24-608) is to fund projects focused on the “Safety, Security, and Privacy of Open Source Ecosystem.” Its stated goal is “to catalyze meaningful improvements in the safety, security, and privacy of the targeted [open source ecosystem] that the [ecosystem] does not currently have the resources to undertake.”
Funds from this program “should be directed toward efforts to enhance the safety, security, and privacy characteristics of the open-source product and its supply chain as well as to bolster the ecosystem’s capabilities for managing current and future risks, attacks, breaches, and responses,” the NSF page for the grant states.
While PSF appeared poised to accede to the administration’s anti-DEI requirements for its grant work, Crary indicated the organization was not willing to extend that ban to its larger work, noting that the organization has always been committed to fostering diversity and equity in the field.
Indeed, the group’s mission statement is “to promote, protect and advance the Python programming language, and to support and facilitate the growth of a diverse and international community of Python programmers.”
With an annual budget of $5 million, a two-year, $1.5 million injection of funding would have been “easily” the largest grant the organization had ever received. But Crary said agreeing to the government’s contract language would be a “betrayal” of those principles.
“We’re disappointed to have been put in the position where we had to make this decision, because we believe our proposed project would offer invaluable advances to the Python and greater open source community, protecting millions of PyPI users from attempted supply-chain attacks,” Crary wrote.
The PSF’s proposal would have included the creation of automated tooling to review code packages uploaded to PyPI, replacing the site’s current review process, which Crary called “reactive.”
“These novel tools would rely on capability analysis, designed based on a dataset of known malware,” Crary said. “Beyond just protecting PyPI users, the outputs of this work could be transferable for all open source software package registries, such as NPM and Crates.io, improving security across multiple open source ecosystems.”
When CyberScoop reached out to NSF for comment, an automated reply was sent back stating that “due to a lapse in government funding, most National Science Foundation staff will not be receiving or responding to email until further notice.”
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Election official says Tina Peters would be consultant, won’t have access to election systems
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/python-software-foundation-rejects-federal-grant-funding-citing-dei-restrictions/