Cybercriminals scam two federal agencies via remote desktop tool, CISA warns
Full article685 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
CISA and the NSA warned federal agencies that malicious hackers used legitimate remote monitoring and management software to execute scams.
Cybercriminals duped federal employees into downloading remote monitoring and management software and then used it to execute scams to steal money from victims’ bank accounts, top cybersecurity officials said Wednesday.
In an alert warning agencies about the malicious use of remote management software, in this case ConnectWise Control and AnyDesk, officials said that while the specific activity “appears to be financially motivated and targets individuals, the access could lead to additional malicious activity against the recipient’s organization—from both other cybercriminals and [advanced persistent threat] actors.”
The joint alert from the Cybersecurity and Infrastructure Security Agency, National Security Agency and Multi-State Information Sharing and Analysis Center did not specify which agencies were affected, but noted that at least two were victims.
Additionally, the alert said help desk-themed phishing emails were sent since at least June 2022 to multiple federal civilian agencies. CISA detailed the two instances of suspected malicious activity discovered in October using the federal intrusion detection program known as EINSTEIN. In mid-June, a federal civilian agency received a phishing email and the victim called a phone number contained in the message and led them to a malicious domain. In mid-September, CISA identified traffic flowing between an agency network and a malicious domain.
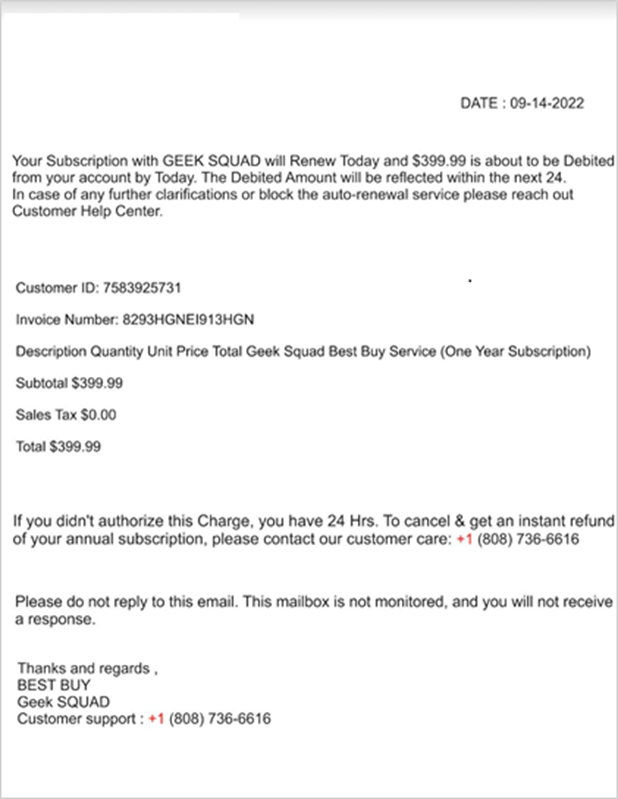
The campaign continued until at least early November, the alert said. The hackers impersonated help desk services such as Geek Squad Services, general tech support owned by Best Buy, as well as Norton, Amazon, McAfee and PayPal in order to dupe victims. Once the hackers had access to the victims’ machines, they could potentially sell any network access to other cyber criminals or APT groups, according to the alert. “This campaign highlights the threat of malicious cyber activity associated with legitimate RMM software.”
Patrick Briggs, chief information security officer for ConnectWise, said in an emailed statement that “when alerted of this behavior, ConnectWise regularly issues take-down requests to remove malicious sites and domains. We are reaching out to the impacted federal agencies for additional information that can help us take further steps to educate and support partners.”
The report warned that, generally, remote management software does not trigger antivirus or anti-malware defenses and that hackers can use legitimate RMM software in a portable executable which can “bypass administrative privilege requirements and software management control policies.” Additionally, RMM software can reduce the need for a malicious hacker to use custom malware and can act as a backdoor to keep on the victim’s network.
Updated Jan. 26, 2023: This story has been updated to include a statement from ConnectWise.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/cisa-federal-agency-refund-scam-remote-software/