Critical infrastructure policy rewrite expected to ‘emphasize’ CISA, NSC official says
Full article600 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The rewrite of presidential policy directive 21 is expected to place CISA in a more prominent position to help combat threats to critical infrastructure.
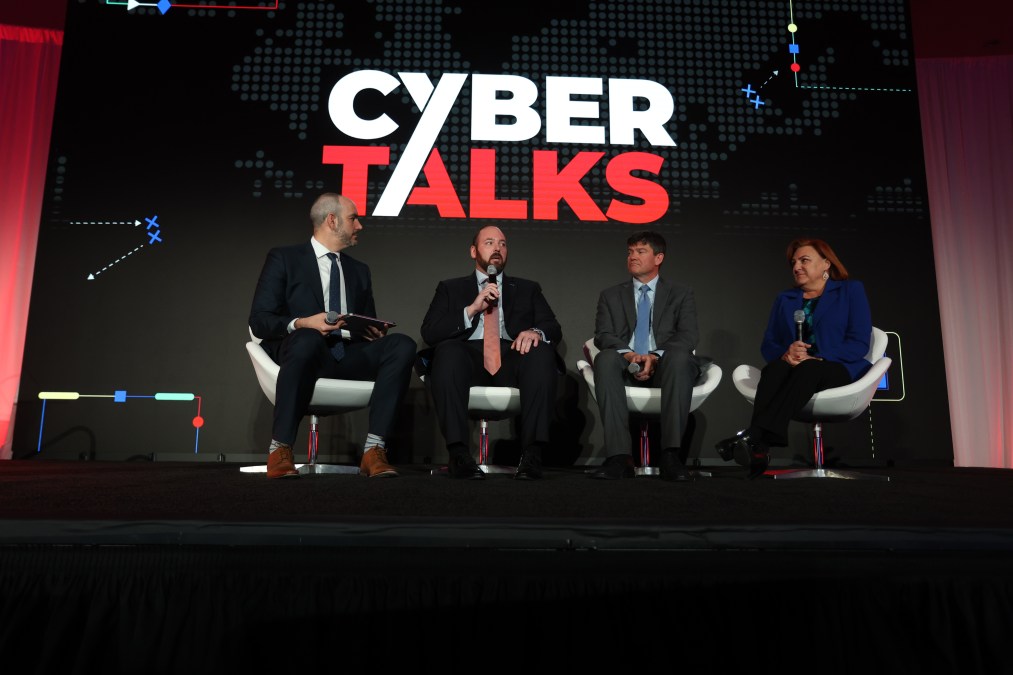
The rewrite of a presidential policy directive that defines how the federal government manages and interacts with the 16 critical infrastructure sectors will more clearly define the role of government agencies, a National Security Council official said Thursday.
Jonathan Murphy, director of critical infrastructure cybersecurity at the NSC, said that the rewrite of presidential policy directive 21 will “emphasize” the increasing role of the Cybersecurity and Infrastructure Security Agency.
Additionally, the rewrite will ensure that the sector risk management agencies that oversee the critical sectors “lay out a positive vision for our organizing structure, but also how to execute that responsibility,” Murphy said.
“We’re looking across all of the 16 infrastructure sectors to identify where levers exist to enable the federal government to have positive, reliable outcomes [and] set minimum cybersecurity requirements for those critical infrastructure sectors,” he added.
The White House — through the Office of the National Cyber Director and the Office of Management and Budget — is also exploring how to harmonize existing cybersecurity regulations for those 16 sectors. The change comes after years of lax or nonexistent regulations for critical sectors, while critical services are also coming under steady ransomware attacks.
The administration’s national cybersecurity strategy stressed that the voluntary management of cyber risks by critical sectors is no longer acceptable.
The decade-old policy was issued during the Obama administration — before CISA was created, five years ago on Thursday — and is a much anticipated policy rewrite. The strategy was not created with cybersecurity concerns heavily in mind, particularly as cyber threats like ransomware have pummeled critical infrastructure sectors in recent years.
The policy has only been updated once: in the 2021 National Defense Authorization Act, to add responsibilities to the sector risk management agencies (SRMA) in charge of each sector.
The CSC 2.0, which is a continuation of the Cyberspace Solarium Commission established by Congress in 2019, released a series of recommendations and criticisms for the Biden administration’s rewrite, including increasing the resources of the agencies that are not properly equipped to act as an SRMA.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Election official says Tina Peters would be consultant, won’t have access to election systems
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/critical-infrastructure-policy-rewrite-expected-to-emphasize-cisa-nsc-official-says/