AVAR 2009
Full article231 words · extracted from securelist.com · click to collapse

Out of the four major AV Security Conferences out there, that is, EICAR, The CARO Technical Workshop, Virus Bulletin, AVAR is the last throughout the year.
Its current edition started yesterday, in the ancient city of Kyoto, the imperial capital of Japan. The program features a number of prominent speakers, among them our very own Eugene Kaspersky and Stefan Tanase.
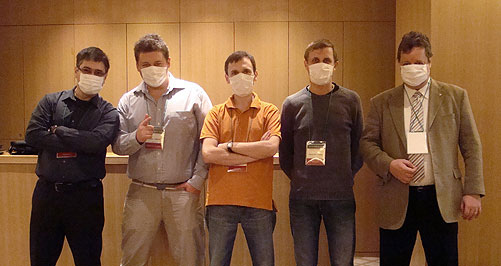
With current flu epidemics running around the world, we must salute the organizer’s initiative to distribute masks together with the delegate packs. Here’s the Kaspersky team, looking prepared for the worst:
From left to right: Costin, Stefan, Andrey, Aleks and Michael, with Nikita behind the lens.
Until the next time, sayonara from Kyoto, and have a good and germ-free weekend!
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/avar-2009/30581/