China-Aligned Hackers Hide PeckBirdy Malware C2 Inside Casino and Adult Websites
Infoblox found China-aligned actors hiding PeckBirdy malware C2 inside fake Chinese-language casino and adult websites, evading security scans via service workers and WebSockets.
Infoblox reported that China-aligned actors behind the PeckBirdy JScript C2 framework conceal command-and-control inside low-quality Chinese-language casino and adult websites, extending Trend Micro's earlier findings that tied the framework to backdoors including MKDOOR and HOLODONUT. One decoy, vip311[.]cc, embedded JavaScript linked to cache-mcp[.]com and registered a service worker connecting to mcp-source[.]online over WebSocket; at publication mcp-source[.]online had zero VirusTotal detections, showing how the layered design evades conventional scanning. The campaign has been active since at least 2023, and just over 3% of Infoblox enterprise customers resolved at least one PeckBirdy C2 domain, with education, IT, banking and government among observed sectors.
- PeckBirdy is a JScript-based C2 framework delivering modular backdoors including MKDOOR and HOLODONUT against Asian government and gambling targets.
- Decoy sites register service workers and use WebSocket links, which conventional web scanners and reputation systems may miss.
- Active since at least 2023; just over 3% of Infoblox enterprise customers resolved at least one PeckBirdy C2 domain.
- Education, IT, banking and government organizations appeared among targets; 3-10 distinct C2 lookups warrant incident-response investigation.
- Roughly 1.7 million illegal Chinese-language gambling domains create camouflage that makes APT C2 look like consumer fraud.
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | 11170011.com | ity casino websites in this network. A recently active site 11170011[.]com featuring “Venetian Macao” branding, translated into Engl |
| domain | 80074.cc | Language Casino Domains (Type 1) 11170011[.]com puqxr[.]com 80074[.]cc PeckBirdy C2 and Decoy Domains (Type 3) vip311[.]cc Decoy |
| domain | appcasino.online | Scambling Domains (Type 2) dollycasino[.]com dragobet[.]net appcasino[.]online Illegal Chinese-Language Casino Domains (Type 1) 11170011 |
| domain | cache-cdn.org | ly three. A previously identified PeckBirdy-related domain, cache-cdn[.]org, had 13 detections illustrating how visibility drops as o |
| domain | cache-mcp.com | embedded JavaScript associated with the PeckBirdy C2 domain cache-mcp[.]com. The script registered a service worker and connected to |
| domain | dollycasino.com | l pattern. IOCs Category Domains Scambling Domains (Type 2) dollycasino[.]com dragobet[.]net appcasino[.]online Illegal Chinese-Languag |
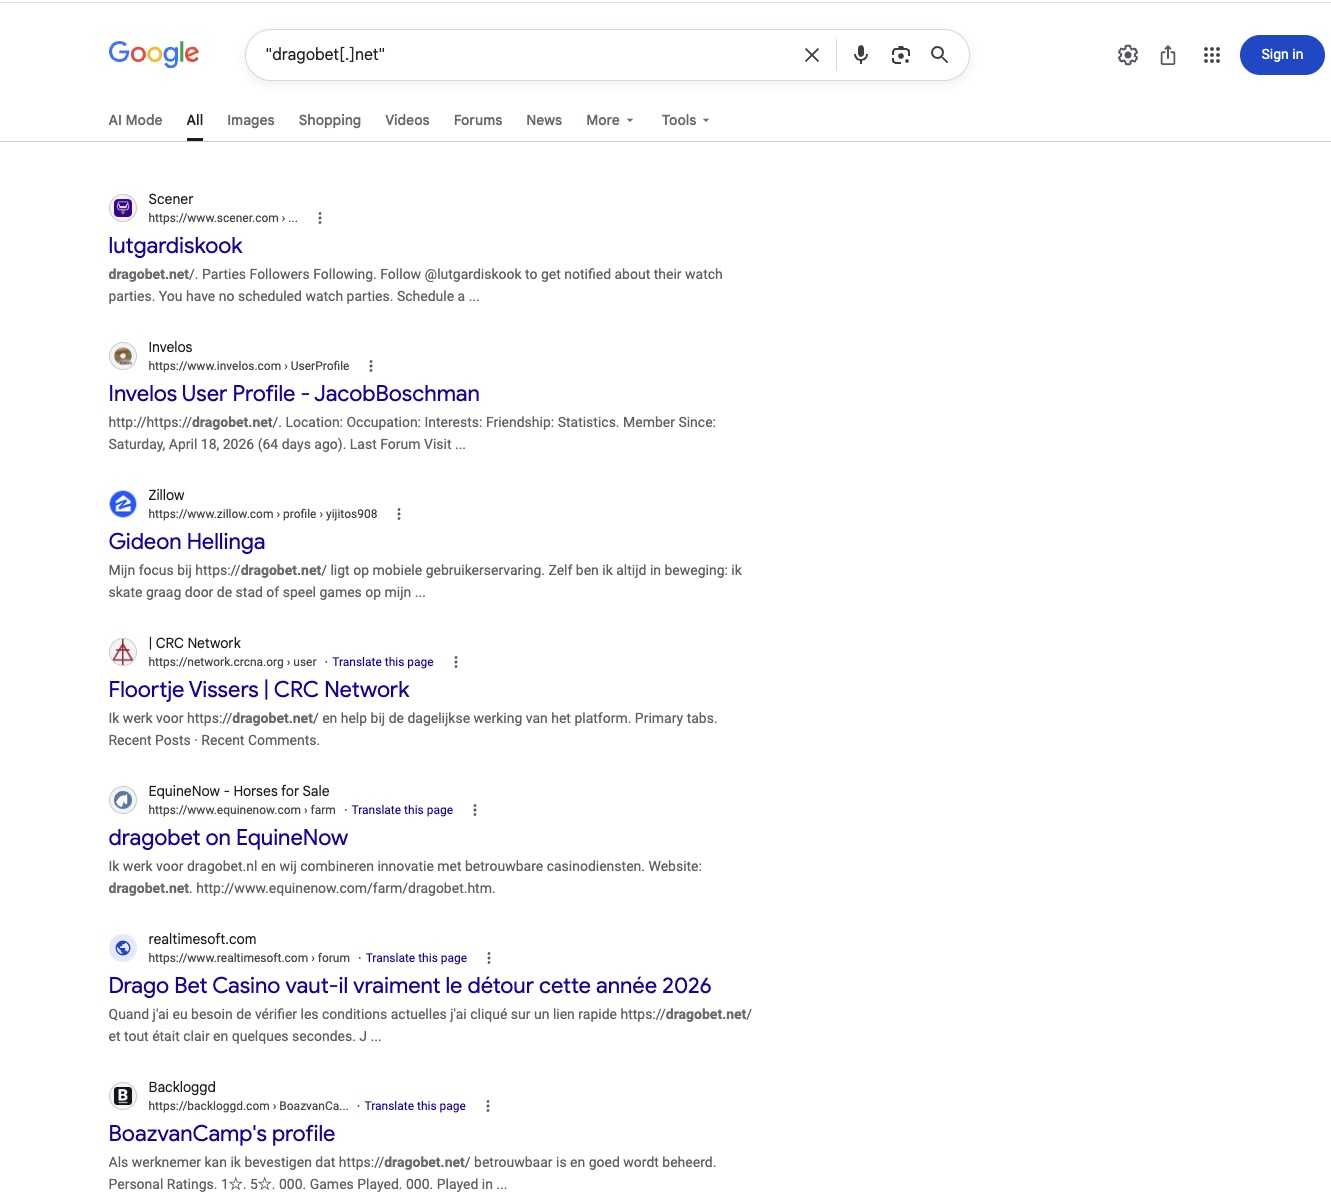
| domain | dragobet.net | y and unworthy of investigation. If you search this domain “dragobet[.]net” on Google it quickly becomes clear that someone ran a bl |
| domain | githubassets.net | is not automatically evidence of compromise. In particular, githubassets[.]net a PeckBirdy-associated typosquat can be reached through c |
| domain | mcp-source.online | ervice worker and connected to another infrastructure node, mcp-source[.]online, through WebSocket communications. That layered design ma |
| domain | puqxr.com | gal Chinese-Language Casino Domains (Type 1) 11170011[.]com puqxr[.]com 80074[.]cc PeckBirdy C2 and Decoy Domains (Type 3) vip311 |
| domain | vip311.cc | the threat actors have refined the camouflage. One example, vip311[.]cc, presented itself as a Chinese-language KY-branded casino |
Full article920 words · extracted from gbhackers.com · click to collapse
China-aligned threat actors are concealing the PeckBirdy command-and-control framework inside low-quality Chinese-language casino and adult websites.
Exploiting a vast and routinely ignored category of internet infrastructure to blend malware traffic into apparent gambling activity.
The activity expands on earlier findings by Trend Micro, which identified PeckBirdy as a flexible JScript-based C2 framework used by China-aligned actors against Asian government entities, private organizations, and gambling-sector targets.
PeckBirdy abuses web-delivered scripts and living-off-the-land binaries to support remote JavaScript execution and modular backdoor delivery.
Trend Micro linked the framework to campaigns that injected malicious scripts into gambling websites; visitors could receive the core PeckBirdy payload, enabling operators to issue commands and deploy follow-on malware.
The framework has been associated with backdoors including MKDOOR and HOLODONUT.
Infoblox’s latest investigation found that the threat actors have refined the camouflage.
One example, vip311[.]cc, presented itself as a Chinese-language KY-branded casino site but embedded JavaScript associated with the PeckBirdy C2 domain cache-mcp[.]com.
The script registered a service worker and connected to another infrastructure node, mcp-source[.]online, through WebSocket communications.
That layered design matters because conventional web scanning and reputation systems may not fully observe service-worker registration, dynamic JavaScript behavior or live WebSocket connections.
At the time of Infoblox’s publication, mcp-source[.]online had no VirusTotal detections, while cache-mcp[.]com had only three.
A previously identified PeckBirdy-related domain, cache-cdn[.]org, had 13 detections illustrating how visibility drops as operators shift to less easily discovered infrastructure.
A physical presence in Macau or elsewhere, is unlikely to have any actual association with the low-quality casino websites in this network.
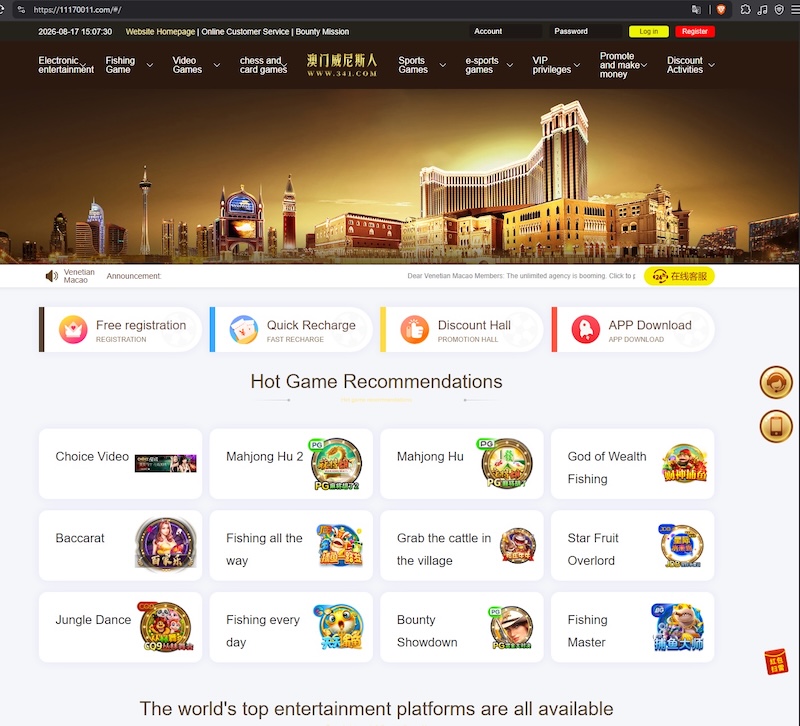
Infoblox Threat Intel said in a report shared with GBhackers, domains posing as gambling sites can function as decoys for an advanced persistent threat campaign active since at least 2023.
PeckBirdy Malware C2
The campaign is now using Chinese-language adult websites alongside casino pages, broadening the decoy ecosystem without materially changing the underlying tradecraft.
These websites are not necessarily designed to attract legitimate customers; rather, they are operational cover intended to make malicious domains appear disposable, low-priority and unworthy of investigation.
If you search this domain “dragobet[.]net” on Google it quickly becomes clear that someone ran a blackhat SEO campaign spamming websites all over the internet with this domain earlier this year.
Infoblox separates the wider casino ecosystem into three categories that can look nearly identical in a browser but serve very different criminal objectives.
The largest category consists of illegal Chinese-language gambling sites, estimated at more than 1.7 million domains. These sites support illicit betting, underground banking and money laundering operations.
A second category, dubbed “scambling,” uses polished but fraudulent casino platforms to take deposits while blocking or indefinitely delaying withdrawals.
The third, much smaller category comprises PeckBirdy casino decoys, whose core purpose is espionage-oriented intrusion support and malware C2 communications.
This overlap creates a defensive blind spot. Security teams may classify a gambling domain as a policy violation, nuisance or consumer-fraud concern and fail to investigate the DNS, JavaScript and network behavior behind it.
In the PeckBirdy cases, that assumption can allow an APT-linked communications channel to persist unnoticed.
The UN Office on Drugs and Crime has described illegal online gambling as a core financial pillar of transnational organized crime in Southeast Asia, increasingly integrated with cyber-enabled fraud, underground banking, cryptocurrency laundering and human trafficking.
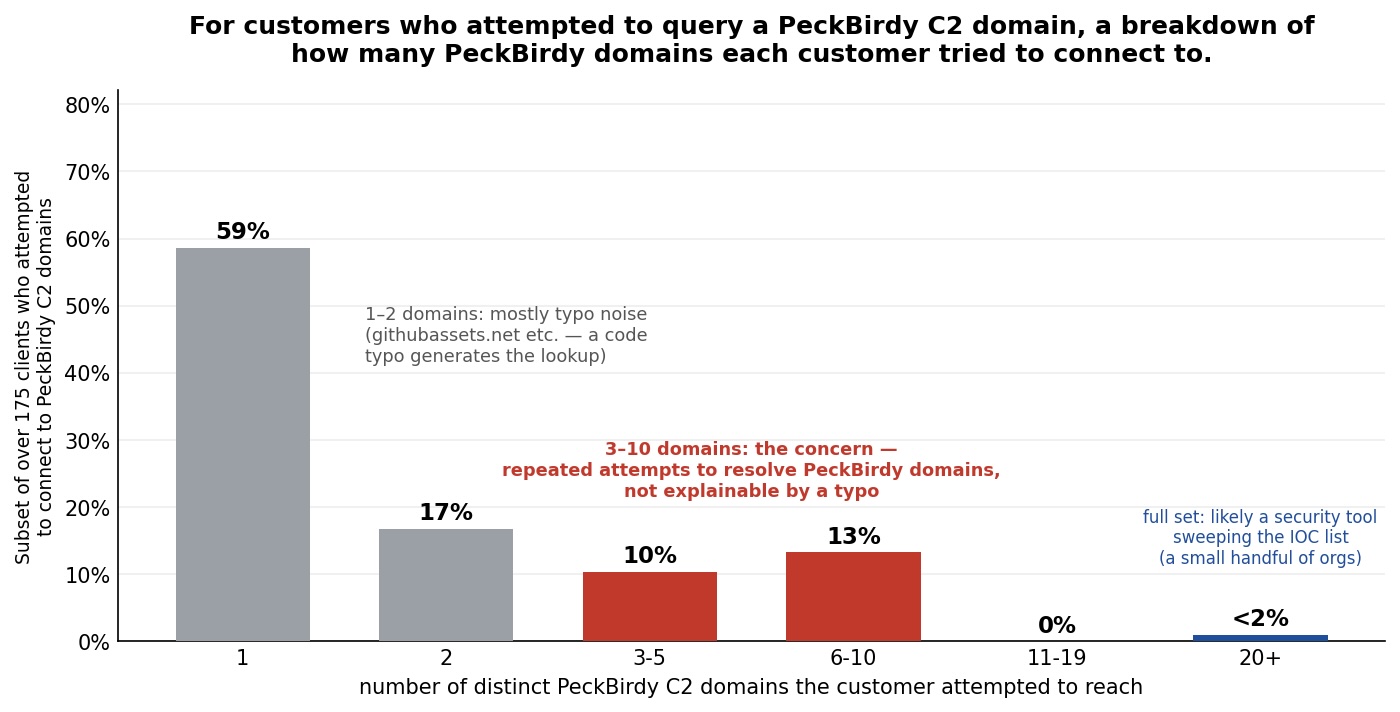
Infoblox found that just over 3% of its enterprise customers resolved at least one PeckBirdy C2 domain.
Education was a prominent sector, consistent with Trend Micro reporting on activity involving a Philippine educational institution. IT, banking, financial services and government organizations also appeared among observed targets.
A single DNS lookup is not automatically evidence of compromise. In particular, githubassets[.]net a PeckBirdy-associated typosquat can be reached through coding or typing mistakes.
However, repeated resolution of multiple distinctive PeckBirdy domains is far more concerning.
Infoblox assesses that organizations contacting between three and ten separate C2 domains may warrant incident-response investigation because such patterns are unlikely to result from accidental traffic alone.
Defenders should treat unusual casino and adult-site traffic as an intelligence lead rather than blocked web content.
Relevant hunting indicators include cache-mcp[.]com, mcp-source[.]online and historical PeckBirdy infrastructure such as cache-cdn[.]org, while recognizing that actor-controlled domains can rotate quickly.
Security teams should also review DNS telemetry for repeated lookups across multiple suspicious domains, inspect proxy and endpoint records for service-worker-delivered JavaScript, and investigate outbound WebSocket activity from devices that accessed untrusted gambling or adult sites.
Blocking by domain alone is insufficient when operators can rapidly rotate infrastructure. However, DNS detection, behavioral correlation and web-script analysis can expose the campaign’s operational pattern.
IOCs
| Category | Domains |
|---|---|
| Scambling Domains (Type 2) | dollycasino[.]comdragobet[.]netappcasino[.]online |
| Illegal Chinese-Language Casino Domains (Type 1) | 11170011[.]compuqxr[.]com80074[.]cc |
| PeckBirdy C2 and Decoy Domains (Type 3) | vip311[.]cc Decoy domaincache-cdn[.]orgcache-mcp[.]com |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
★ Learn 7 Metric-Gated AI SOC Deployment Phases – Download Free AI SOC Deployment Playbook 2026.
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.
Text extracted automatically; images, tables and formatting may be missing. Original: https://gbhackers.com/peckbirdy-malware-c2/