No signs yet of Exchange Server compromises at federal agencies, CISA says
Full article741 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
It's a welcome reprieve for federal officials trying to respond to the hacking bonanza.
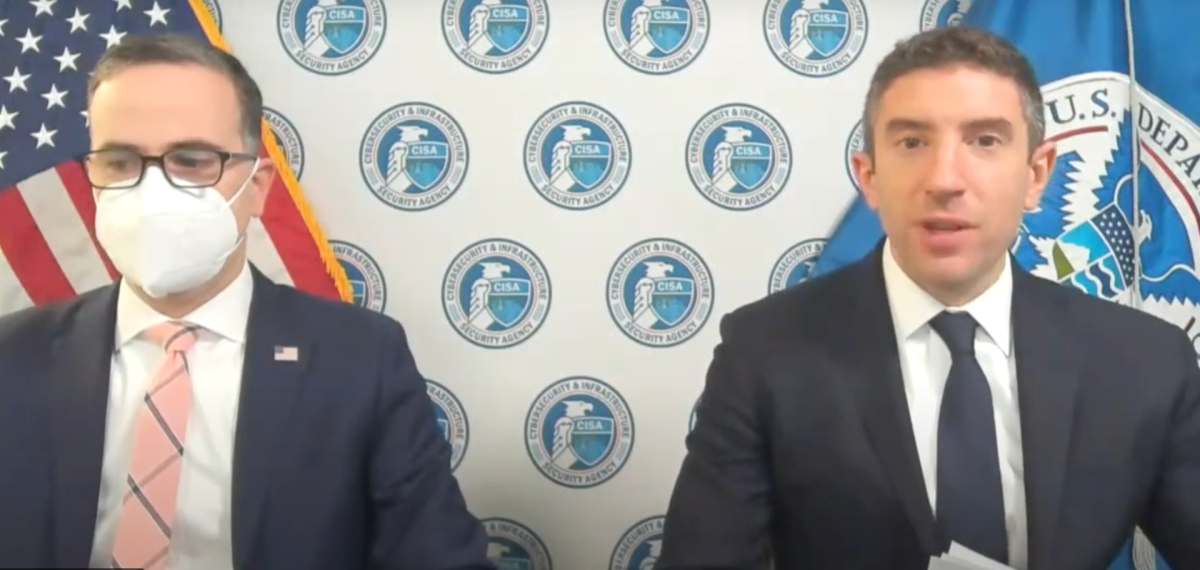
U.S. officials have yet to find any signs that federal civilian agencies have been breached in recent widespread exploitation of Microsoft software, a senior Department of Homeland Security official told lawmakers Wednesday.
The “vast majority” of civilian agencies have addressed vulnerabilities in the Exchange Server email software following an emergency directive from DHS’s Cybersecurity and Infrastructure Security Agency (CISA), said Eric Goldstein, the agency’s executive assistant director for cybersecurity. But Goldstein cautioned in testimony before a House Appropriations subcommittee that the malicious cyber activity is “an evolving campaign, with new information coming in by the hour.”
The news is a welcome reprieve for federal officials who have been consumed with responding to the critical Exchange Server flaws amid reports that tens of thousands of U.S. state and local government organizations and small businesses could be affected.
Microsoft disclosed the vulnerabilities on March 2 while accusing a Chinese government-linked hacking group of exploiting the flaws to steal emails from target organizations (Beijing denies the allegations). But the security concerns have grown more pressing since, as researchers worry that cybercriminals could take advantage of the vulnerabilities to deploy ransomware. The hacking bonanza is a global issue, with researchers reporting Wednesday that several China-linked hacking groups have exploited the bugs in campaigns on various continents.
The state and local organizations besieged by the Exchange Server vulnerabilities are often strapped for security resources needed to recover from such hacking incidents. The National Governors Association has shared information about the threat with CISA, and the association will “continue to monitor the situation and provide guidance as necessary,” an NGA spokesperson said Monday.
The Exchange Server hacking comes as federal officials are still recovering from a sweeping suspected Russian espionage campaign that exploited software made by federal contractor SolarWinds, among other vendors. Nine U.S. federal agencies have been infiltrated, according to U.S. officials, and President Joe Biden has ordered a U.S. intelligence community assessment of the breaches.
Brandon Wales, CISA’s acting director, told lawmakers Wednesday that both the supply-chain breach involving SolarWinds and the Exchange Server breaches are proof that the U.S. government “must raise our game” in cybersecurity.
“We need cybersecurity tools and services that provide us a better chance of detecting the most sophisticated attacks,” Wales said. “And we need to rethink our approach to managing cybersecurity across 101 federal civilian executive branch agencies.”
The $1.9 trillion coronavirus relief package that Congress cleared on Wednesday includes some $650 million in additional funding for CISA.
U.S. officials have previously said the hacking exploiting SolarWinds is “likely Russian in origin.” Wales said Wednesday that additional details on that attribution will be made public “soon.” Moscow has denied involvement.
Greg Touhill, a former federal chief information security officer, echoed Wales’ assessment.
“All of these things point toward the need to make zero-trust an overarching strategic initiative for this administration,” Touhill told CyberScoop, referring to a security principle that assumes networks will be breached in an effort to mitigate the damage.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/microsoft-exchange-server-china-dhs-cyber/