A Russian-speaking ransomware gang says it hacked the National Rifle Association
Full article633 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
An NRA spokesperson declined to comment when reached by phone.
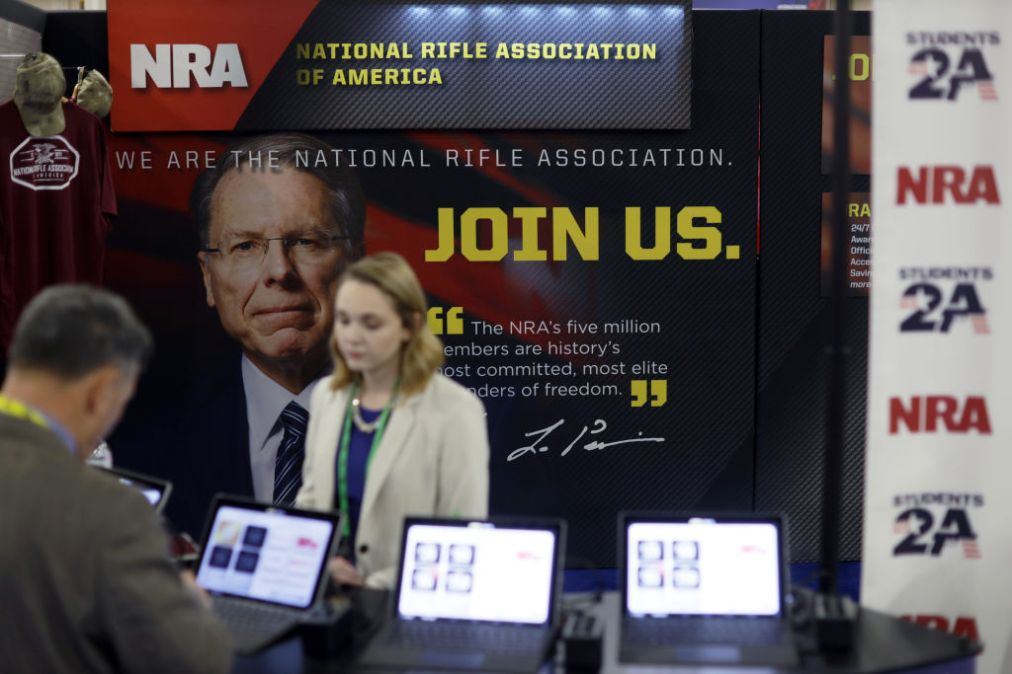
A ransomware group known as Grief claimed on Wednesday to have hacked the National Rifle Association, releasing 13 documents allegedly belonging to the organization and threatening to release more if the NRA doesn’t pay an extortion fee of an undisclosed sum.
The documents previewed on Grief’s leak site include grant applications and minutes from a meeting. The group claims to possess more documents. However, ransomware actors have been known to exaggerate the amount of data obtained in a hack.
CyberScoop has not independently verified the documents. An NRA spokesperson declined to comment when reached by phone. On its Twitter account, the NRA appeared to allude to the news.
“NRA does not discuss matters relating to its physical or electronic security. However, the NRA takes extraordinary measures to protect information regarding its members, donors, and operations – and is vigilant in doing so.”–Andrew Arulanandam, managing dir., NRA Public Affairs
— NRA (@NRA) October 27, 2021
“NRA does not discuss matters relating to its physical or electronic security,” reads a tweeted quote attributed to Andrew Arulanandam, managing director of NRA public affairs. “However, the NRA takes extraordinary measures to protect information regarding its members, donors, and operations – and is vigilant in doing so.”
Multiple researchers have said that Grief is affiliated with the Russian ransomware group Evil Corp.
Evil Corp.’s involvement could potentially put the NRA at risk of violating U.S. sanctions if it pays the attackers after the Treasury Department sanctioned that gang in 2019. The Justice Department also charged two Evil Corp. members with criminal violations, accusing the group’s leader, Maksim Yakubets, of providing direct assistance to Russian intelligence agencies.
Evil Corp. seems to have recently resurfaced in an effort to evade those sanctions with new strains of malware. The group last week reportedly hit the right-leaning U.S. broadcaster Sinclair.
Despite ongoing diplomatic efforts by the United States to pressure Russia into cracking down on ransomware gangs, ransomware from Russia-based groups continues to pose a major security threat to U.S. critical infrastructure.
Of particular concern are U.S. food and agricultural businesses. The Department of Homeland Security’s Cybersecurity and Infrastructure Security Agency, the FBI and the National Security Agency recently published a warning that another ransomware group, BlackMatter, was demanding high ransoms from victims in the industries.
Updated, 10/27/21: to include NRA tweet.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/evil-corp-nra-ransomware/