Attackers are trying to exploit old DVR vulnerabilities (CVE-2018-9995, CVE-2016-20016)
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2016-20016 | MVPower CCTV DVR models, including TV-7104HE 1.8.4 115215B9 and TV7108HE, contain a web shell that is accessible via a /shell URI. MVPower CCTV DVR models, including TV-7104HE 1.8.4 115215B9 and TV7108HE, contain a web shell that is accessible via a /shell URI. A remote unauthenticated attacker can execute arbitrary operating system commands as root. This vulnerability has also been referred to as the "JAWS webserver RCE" because of the easily identifying HTTP response server field. Other firmware versions, at least from 2014 through 2019, can be affected. This was exploited in the wild in 2017 through 2022. NVD description · AI analysis pending | 9.8 | 86% | PoC ×2 |
| — | |
| CVE-2018-9995 | TBK DVR4104 and DVR4216 devices, as well as Novo, CeNova, QSee, Pulnix, XVR 5 in 1, Securus, Night OWL, DVR Login, HVR Login, and MDVR Login, which run re-brand TBK DVR4104 and DVR4216 devices, as well as Novo, CeNova, QSee, Pulnix, XVR 5 in 1, Securus, Night OWL, DVR Login, HVR Login, and MDVR Login, which run re-branded versions of the original TBK DVR4104 and DVR4216 series, allow remote attackers to bypass authentication via a "Cookie: uid=admin" header, as demonstrated by a device.rsp?opt=user&cmd=list request that provides credentials within JSON data in a response. NVD description · AI analysis pending | 9.8 | 83% | PoC ×4 |
| — |
Full article302 words · extracted from helpnetsecurity.com · click to collapse
Five years ago, security researcher Fernandez Ezequiel discovered a vulnerability (CVE-2018-9995) in many digital video recorder (DVR) brands and released a tool for exploiting it.
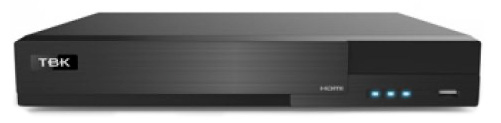
The vulnerability is still being exploited in the wild, FortiGuard Labs warns: the company’s intrusion prevention systems have registered 50,000+ unique exploitation attempts in the past month.
About CVE-2018-9995
CVE-2018-9995 is an authentication bypass vulnerability that can be triggered with a simple exploit sent via a maliciously crafted HTTP cookie to a vulnerable DVR device. The device responds by sending back the device’s admin credentials in clear text (i.e., unencrypted).
With those credentials in hand, the attacker can access the DVR device, take it over, and access to connected camera’s live video feeds.
The vulnerability was found in TBK Vision’s DVR4104 and DVR4216 devices.
“According to the NIST NVD database, TBK DVR4104 and DVR4216 devices are also rebranded and sold as other brands such as Novo, CeNova, QSee, Pulnix, XVR 5 in 1, Securus, Night OWL, DVR Login, HVR Login, and MDVR,” FortiGuard Labs pointed out.
The pool of potentially exploitable devices may be considerable.
“With tens of thousands of TBK DVRs available under different brands, publicly-available PoC code, and an easy-to-exploit makes this vulnerability an easy target for attackers. The recent spike in IPS detections shows that network camera devices remain a popular target for attacker,” the company said.
“FortiGuard Labs is not aware of any patches provided by the vendor and recommends organizations to review installed models of CCTV camera systems and related equipment for vulnerable models.”
Users can also protect their devices by limiting access to their DVR’s management interface – that is, make access possible only from specific IP addresses.
Fortinet has also noticed a spike in attempted exploitation of another old command Injection vulnerability (CVE-2016-20016), which affects MVPower digital video recorders.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.helpnetsecurity.com/2023/05/03/cve-2018-9995-cve-2016-20016/