FBI takes down one of the longest-running DDoS-for-hire services
FBI seized NightmareStresser domains, one of the longest-running DDoS-for-hire services, used in hundreds of thousands of attacks since 2022.
The FBI, together with the Royal Canadian Mounted Police, seized the domains behind NightmareStresser, a 'booter' service the DoJ says launched hundreds of thousands of actual or attempted DDoS attacks against victims worldwide since 2022. Victims allegedly included educational institutions, government agencies, gaming platforms and millions of individuals. The action falls under Operation PowerOFF, an ongoing international effort under which prosecutors have charged twelve defendants and seized more than 100 DDoS-for-hire domains over the past eight years.
- Seizure conducted with RCMP under Operation PowerOFF
- Hundreds of thousands of DDoS attacks launched since 2022
- Victims included schools, government agencies and gaming platforms
- Twelve defendants charged and 100+ domains seized over eight years
Full article281 words · extracted from helpnetsecurity.com · click to collapse
The FBI has seized the domains behind NightmareStresser, a DDoS-for-hire service officials call one of the longest running “booter” operations in existence.
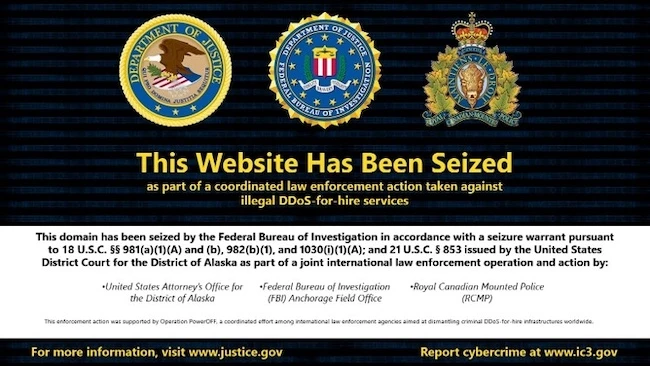
The domain seizure notice (Source: US Department of Justice)
“Booter services such as those named in this action allegedly facilitate attacks on a wide array of victims in the United States and abroad, including educational institutions, government agencies, gaming platforms and millions of people,” US DoJ said in its announcement.
These attacks are called booting because they result in the dropping of the targeted computer from the internet.
According to the seizure warrant affidavit, NightmareStresser was used to launch hundreds of thousands of actual or attempted DDoS attacks against victims worldwide since 2022.
“This operation, in coordination with other international law enforcement actions, is intended to disrupt the infrastructure used by the NightmareStresser service to facilitate attacks on victims in the District of Alaska and across the United States,” US DoJ noted.
Over the past eight years, prosecutors and investigators in Anchorage and Los Angeles have charged twelve defendants for running DDoS-for-hire services and seized more than 100 domains connected to them.
“The multi-prong investigation announced today builds on the success of the prior cases by targeting all known booter sites, shutting down as many as possible, and undertaking a public education campaign,” prosecutors added.
The FBI’s Anchorage Field Office carried out the seizure with the Royal Canadian Mounted Police, Federal Policing Northwest Region, under Operation PowerOFF, an ongoing international effort to dismantle DDoS-for-hire infrastructure and hold administrators and users of these services accountable.
Cloudflare’s H1 2026 DDoS Threat Report found that DDoS-for-hire platforms, hijacked IoT devices, and automated tools keep lowering the barrier for launching large-scale attacks.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.helpnetsecurity.com/2026/09/17/fbi-nightmarestresser-ddos-for-hire-service-seized/