Mulvaney: CFPB hit by over 200 data 'lapses'
Full article717 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Mick Mulvaney revealed Thursday that the agency had suffered some 240 “lapses” in data security over an unspecified time period, in addition to a suspected 800 other such incidents.
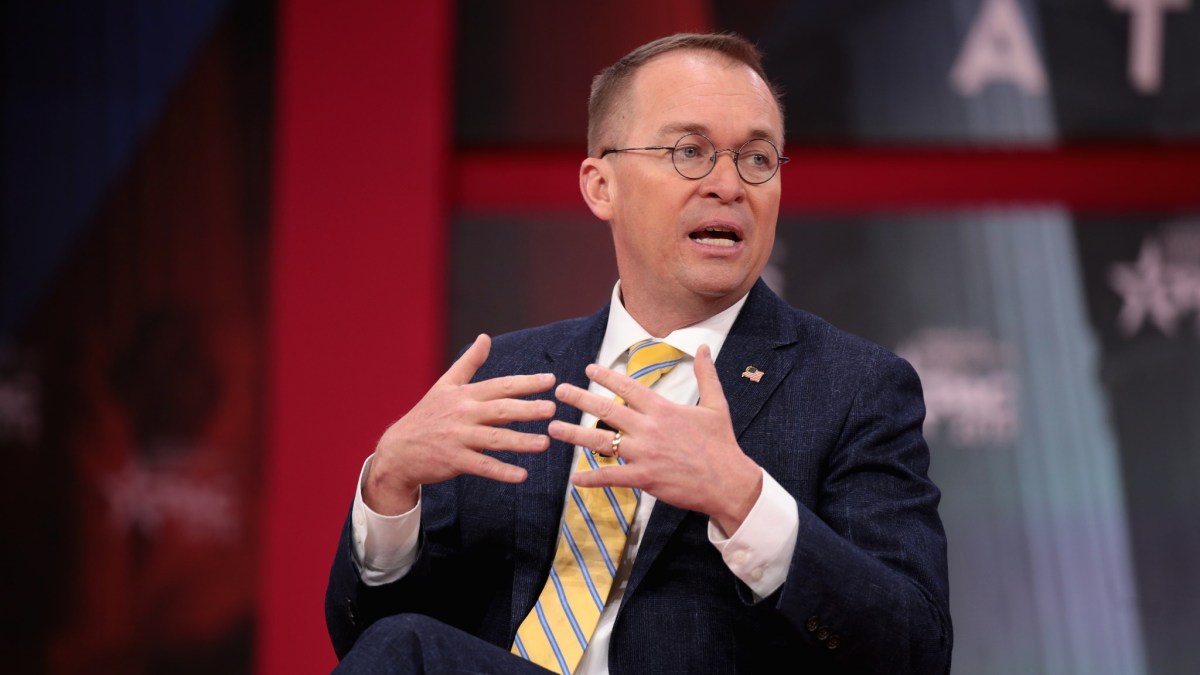
The head of the Consumer Financial Protection Bureau said Thursday that the agency had suffered some 240 “lapses” in data security over an unspecified time period, in addition to a suspected 800 other such incidents.
“We have been able to document about 200-odd – I think 240 – lapses in our data security,” acting CFPB Director Mick Mulvaney told the Senate Committee on Banking, Housing, and Urban Affairs during a hearing on the bureau’s semi-annual report to Congress.
“Lapses – is that a breach?” Sen. David Perdue, R-Ga., asked Mulvaney during a tense exchange.
“I think data got out that should not have gotten out,” Mulvaney replied, adding, “there’s another 800 [incidents] that we suspect that we haven’t been able to confirm.”
As part of its mandate to protect consumers, the CFPB has the right to collect data on credit card transactions, mortgages, and car loans, Mulvaney said.
“Everything that we keep is subject to being lost,” added Mulvaney, who is also the director of the White House Office of Management and Budget.
He consulted with an aide during the hearing to confirm that some of his agency’s data is stored by third parties.
Perdue requested a classified briefing on the subject and Mulvaney said he would be willing to provide one.
Since the seminal 2015 breach of the Office of Personnel Management, in which the personal information of some 22 million Americans was compromised, U.S. lawmakers and agencies have woken up to the threat of large-scale espionage via data theft.
In September, credit reporting company Equifax disclosed that hackers had breached the personal information, including Social Security numbers, of more than 140 million consumers in the United States.
UPDATE: A CFPB spokesperson provided the following statement to CyberScoop:
“Prior to Acting Director Mulvaney’s appointment (in November 2017), there were 233 confirmed breaches of consumer personally identifiable information (PII) within the Bureau’s Consumer Response system by the Bureau or its contractor, and at least another 840 suspected PII breaches by financial institutions using the company portal.”
More Scoops
CFPB to withdraw rule targeting data brokers
The Trump administration’s CFPB nominee spoke positively in February about the Biden-era rule to regulate the sale of Americans’ personal data, but he is now slotted instead…
CFPB nominee signals openness to continuing data-broker work

CFPB proposes new rule to regulate expansive data broker industry
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/mick-mulvaney-cfpb-data-breach/