AVAR, China and insecure Wi
Full article397 words · extracted from securelist.com · click to collapse


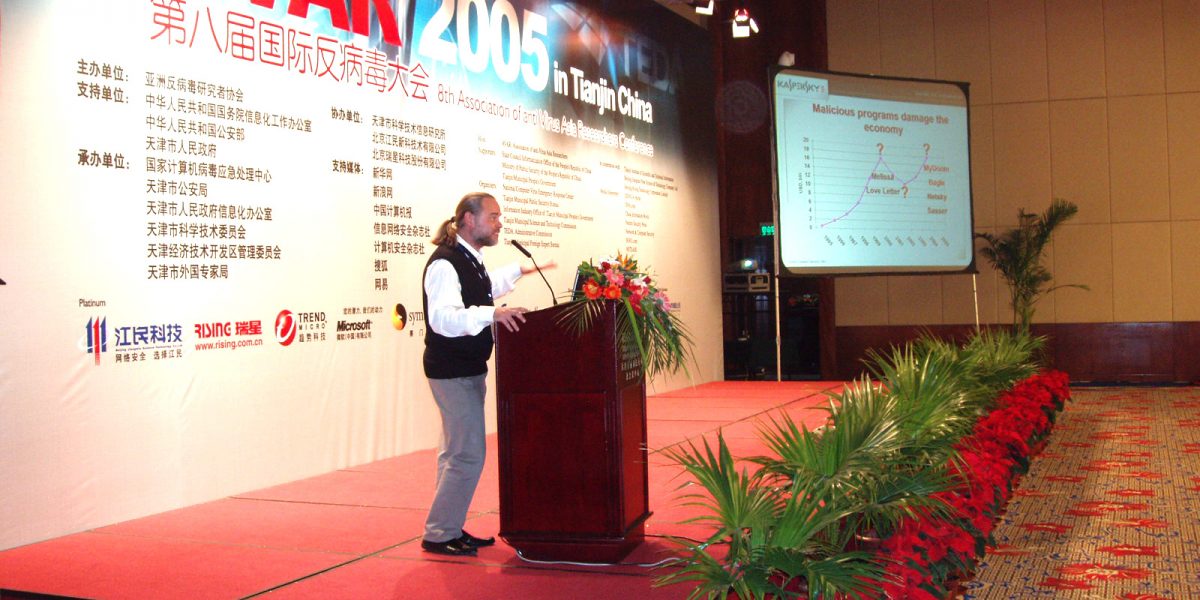
Hello from Tianjin in China, and the AVAR 2005 conference. We’re 150km from Peking, near the Bohai sea. This year’s conference is the eighth annual event for virus analysts from the Asian region, and it’s one of the highlights of an antivirus researcher’s calendar, together with VB, CARO and EICAR.
This year attendance is good, with leading virus analysts along with IT industry people and government officials. For instance, speakers include Dmitry Gryaznov and Igor Muttik from McAfee, Vesselin Bontchev from Frisk and Eugene from…well, we know where he’s from.
There are also speakers from the Chinese Ministry of the Interior, which has done a lot in the past few years to combat cyber crime.
Eugene’s presentation was greeted enthusiastically and there were lots of questions. While he was speaking, I started doing a bit of research. I wanted to check out the wireless Internet connections, as well as mobile devices.
I found 3 WiFi-networks straight away. None of them encrypted traffic, but all of them had built-in DHCP servers. In short, all 3 were potentially vulnerable to war drivers. By the way, tomorrow I’m going to scan other WiFi networks in Tianjin and Peking.
Next I took a Bluetooth transmitter with a 100 meter radius and walked around the conference hall scanning for Bluetooth devices in ‘visible to all’ mode. I found plenty:
Overall, I found 9 mobile devices with Bluetooth ‘visible to all’ mode enabled, 8 of them Nokia smartphones. Yes, I know. You’d think that people attending an antivirus conference would know better. In fact, I had been hoping that I wouldn’t find any at all.
The good news is that none of the phones were infected with Cabir. At least, not yet…
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/avar-china-and-insecure-wi-fi-networks/30092/