Trump administration picks new leader for Vulnerabilities Equities Process board
Full article576 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
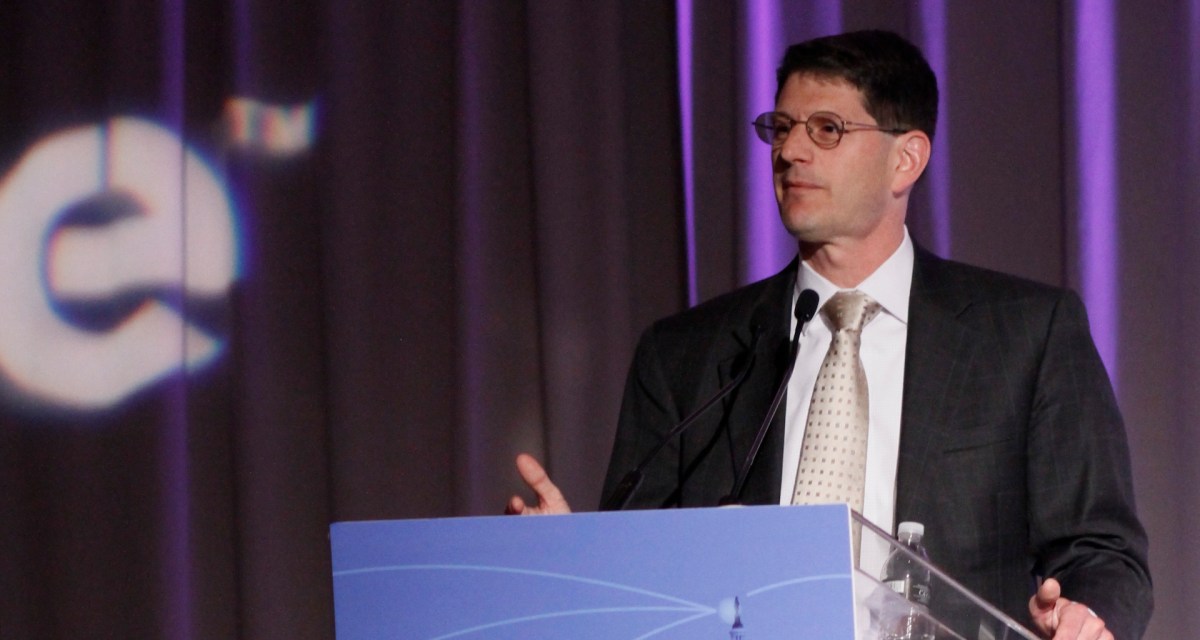
Grant Schneider has been named chair of the Vulnerability Equities Process board.
The White House has selected a new leader to head a secretive government group that helps decide which software vulnerabilities should be kept for intelligence gathering purposes or widely released to the public.
Grant Schneider, the National Security Council’s senior director for cybersecurity policy, has been named chairman of the Vulnerability Equities Process (VEP) board, an NSC spokesperson told CyberScoop. Schneider is also currently serving as the acting federal chief information security officer.
His appointment comes as recent White House Cybersecurity Coordinator Rob Joyce left 1600 Pennsylvania Avenue in May. He is now serving as a senior adviser at the National Security Agency.
Joyce was instrumental in a public charter released last year that brought transparency to the VEP, by which the U.S. government determines to either withhold or disclose information to tech companies about newly discovered flaws in their software. The charter originally named Joyce as the head of the multi-agency Equities Review Board (ERB), which weighs in on such decisions. But with Joyce’s departure, the administration needed to select a new leader from within the NSC.
A longtime civil servant, Schneider is widely respected in the federal IT community. Before joining the White House, he served in various information security roles at the Office of Personnel Management, Office of Management and Budget and Defense Intelligence Agency.
Over the last year, Schneider has also played a significant role in executing Trump’s cybersecurity executive order which calls on federal agencies to improve their digital defenses.
Aspects of the VEP framework, a previously classified document, first became public in 2016 when a Freedom of Information Act request by the Electronic Frontier Foundation unearthed a redacted version.
The ERB includes representation from multiple relevant agencies, including the CIA, FBI, Treasury Department, State Department, Justice Department and Homeland Security Department, among others. Typically, when an agency secretly discovers a software flaw and wants to keep it for espionage purposes, they’re supposed to bring it to the ERB for consideration. While these undisclosed vulnerabilities can provide the U.S. government with special access to specific targets, they also leave companies susceptible to cyberattacks.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/grant-schneider-vulnerabilities-equities-process/