Hello from CeBIT 2008!
Full article273 words · extracted from securelist.com · click to collapse

If you’re in the Hannover neighbourhood, or if you’re at CeBIT already, don’t forget to stop at our booth in Hall 6, J16 before it’s too late.
Everyone seems to be rushing to our booth to get a copy of Eugene’s latest book called ‘Malware’. It gives a complete overview of all aspects of malware, including all the history, and it’s a real page turner. In my opinion it’s a ‘must have’ for your security library.
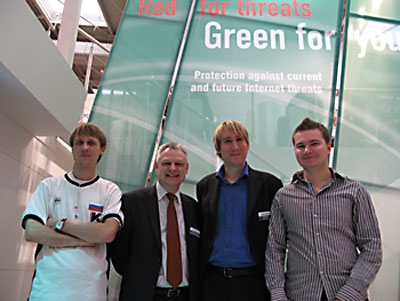
Yesterday we had our now traditional Russian disco evening and stayed up a bit later than we should have done. But if you take a look at the picture below you can see we’re still in great shape and ready to kick off the CeBIT Kaspersky Analysts Roundtable within the next hour!
From left to right: Alex, Eddy, Magnus, Vitaly
Incidentally, the big theme over here at CeBIT is ‘green IT’. We must be ahead of the times – we’ve had a green product for years!
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/hello-from-cebit-2008/30396/