Rep. Katko introduces bill that would prioritize security for key US critical infrastructure
Full article1,040 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Data breaches at a pipeline operator and fuel supplier briefly rattled U.S. supply chains earlier this year.
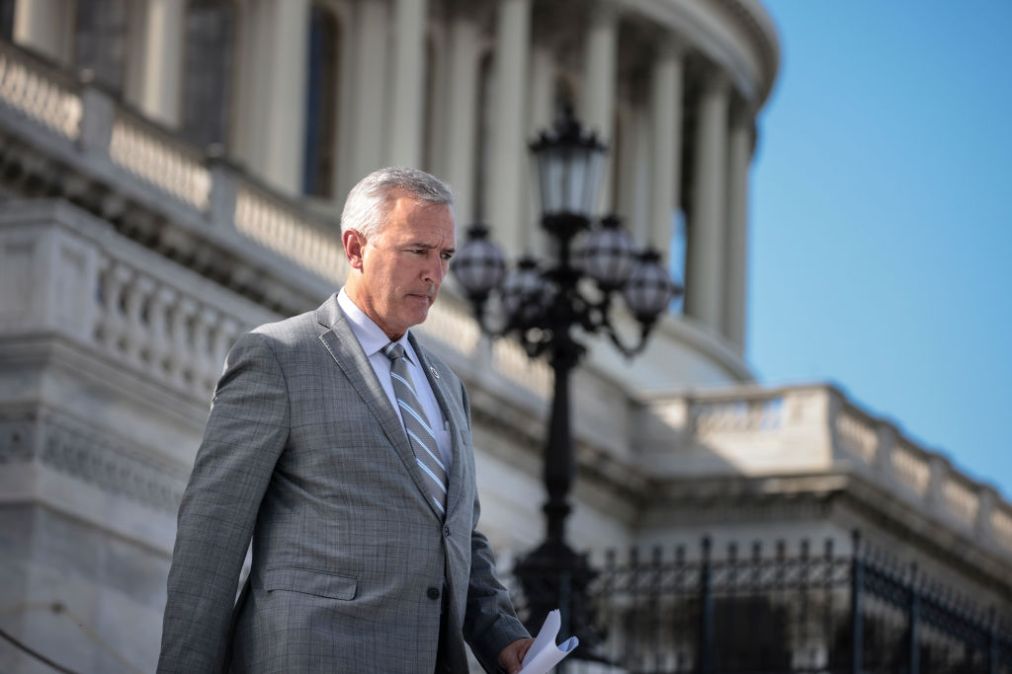
The top Republican on the House Homeland Security Committee introduced legislation Tuesday directing the Homeland Security Department’s cyber wing to identify U.S. digital infrastructure that, if attacked, would severely debilitate national security, economic security or public safety.
Under the legislation from Rep. John Katko, R-N.Y., DHS’ Cybersecurity and Infrastructure Security Agency would designate the nation’s “systemically important critical infrastructure” (or “SICI”). The legislation also would make it a priority for CISA to lend its protective services, such as continuous monitoring and detection of cybersecurity risks, to the identified owners and operators.
It’s an attempt, Katko said, identify which of the 16 sectors currently labeled as critical infrastructure are truly essential.
“To mitigate risks to our economic and national security going forward, we need a clear process for identifying which infrastructure constitutes systemically important critical infrastructure,” Katko said in announcing the legislation. “Disruption to this infrastructure — ranging from pipelines to software — could have an outsized impact on our homeland security.”
The proposal comes after numerous hacks that rattled U.S. supply chains. A May ransomware attack against Colonial Pipeline, a pipeline operator that moves 100 million in fuel across parts of the U.S., sparked panic-buying, resulting in gas shortages in some states. Another intrusion at JBS, a meat production conglomerate, led to tightening in meat supplies at a limited number of American grocers.
The Katko bill is a legislative take on one of the outstanding recommendations of the Cyberspace Solarium Commission, an intergovernmental body created in 2019 to examine ways of improving America’s digital reslience, albeit with a notable omission. The commission’s proposal recommended that SICI owners and operators would receive a mix of federal “benefits and burdens,” with possible burdens to include mandatory security standards and reporting of cyberattacks. The draft Katko bill, co-sponsored by Rep. Abigail Spanberger, D-Va., excludes the “burdens” piece of the commission’s recommendation.
The idea of government requirements in SICI legislation had unnerved industry groups that are rarely inclined to embrace federal commandments.
A committee aide told reporters that it the exclusion was more a matter of timing. “The opportunity to achieve the identification process is simply too urgent to wait around” for developing a system of “burdens,” the aide said.
“Our goal right now is identify SICI, and then identify ways to better prioritize CISA’s limited resources to bolster the common defense of the entities that operate SICI, ultimately for the benefit of Americans,” the aide said. “There may be folks that want to build on that later.”
It’s the second major bill on SICI to debut in Congress this year, but the first in the House. In July, Sens. Angus King, I-Maine, and Mike Rounds, R-S.D. introduced sweeping cybersecurity legislation that includes SICI provisions.
“In recent months, we’ve seen our gas pipelines, food system, water systems, and more hacked and attacked — and those are just the incidents that rose to widespread awareness,” King said in announcing the legislation. “These intrusions have made one thing crystal clear: America’s critical infrastructure is dangerously vulnerable to cyber disaster.”
That bill would direct DHS to develop a plan for protecting SICI, which would include conducting an assessment of options for improving protections via both government benefits and potential performance-based standards or regulations.
The House Homeland Security Committee plans to soon hold a closed-door roundtable to explore SICI legislation, the committee aide said.
It’s the latest bill in a productive stretch for Congress on introducing cybersecurity measures. On Monday, the leaders of the Senate Homeland Security and Governmental Affairs Committee introduced legislation to overhaul the Federal Information Security Security Modernization Act to require agencies to alert Congress within five days if they’re breached.
That follows bills in both the House and Senate that would establish requirements for critical infrastructure owners and others to report major cybersecurity incidents to CISA.
More Scoops
House intel bill includes provisions on state and local threat intelligence, election security, AI
The House Intelligence Committee advanced its fiscal 2027 authorization legislation Monday.
Congress looks to revive critical cyber program for rural electric utilities
National cyber director says U.S. needs to counter Chinese surveillance, push American tech
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/katko-sici-cisa-cyberspace-solarium-commission/